Integrating Microsoft Entra ID with Keycloak for MTG CLM Authentication
This guide walks you through configuring Microsoft Entra ID (formerly Azure AD) as an identity provider for Keycloak, enabling single sign-on for MTG CLM users.
Prerequisites: Microsoft Entra ID administrative privileges, Keycloak administrative access, and MTG CLM environment access.
Creating the App Registration in Entra ID
To allow Keycloak and MTG CLM to authenticate users against your Microsoft environment, you must first register an application in your Entra ID tenant.
-
Log in to Azure Portal 🔗.
-
Click the hamburger button on the top left corner.
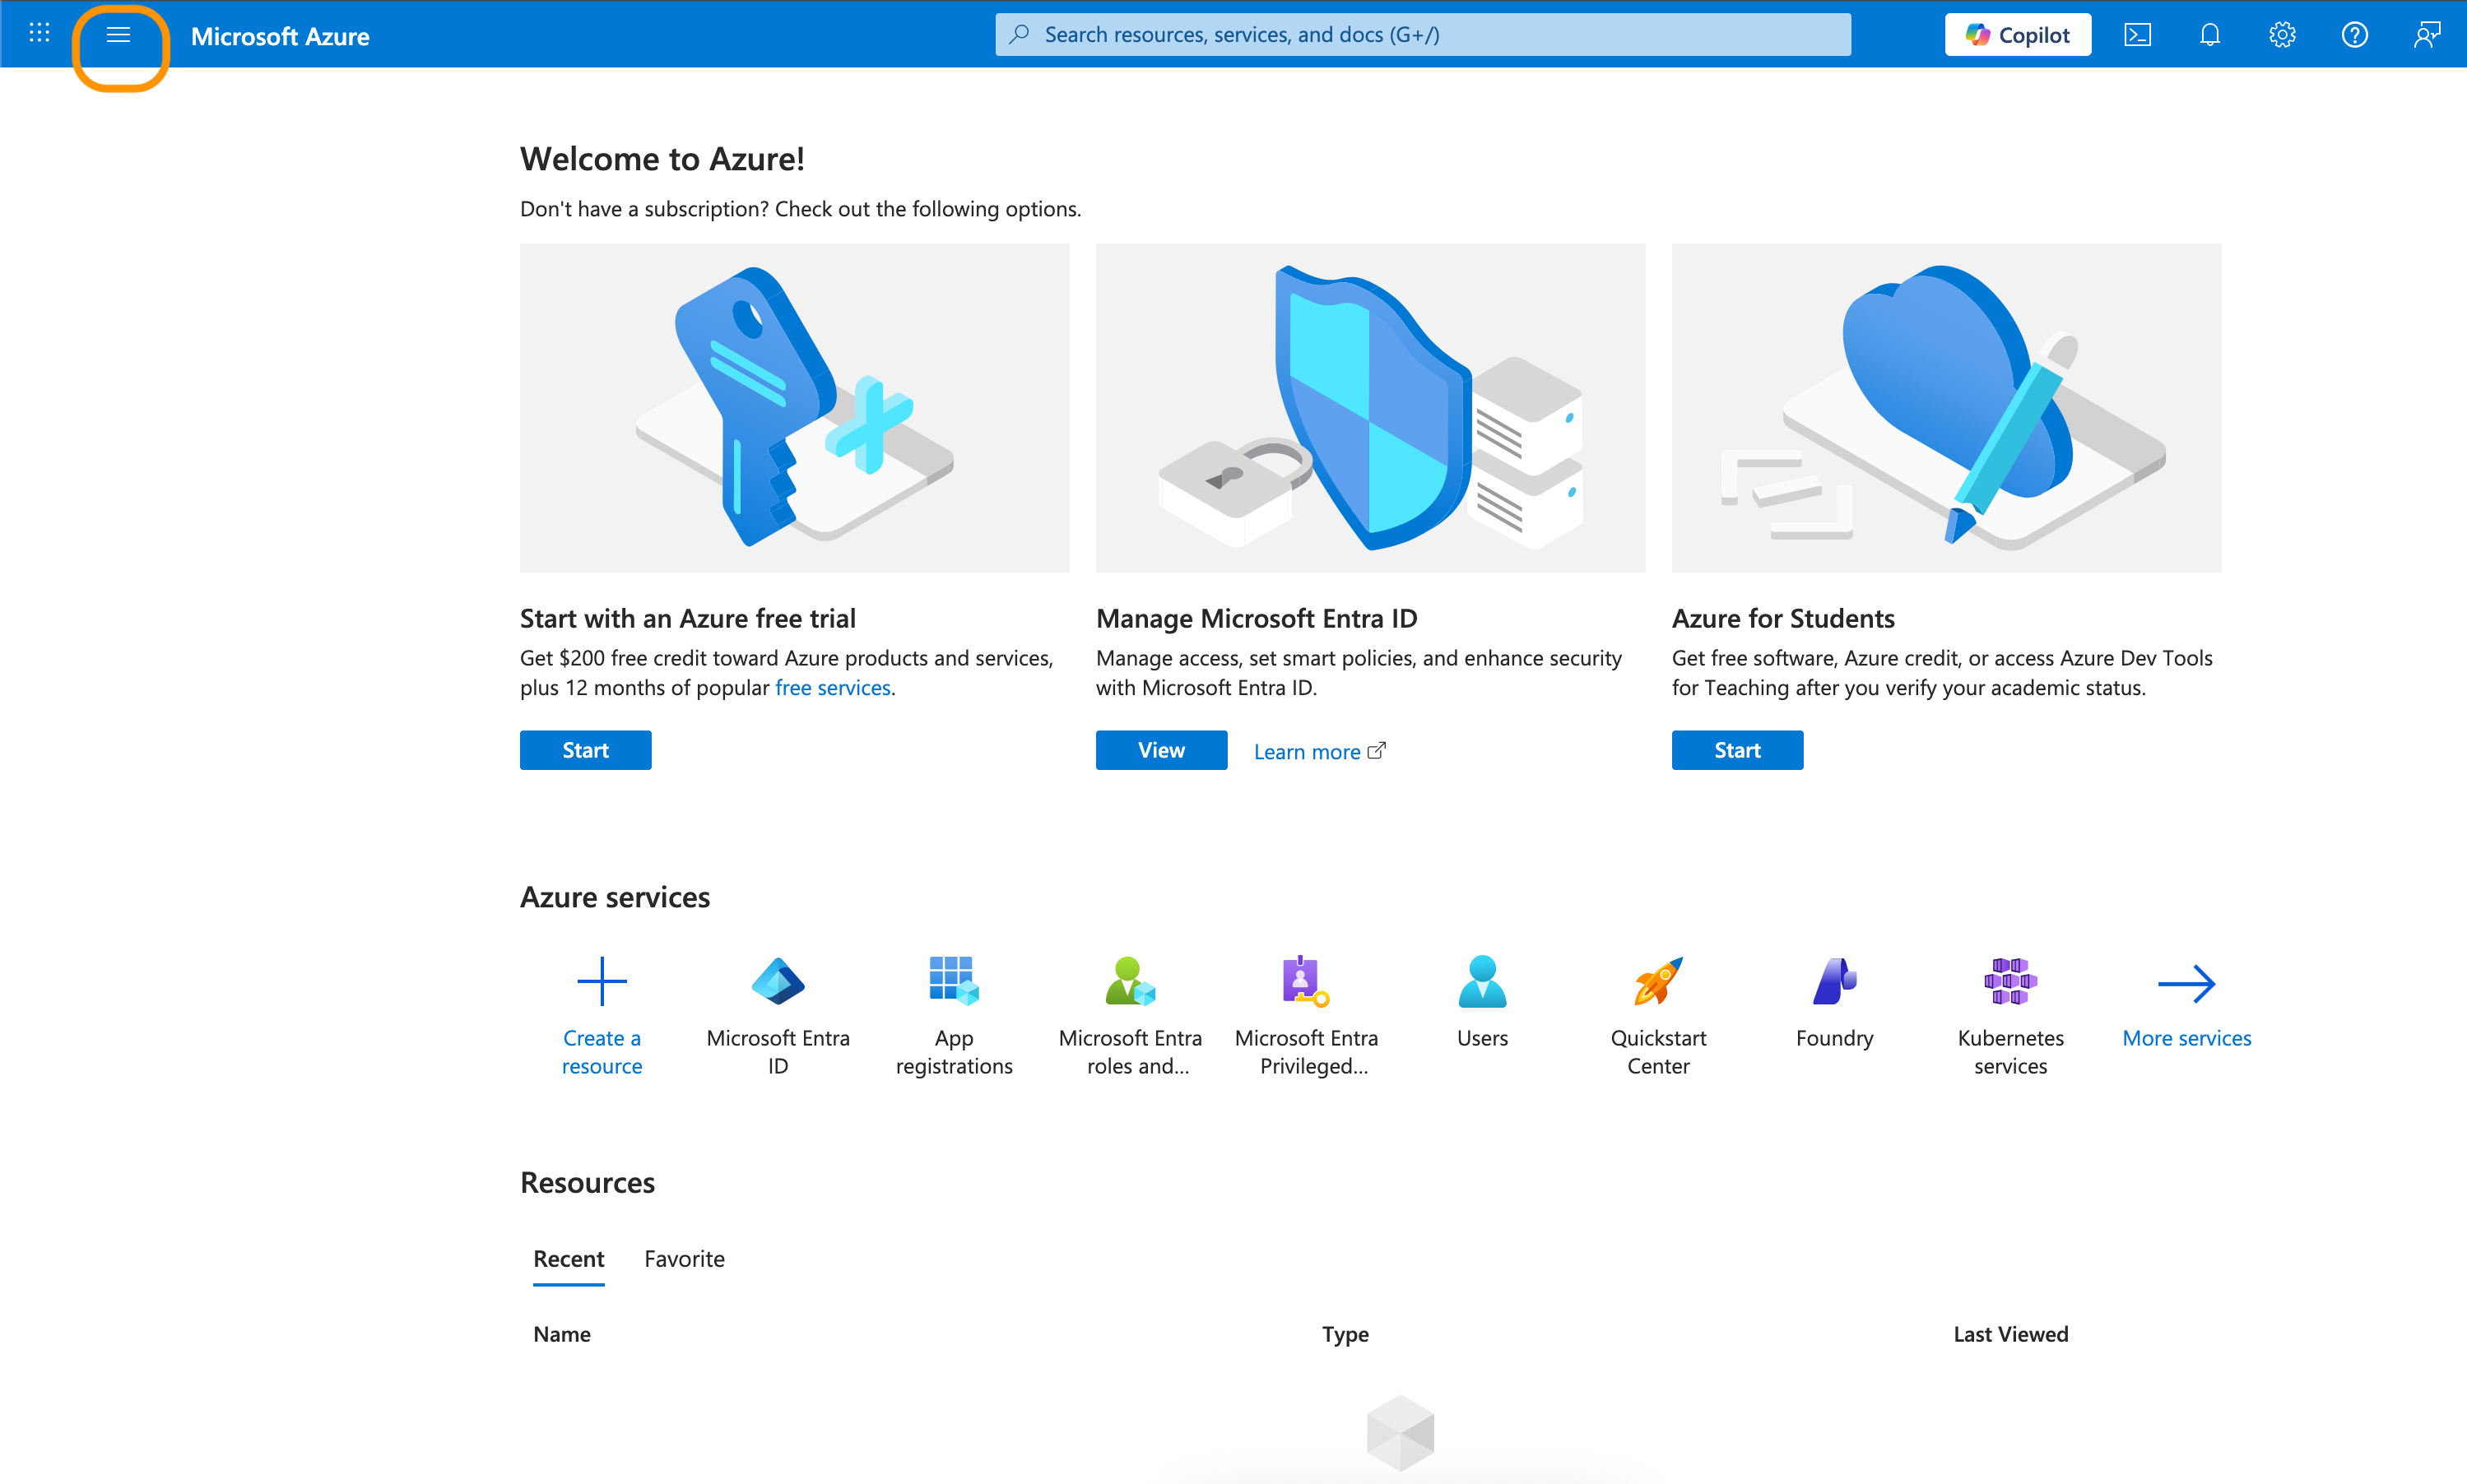
-
Select Microsoft Entra ID.
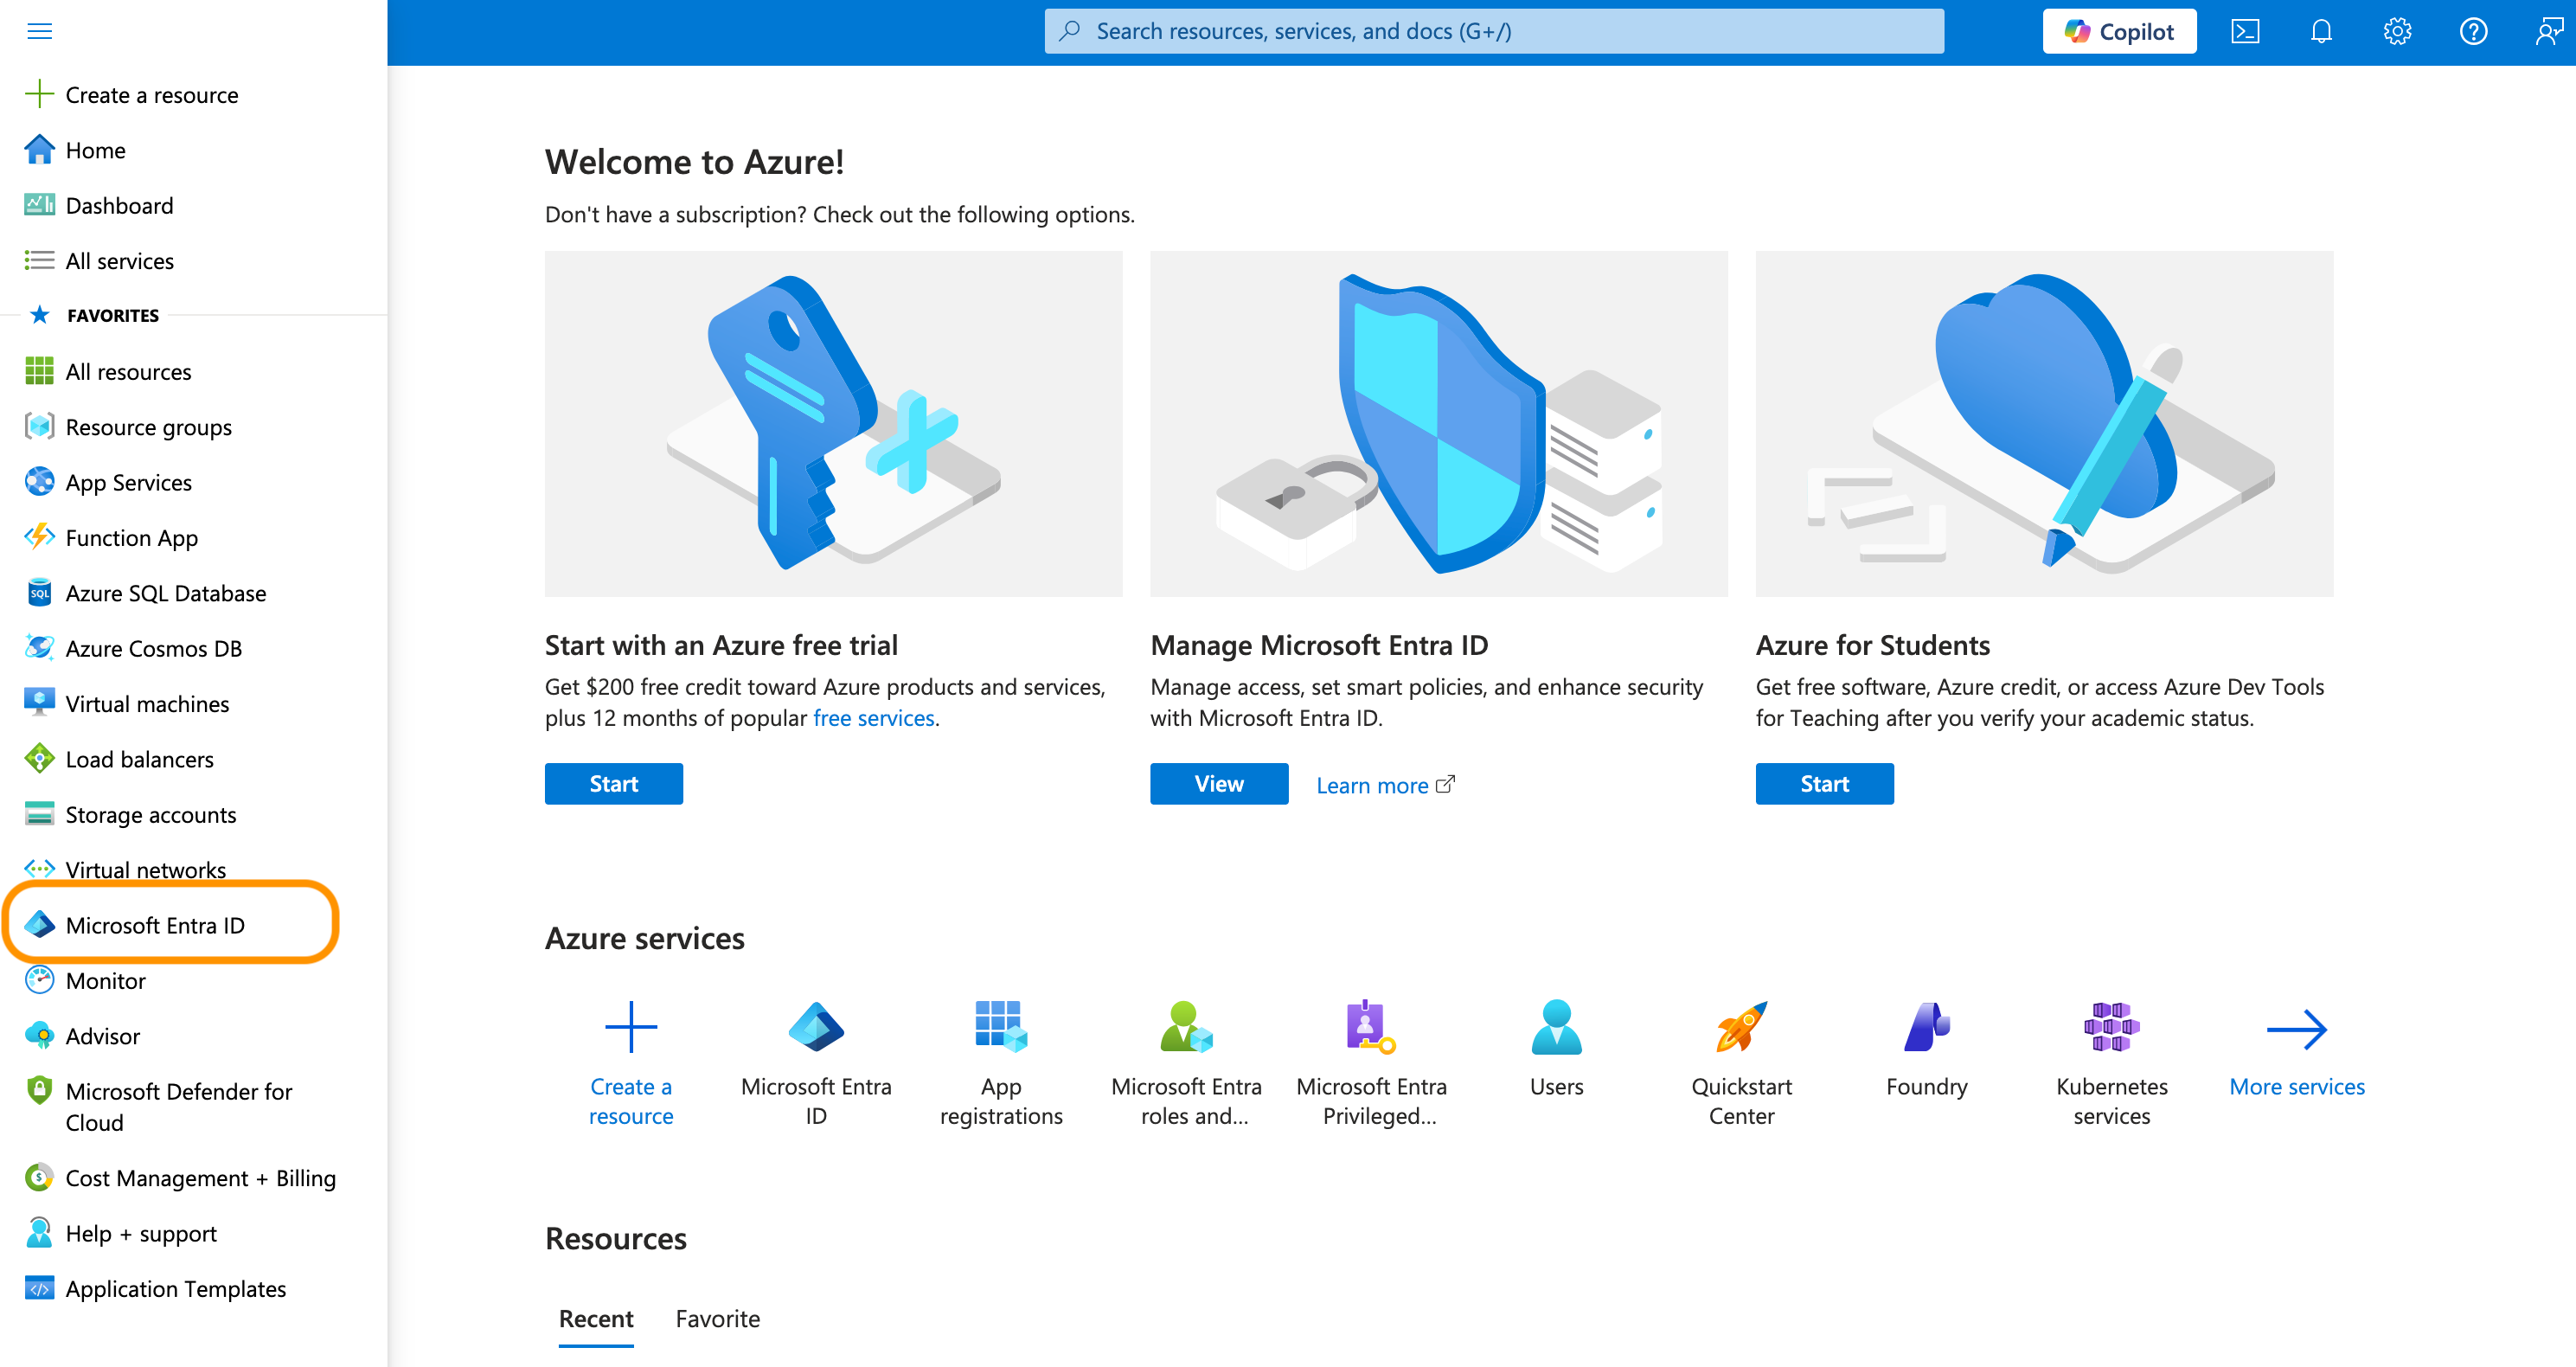
-
Click + Add and then App Registration.
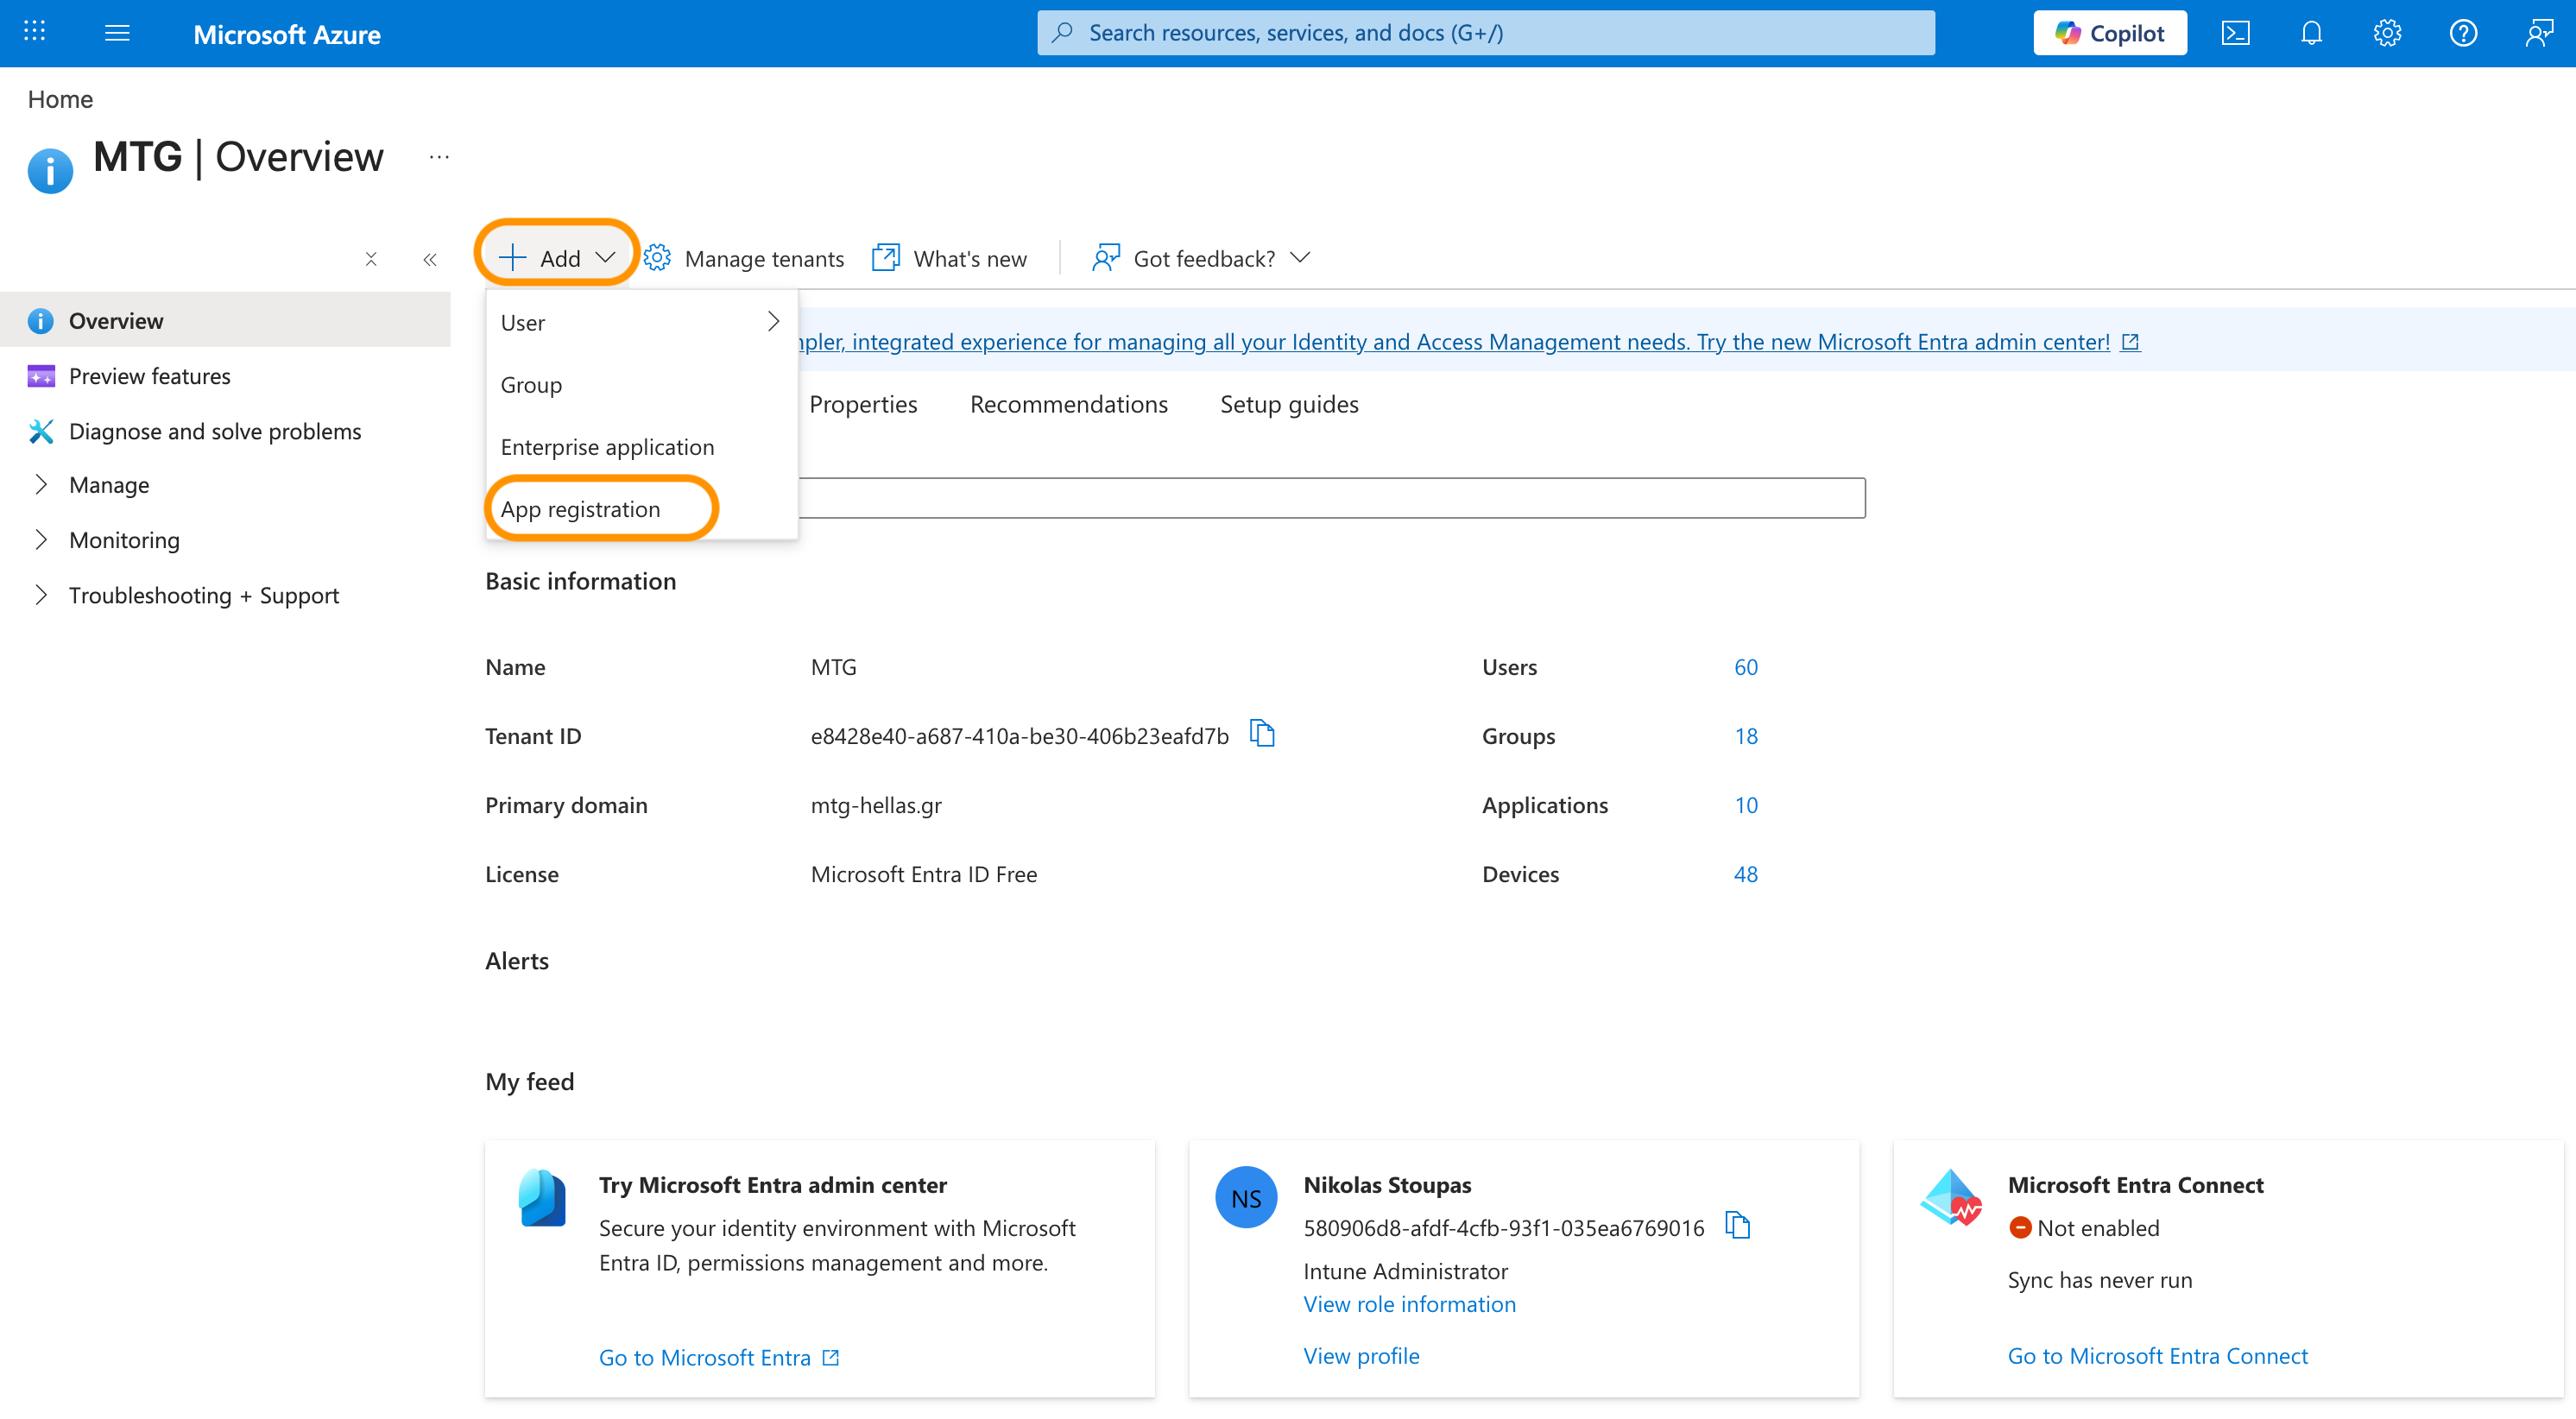
-
Enter a descriptive Name for the application (e.g., MTG CLM - Keycloak).
-
Under Supported account types, select Single tenant only.
-
Leave the Redirect URI blank for now. You will configure this later when setting up Keycloak.
-
Click Register.
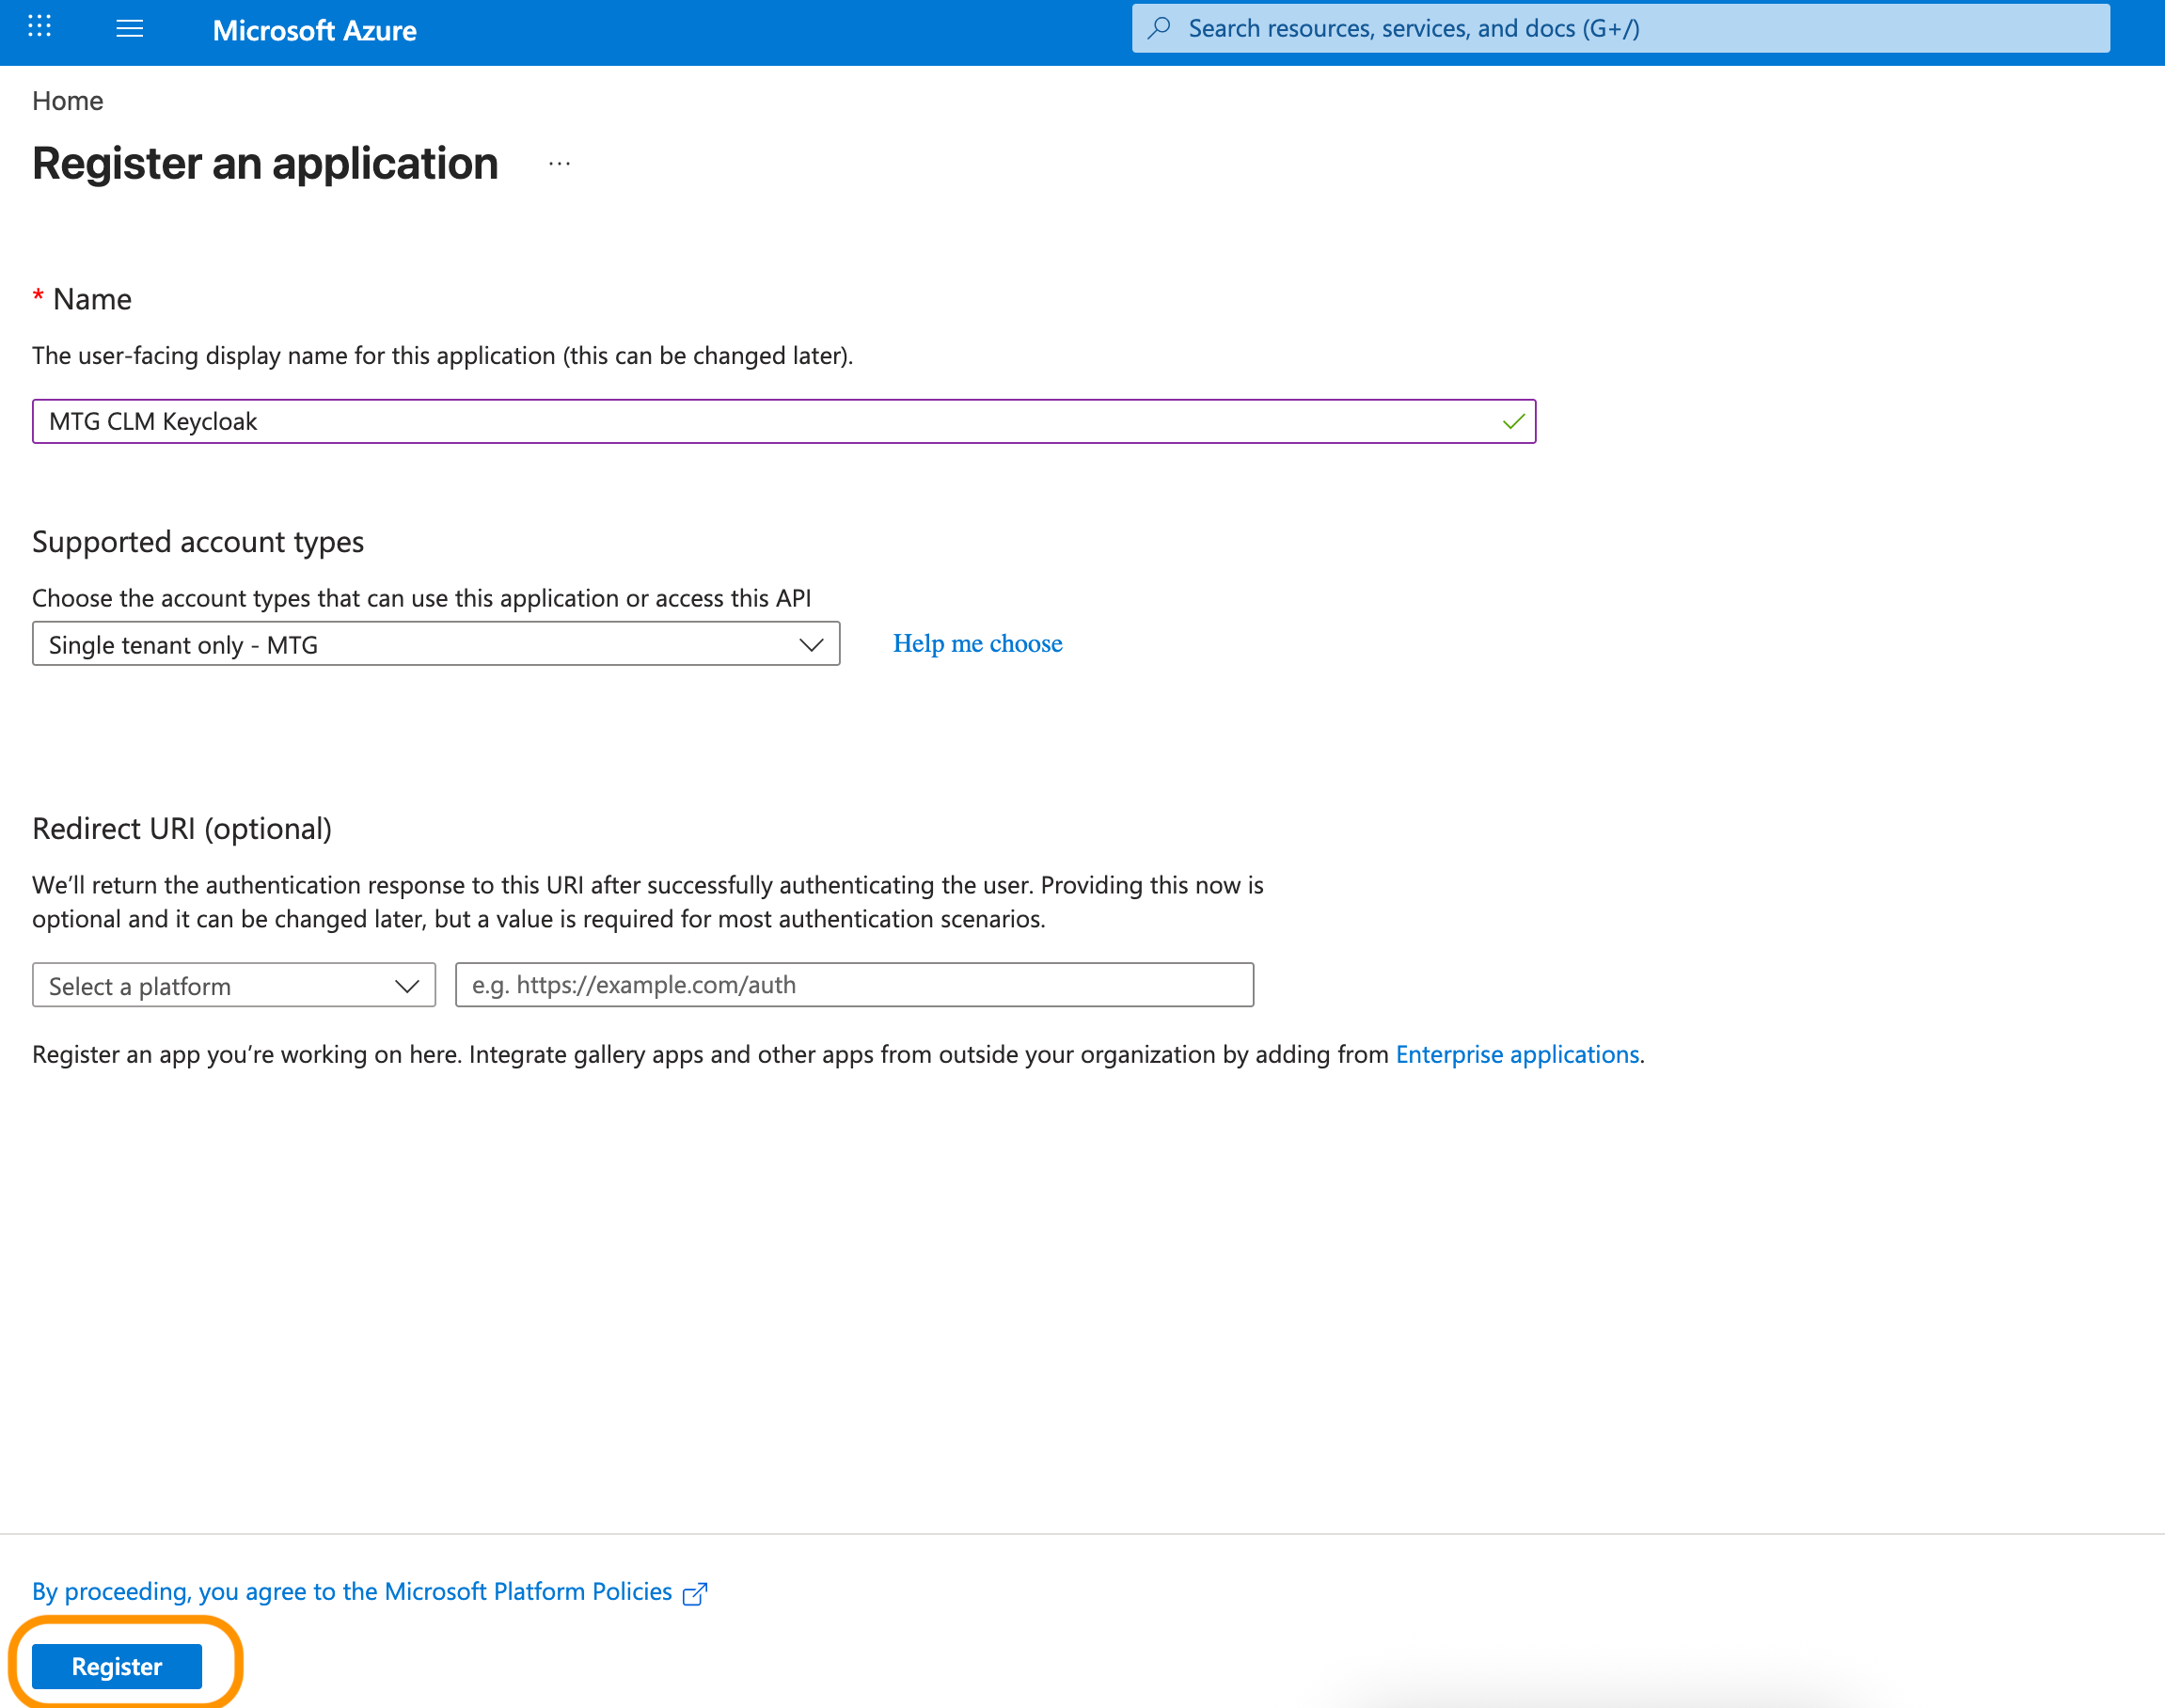
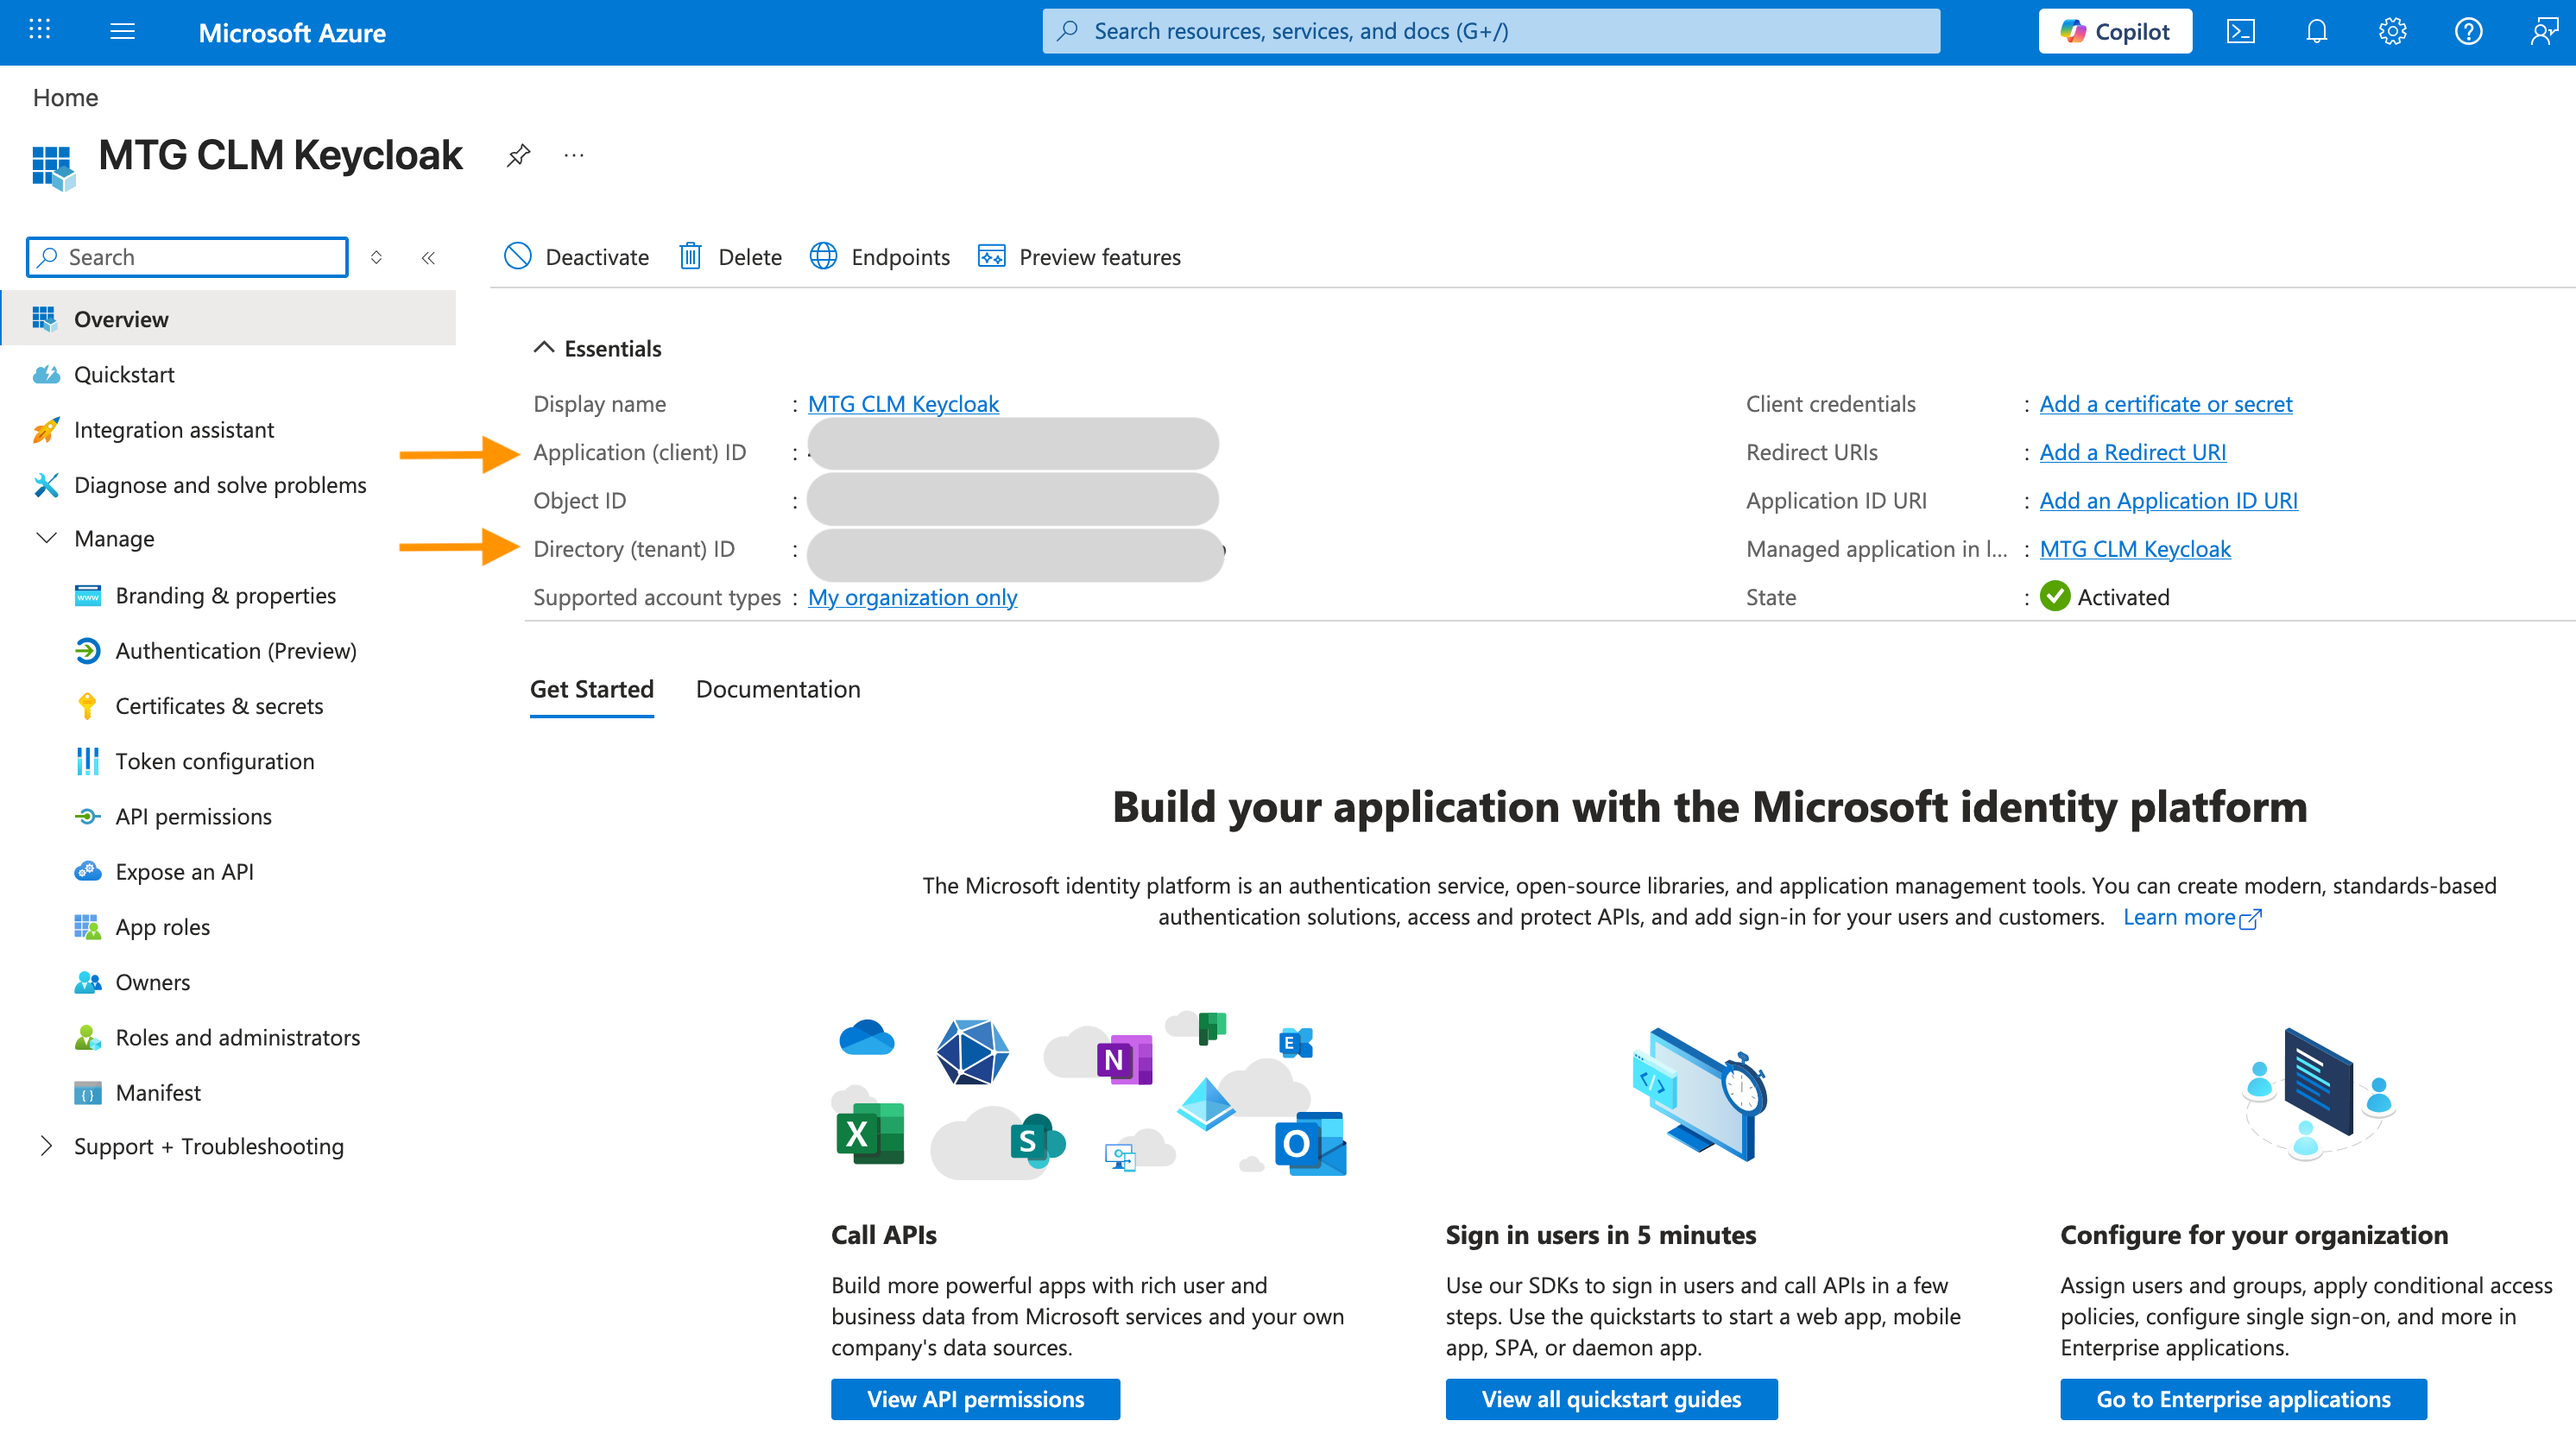
Once the application is created, you are taken to the Overview page.
Copy and securely store the following two values, as you will need them for the Keycloak configuration:
-
Application (client) ID
-
Directory (tenant) ID
Configuring API Permissions and Admin Consent
To allow MTG CLM to read user and directory objects within your tenant, you must grant the App Registration specific Microsoft Graph API permissions.
-
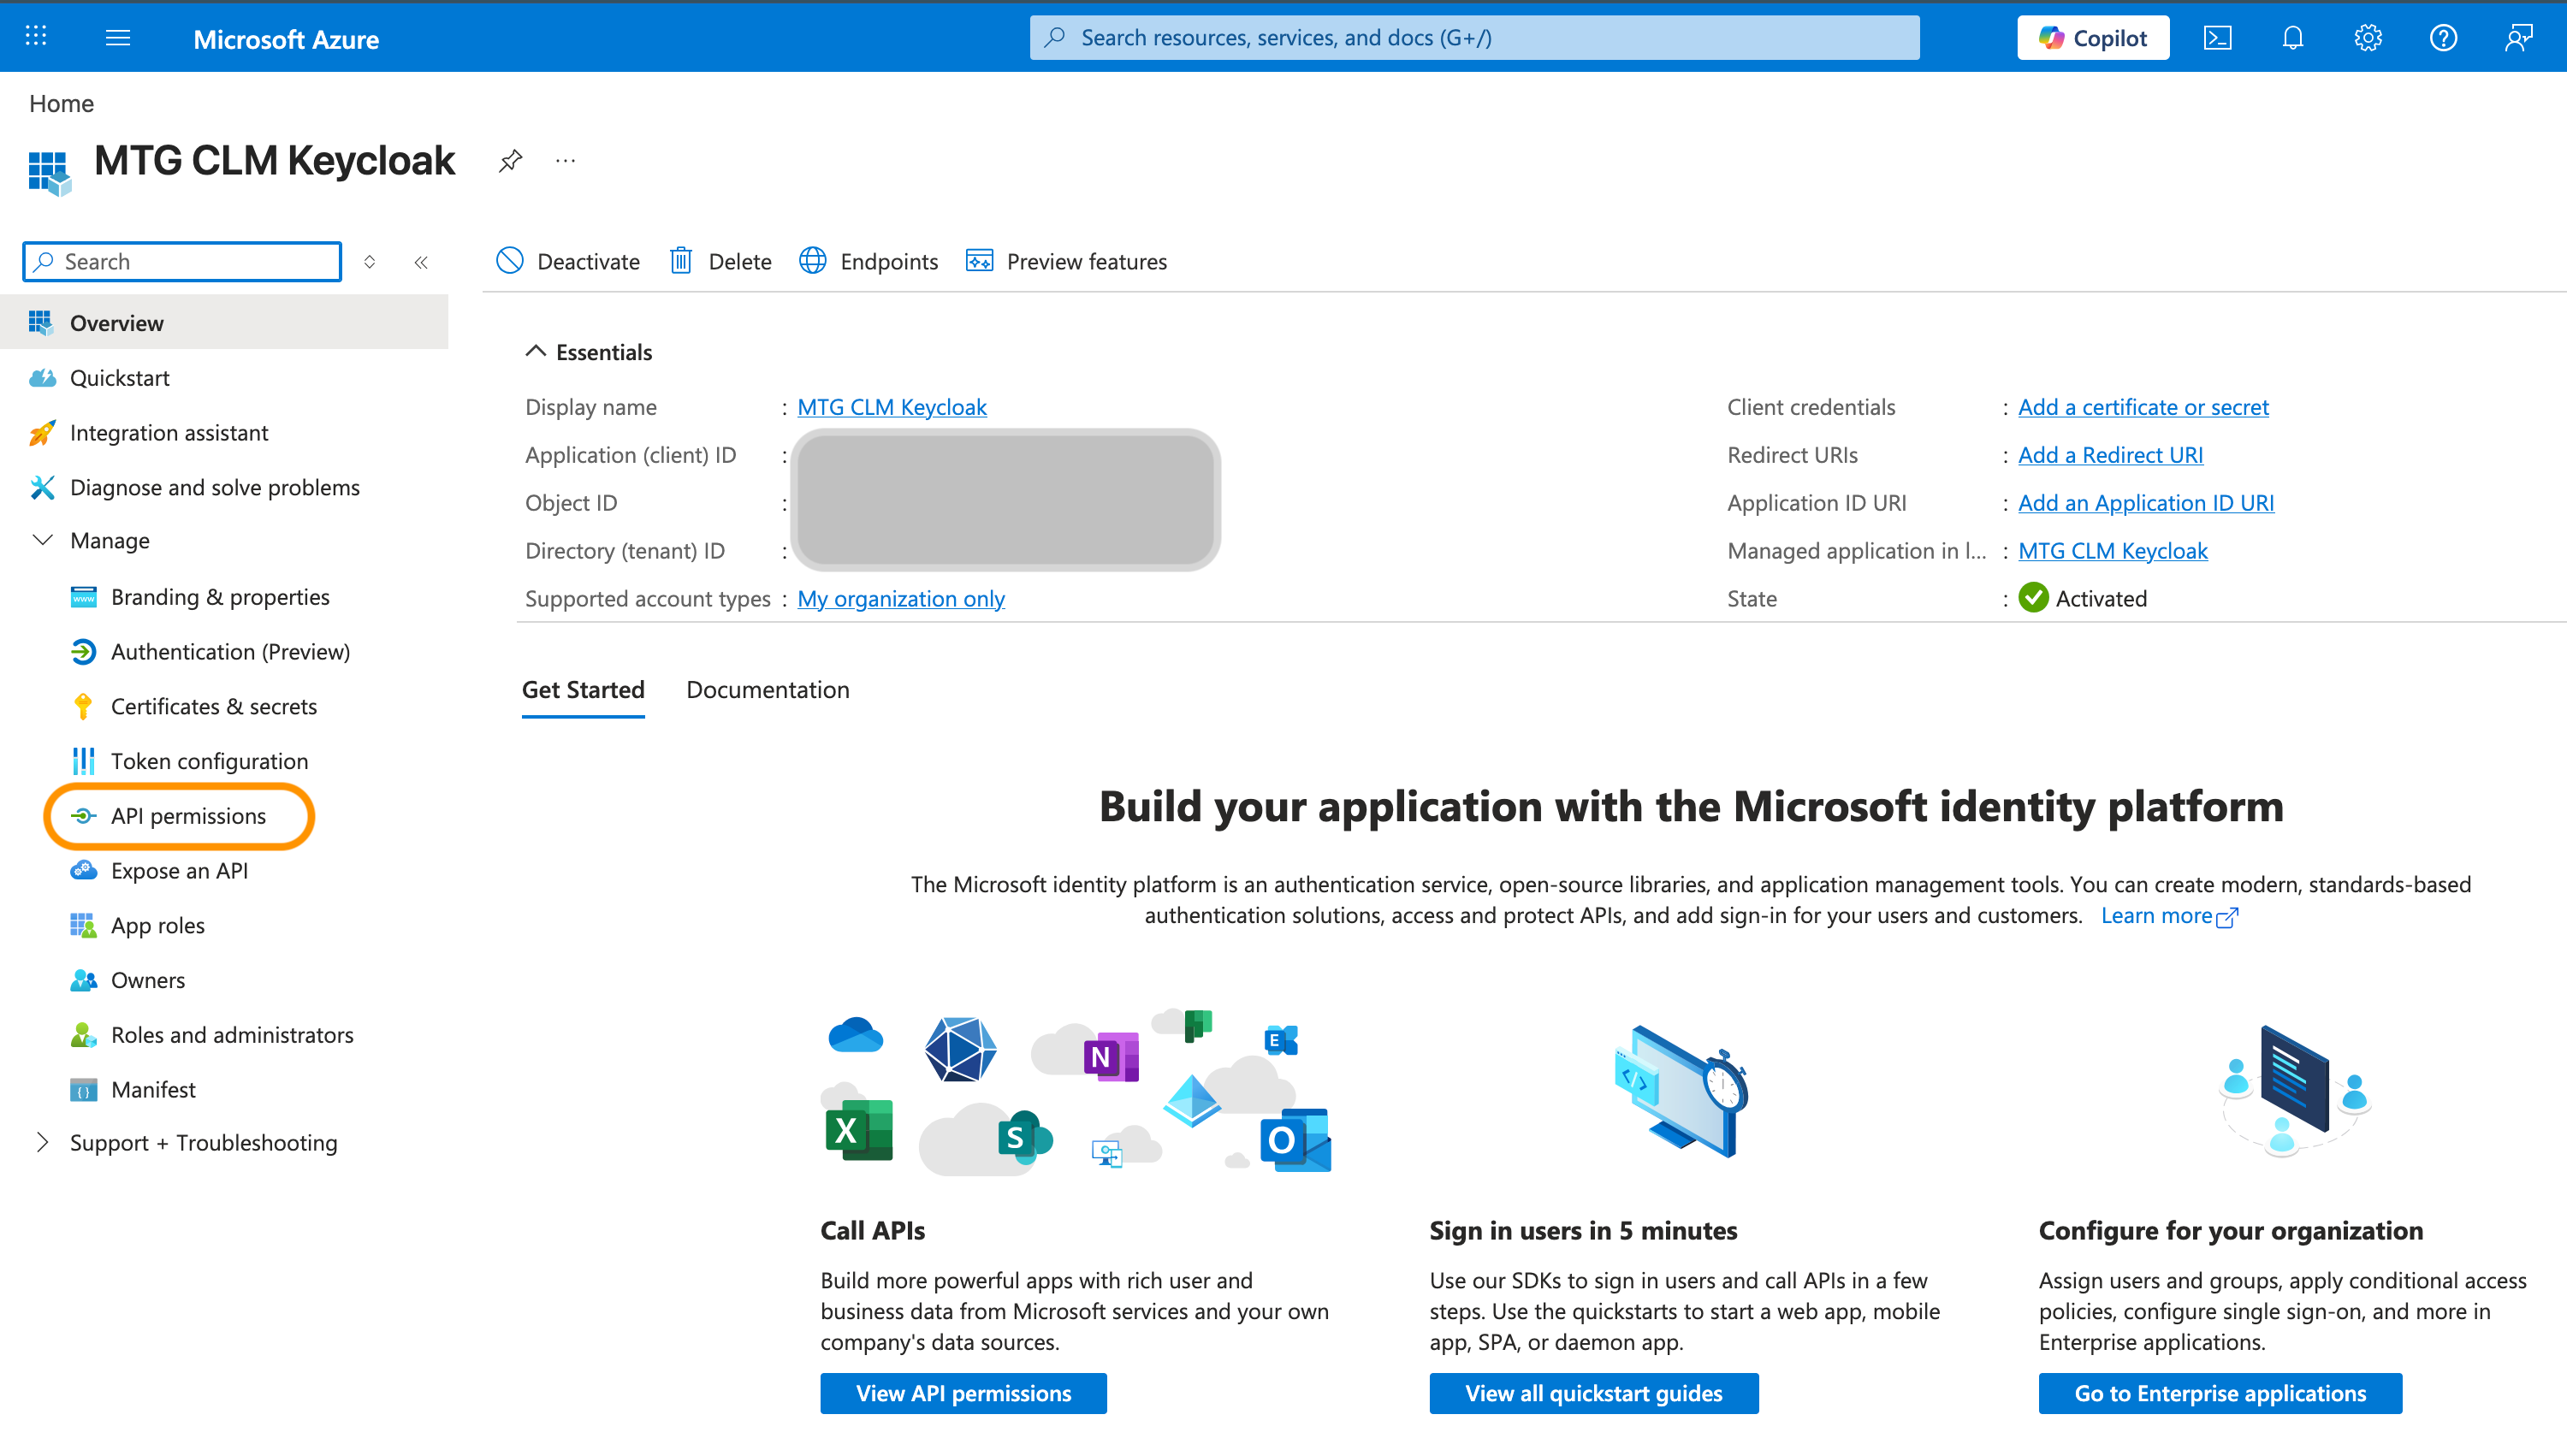
In your App Registration menu, select API permissions from the left sidebar.
-
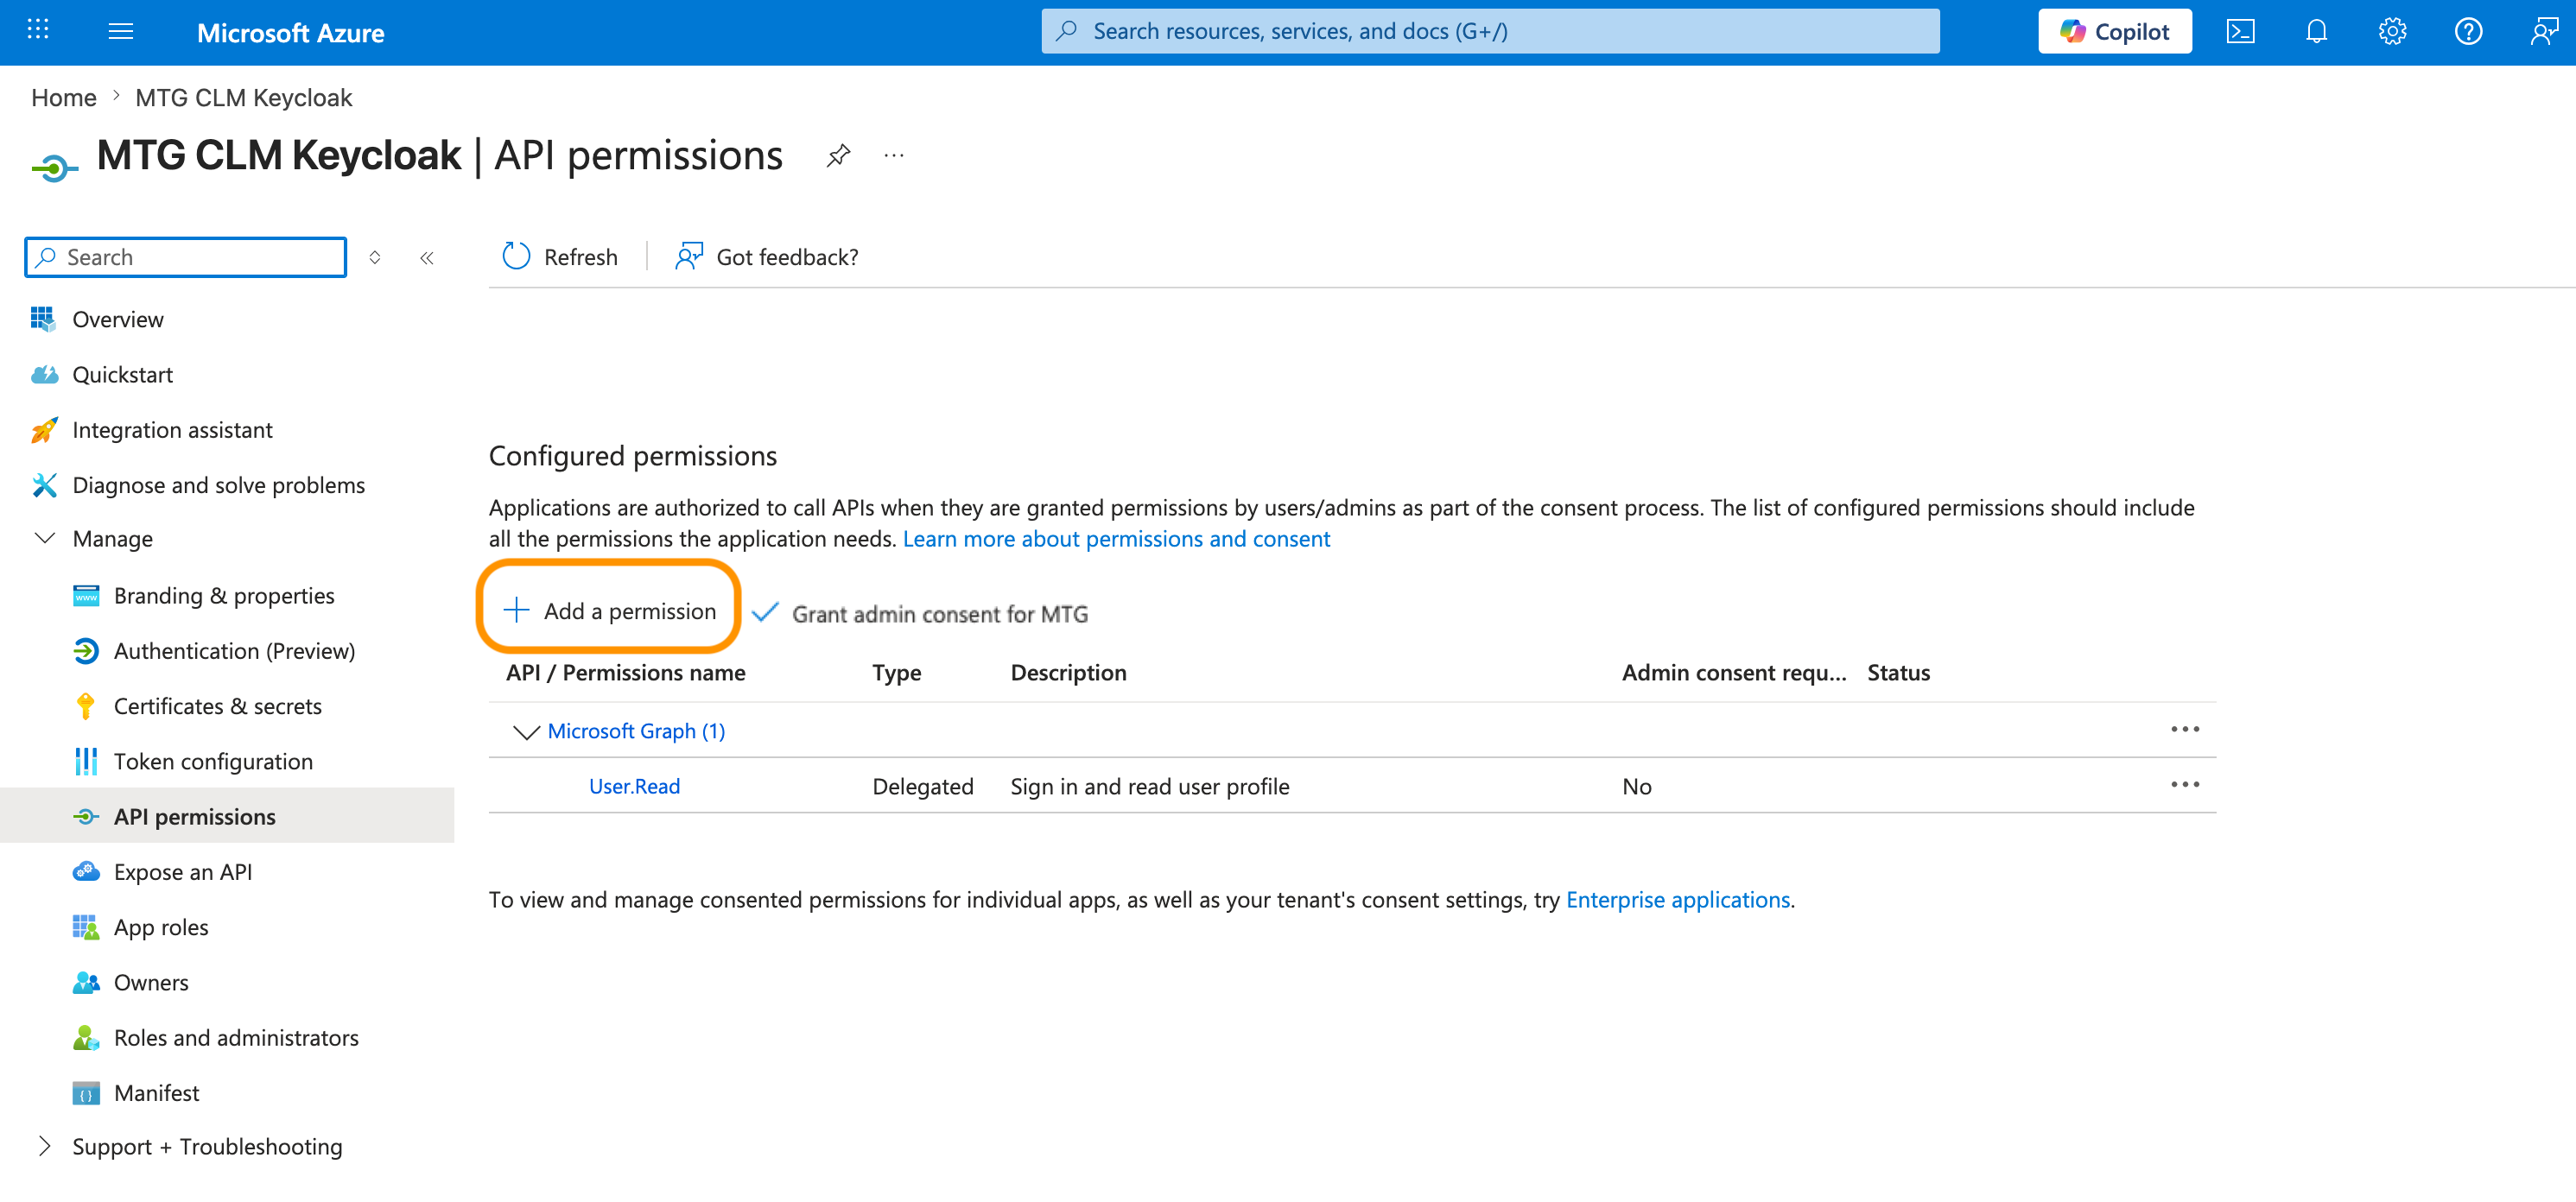
Click + Add a permission.
-
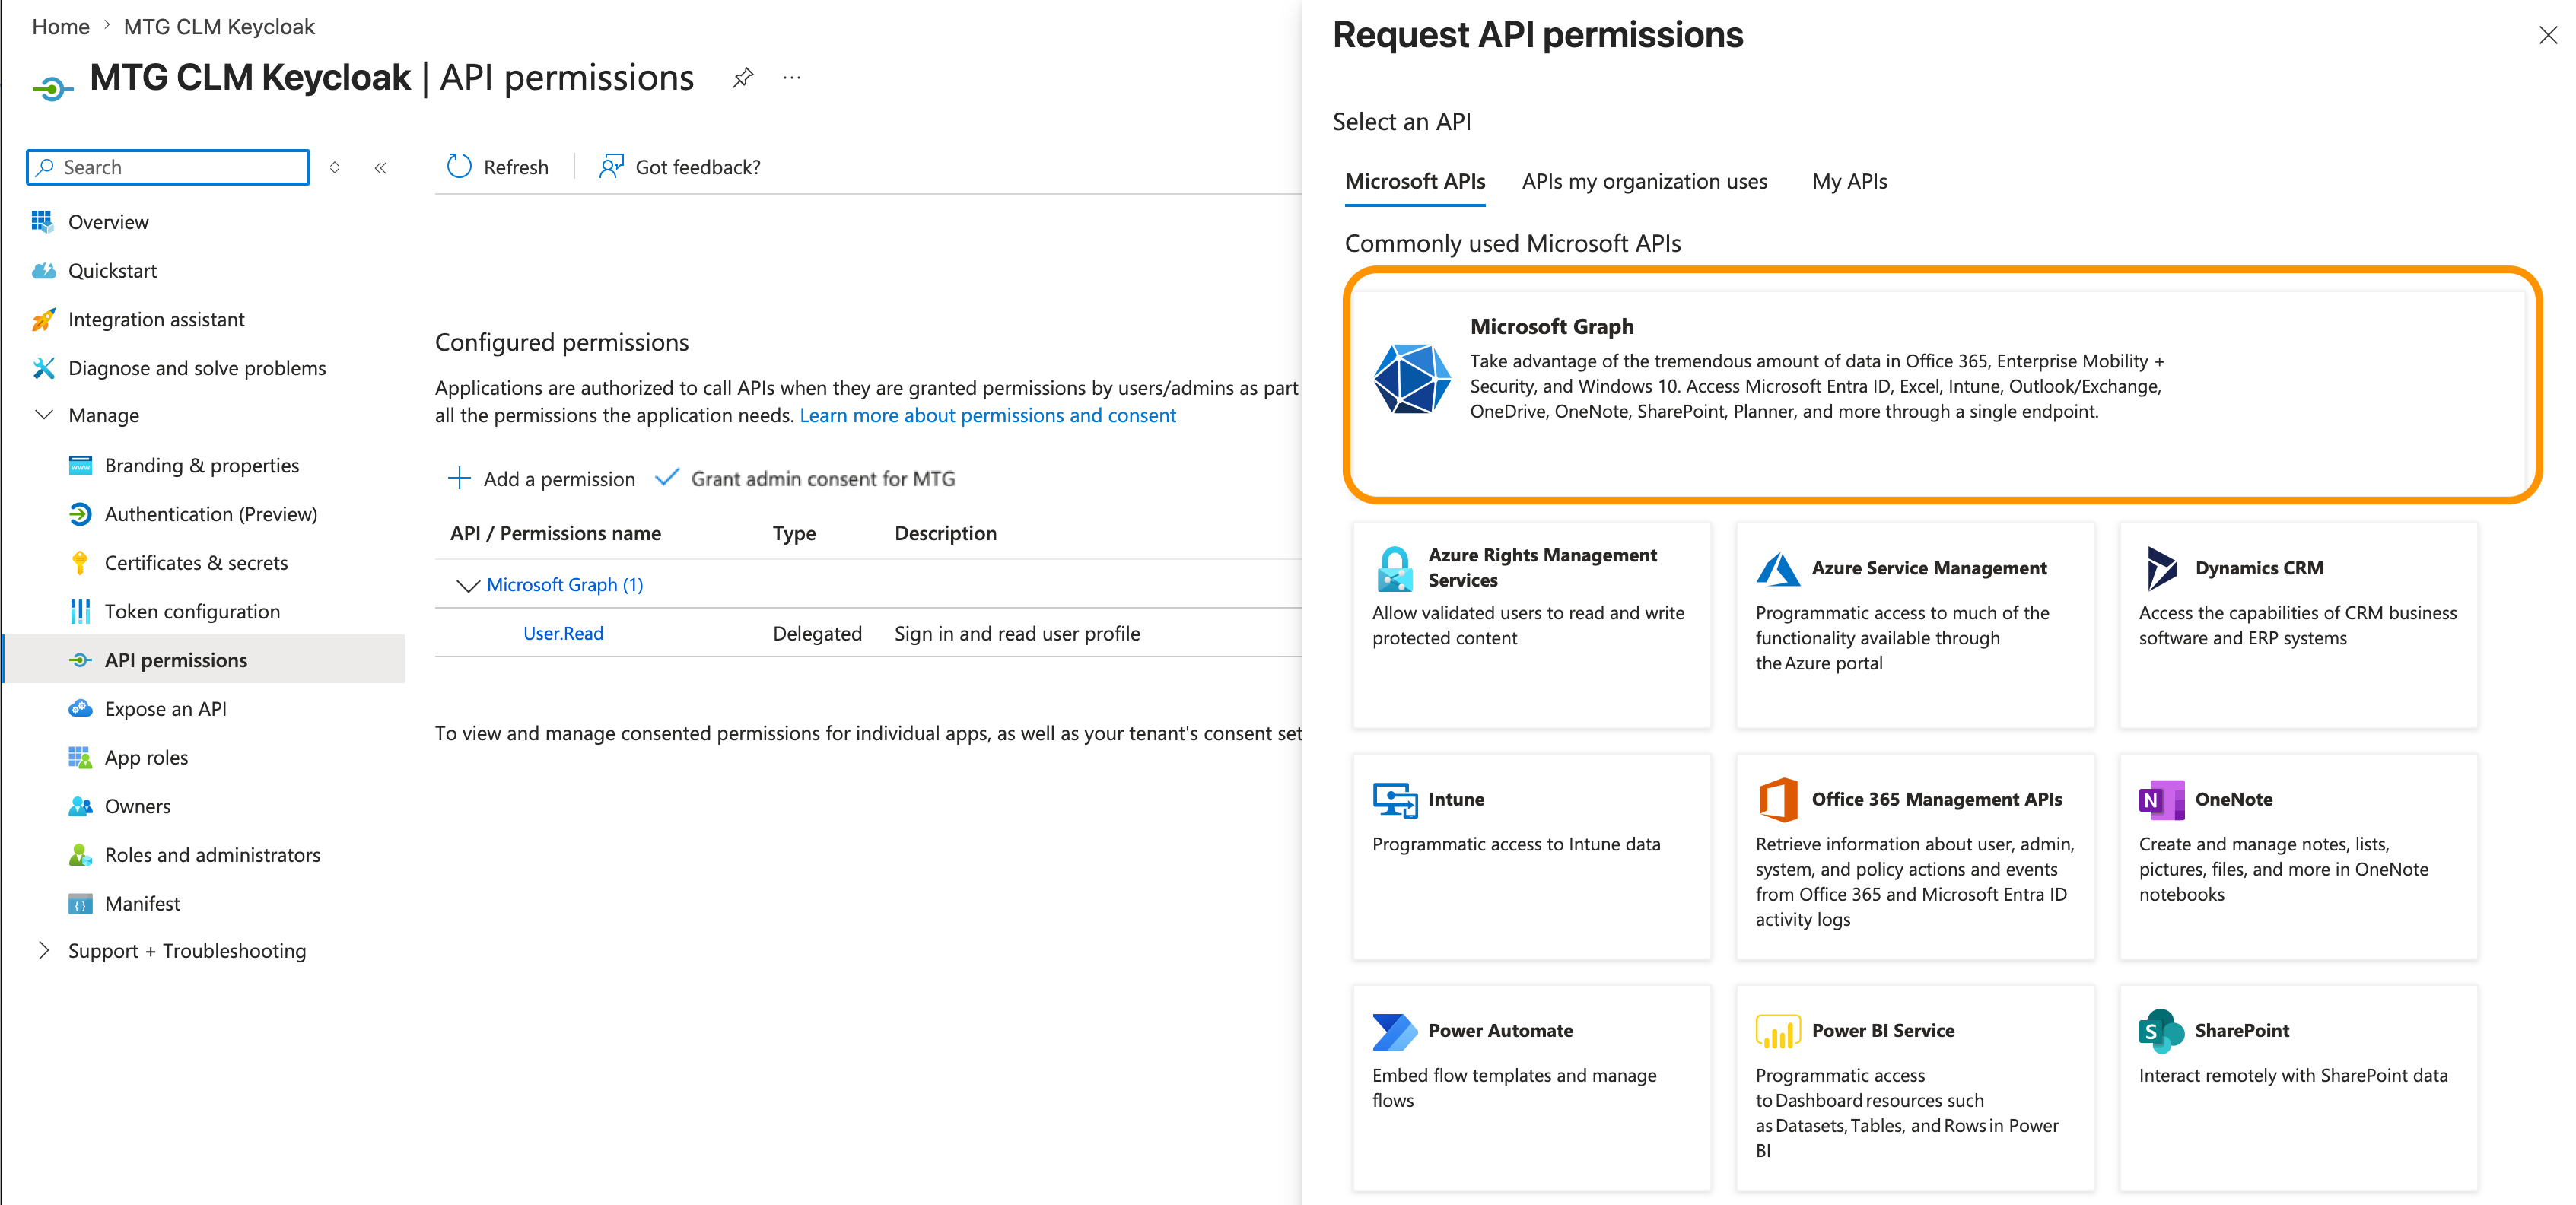
Select Microsoft Graph.
-
Select Application permissions (not Delegated permissions).
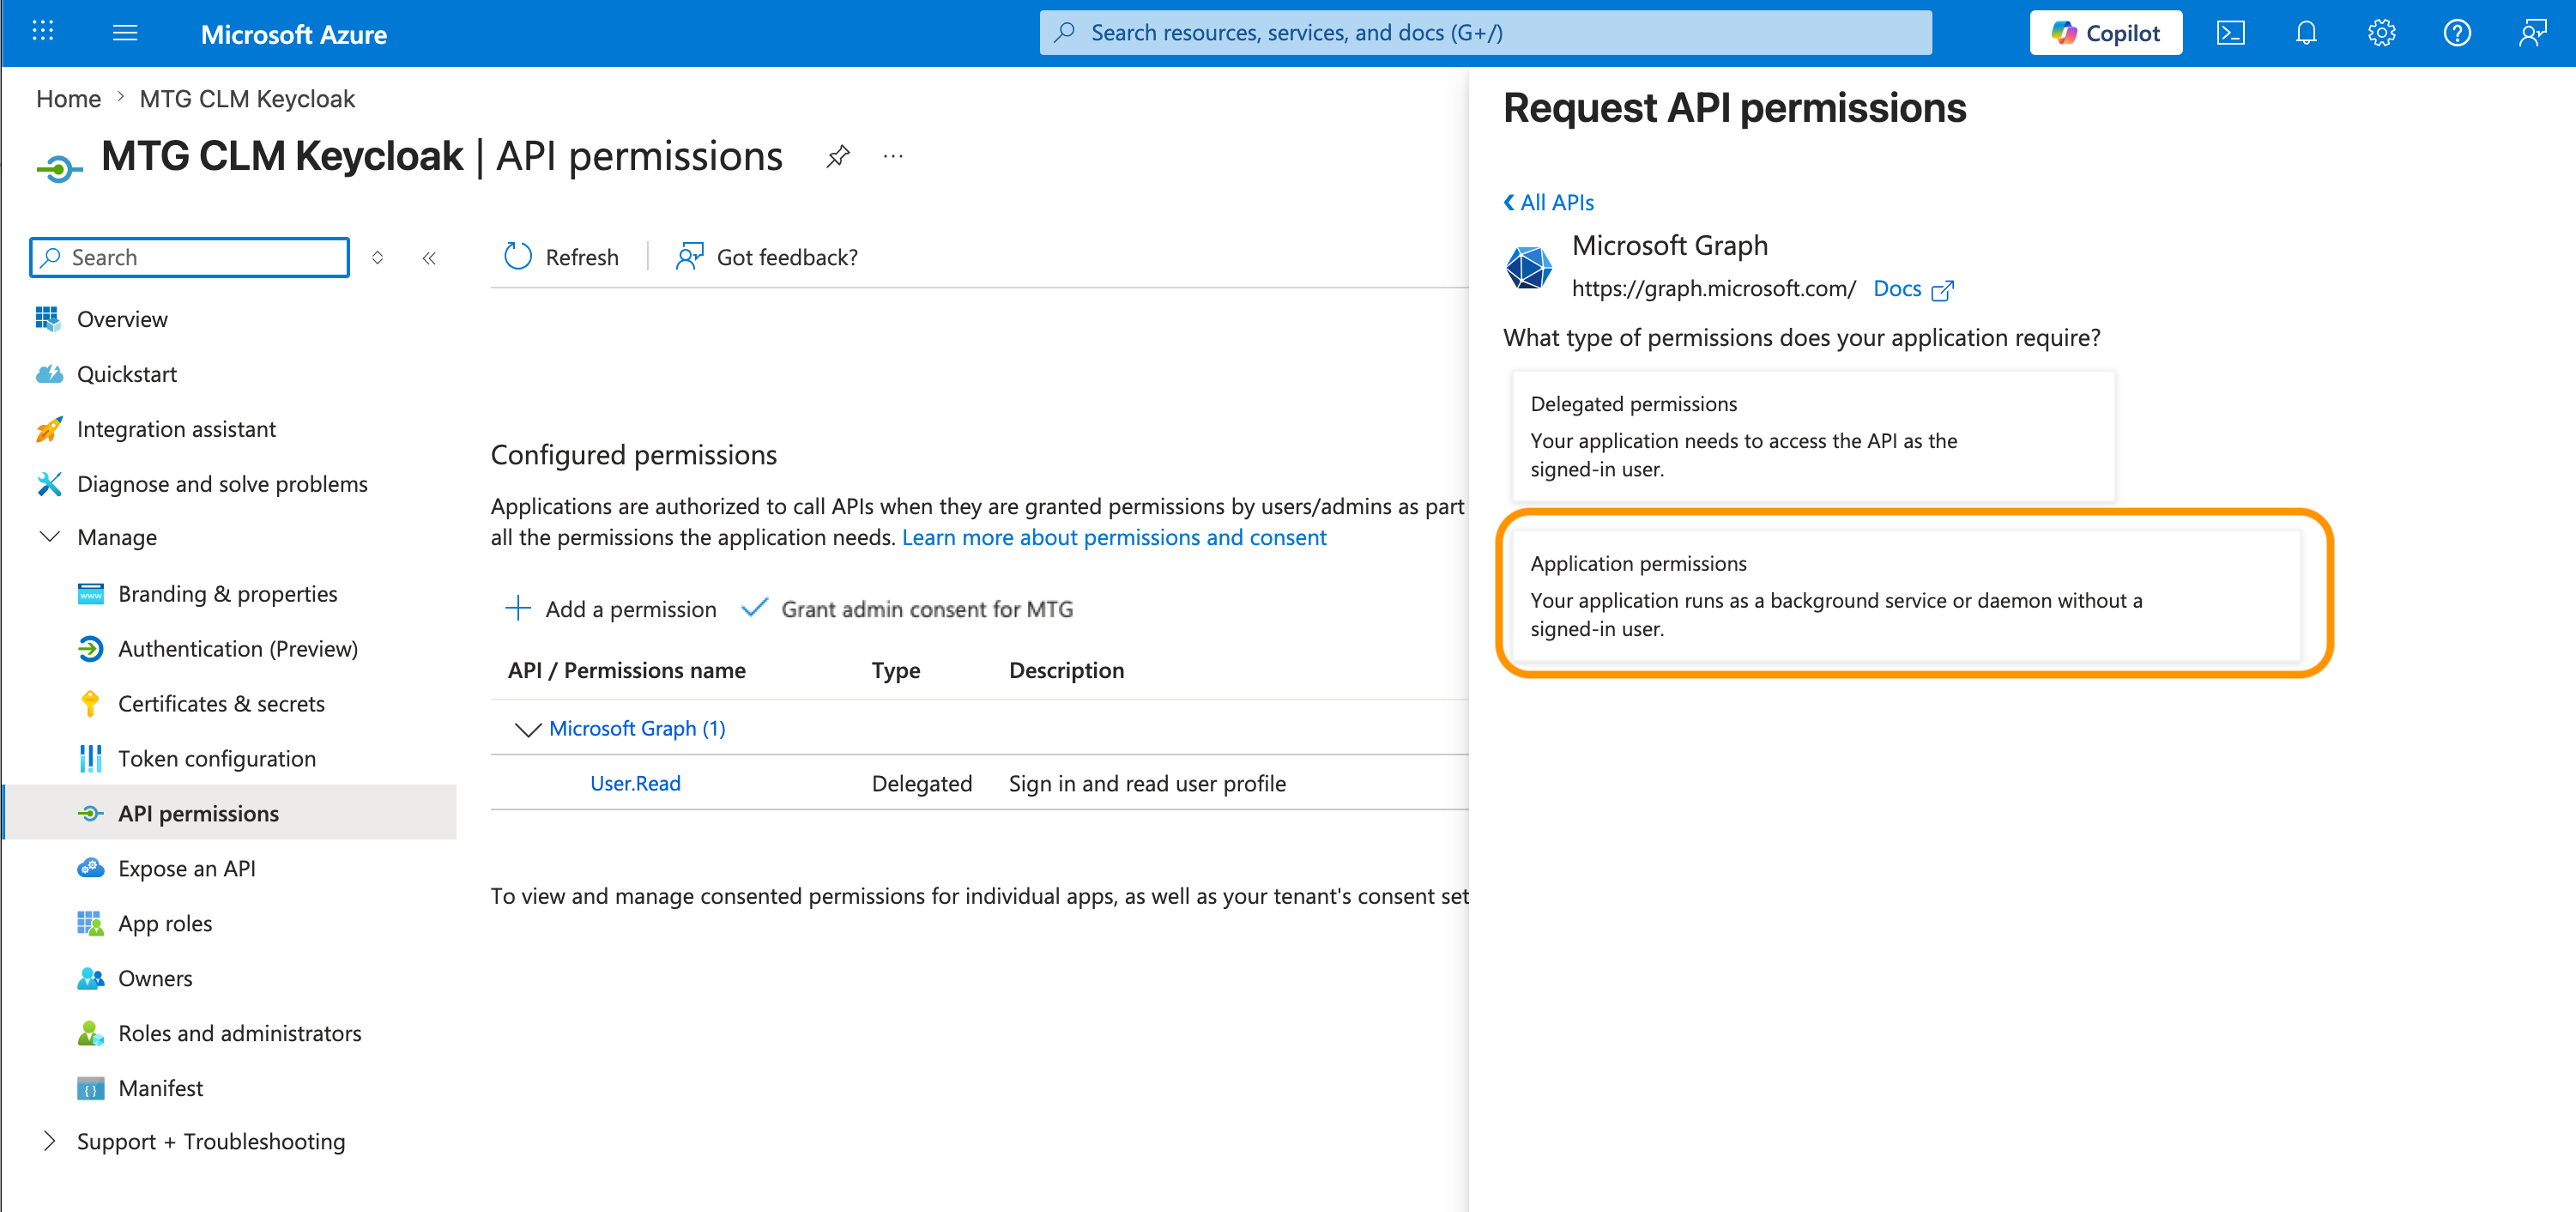
-
In the search bar, locate and check the following permission:
Directory.Read.All. Click Add permissions at the bottom of the screen.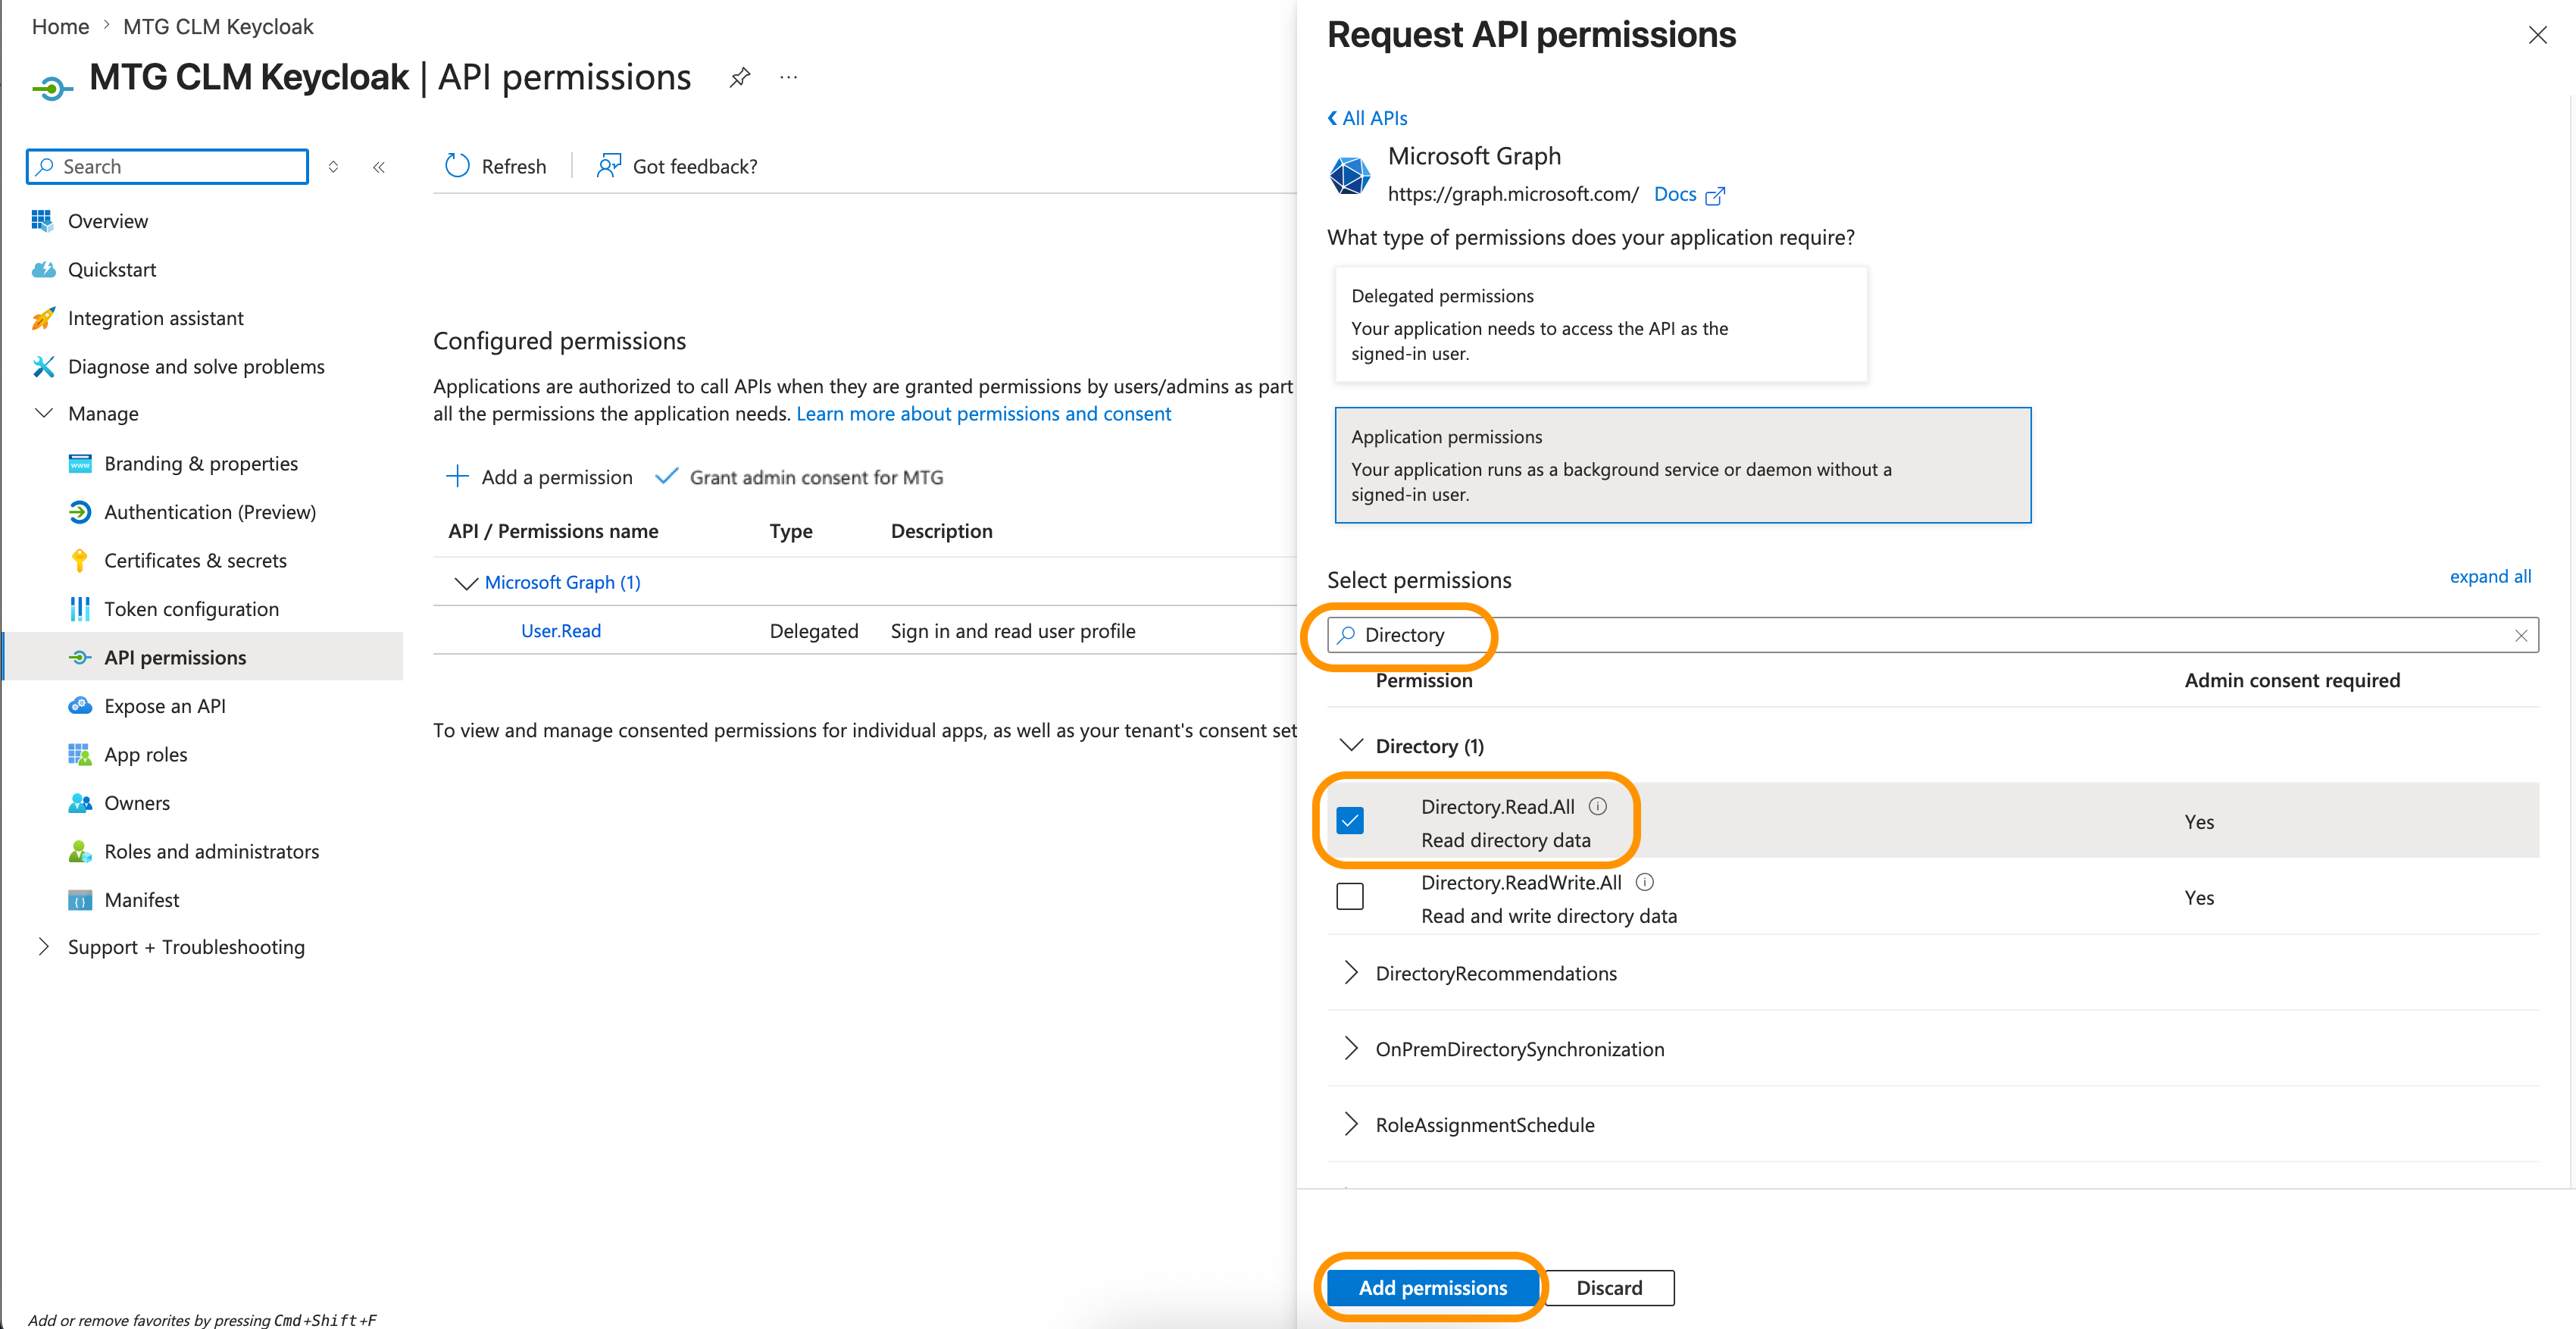
-
Once the permissions are added, select them and click the Grant admin consent for [Your Tenant Name] button located above the permissions list.
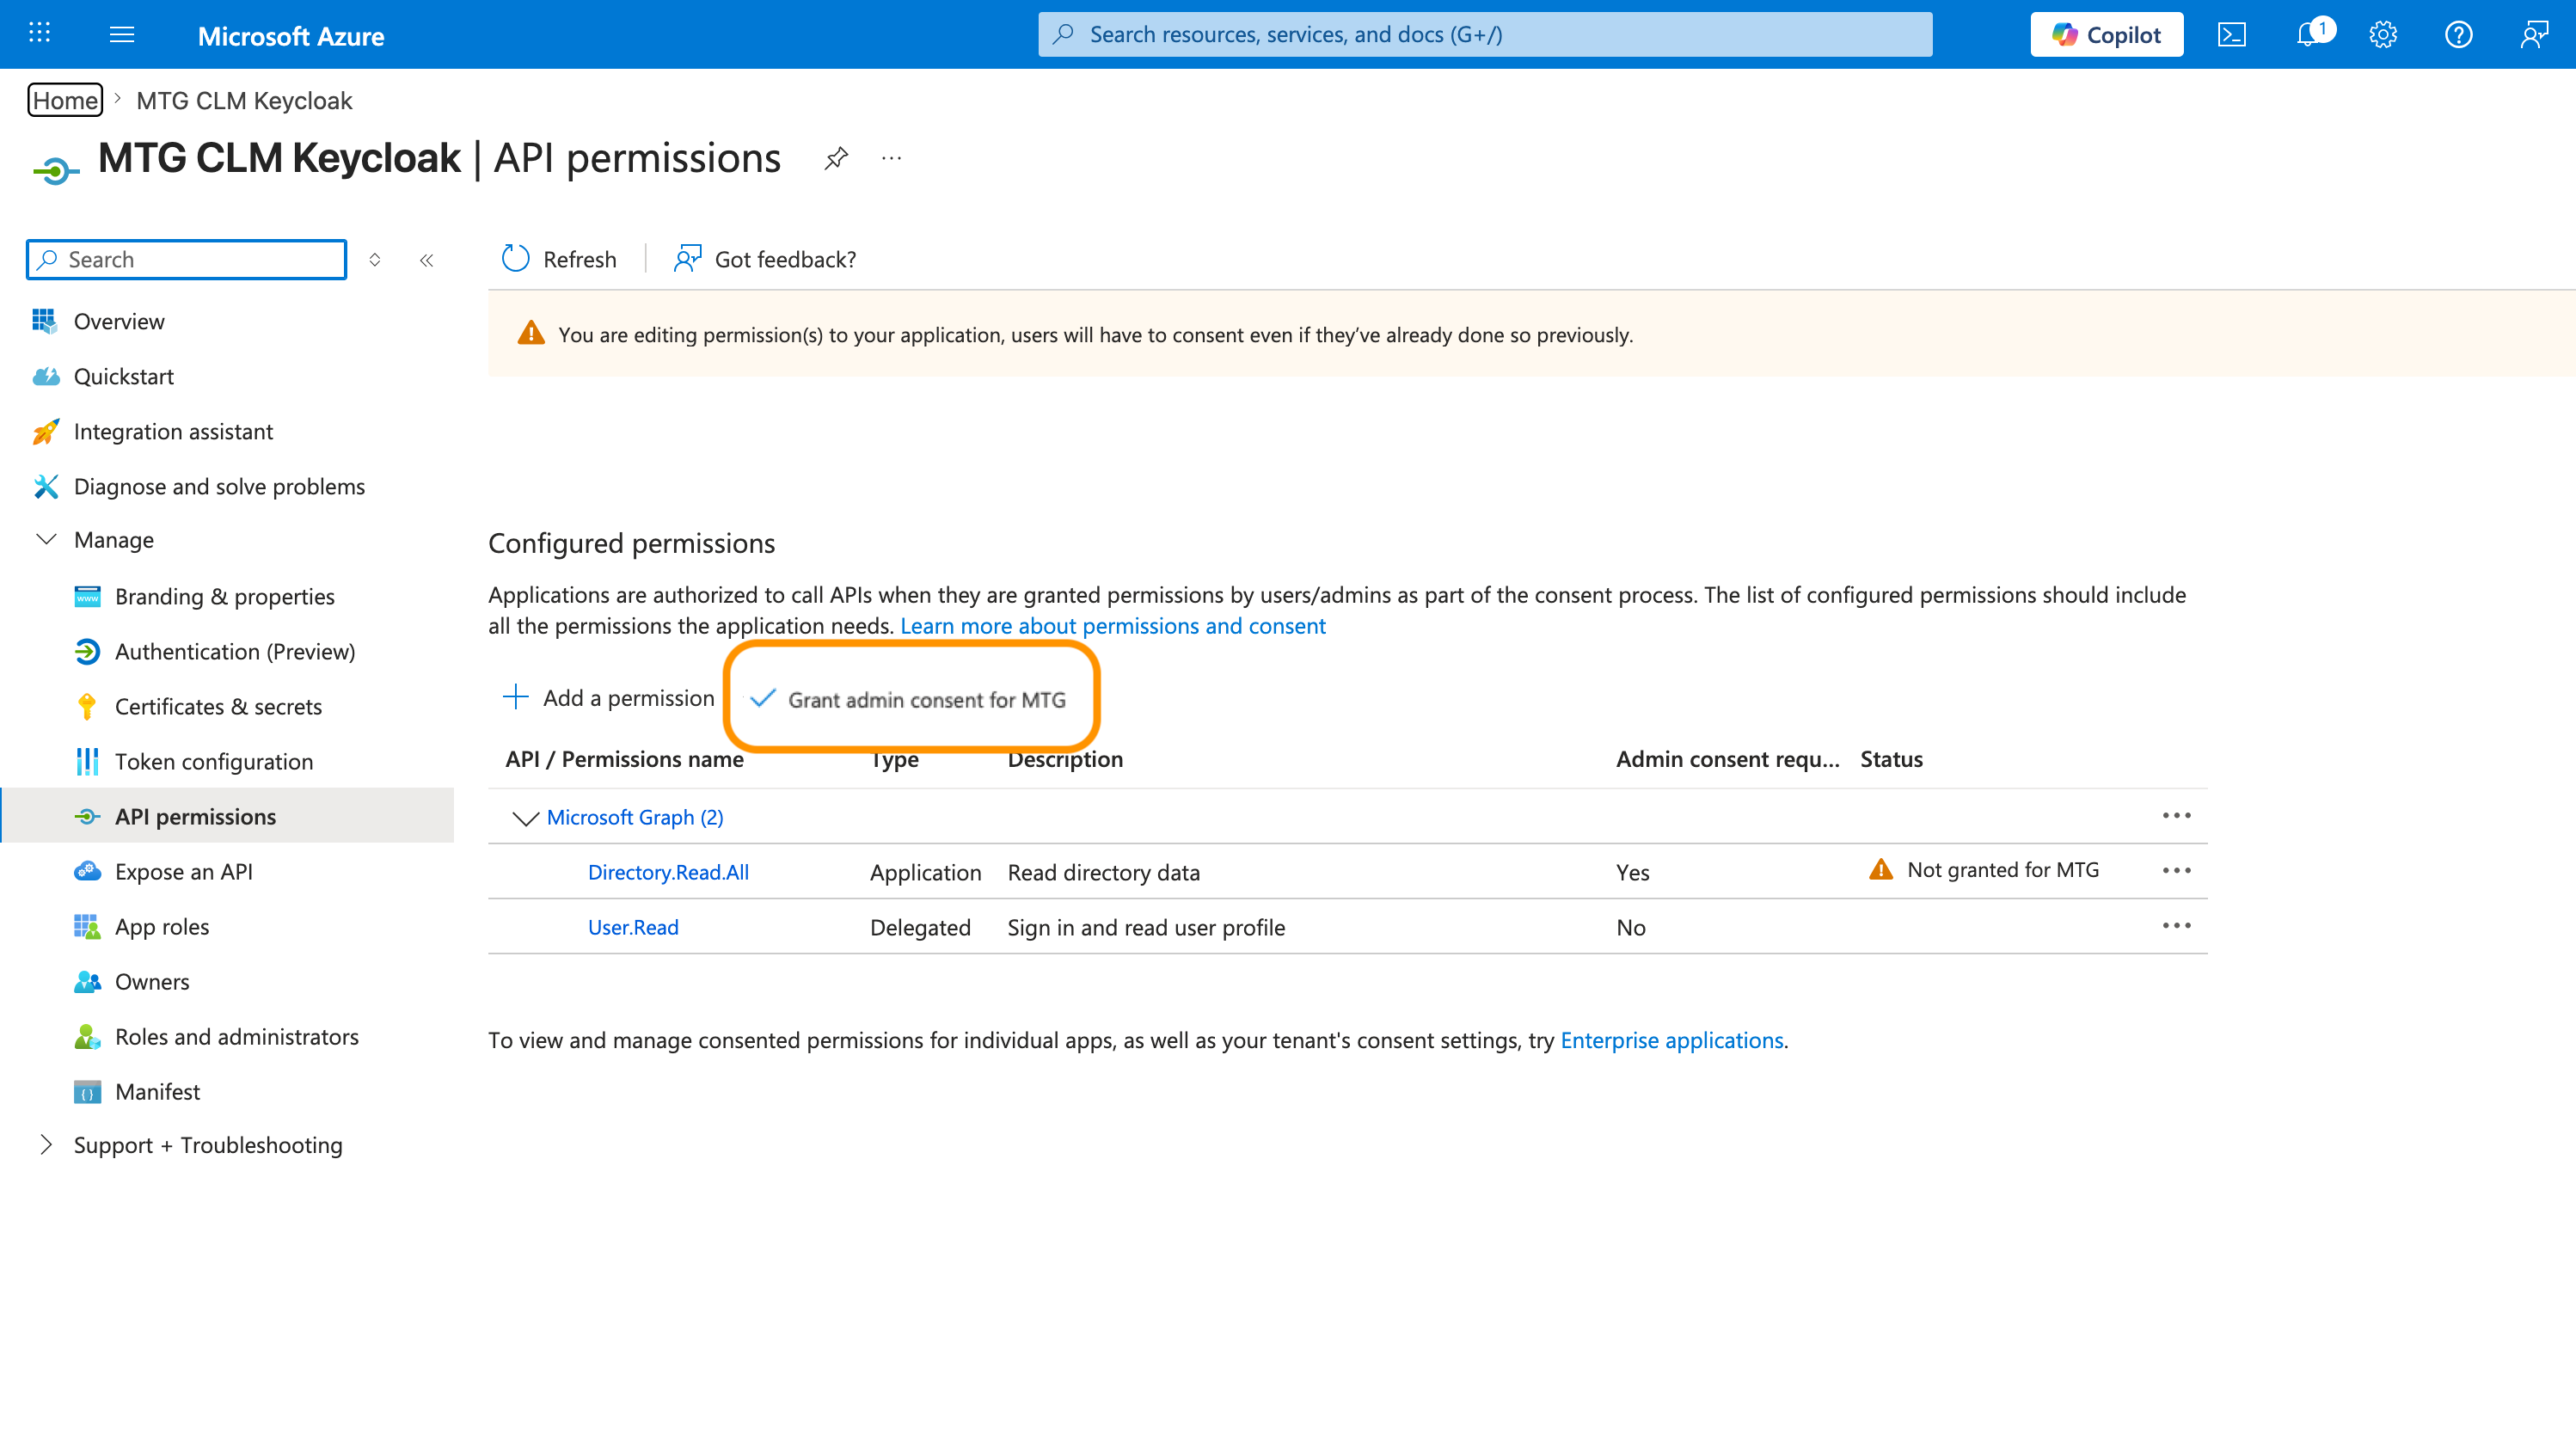
-
Click Yes in the confirmation prompt. You should be seeing a similar screen to:
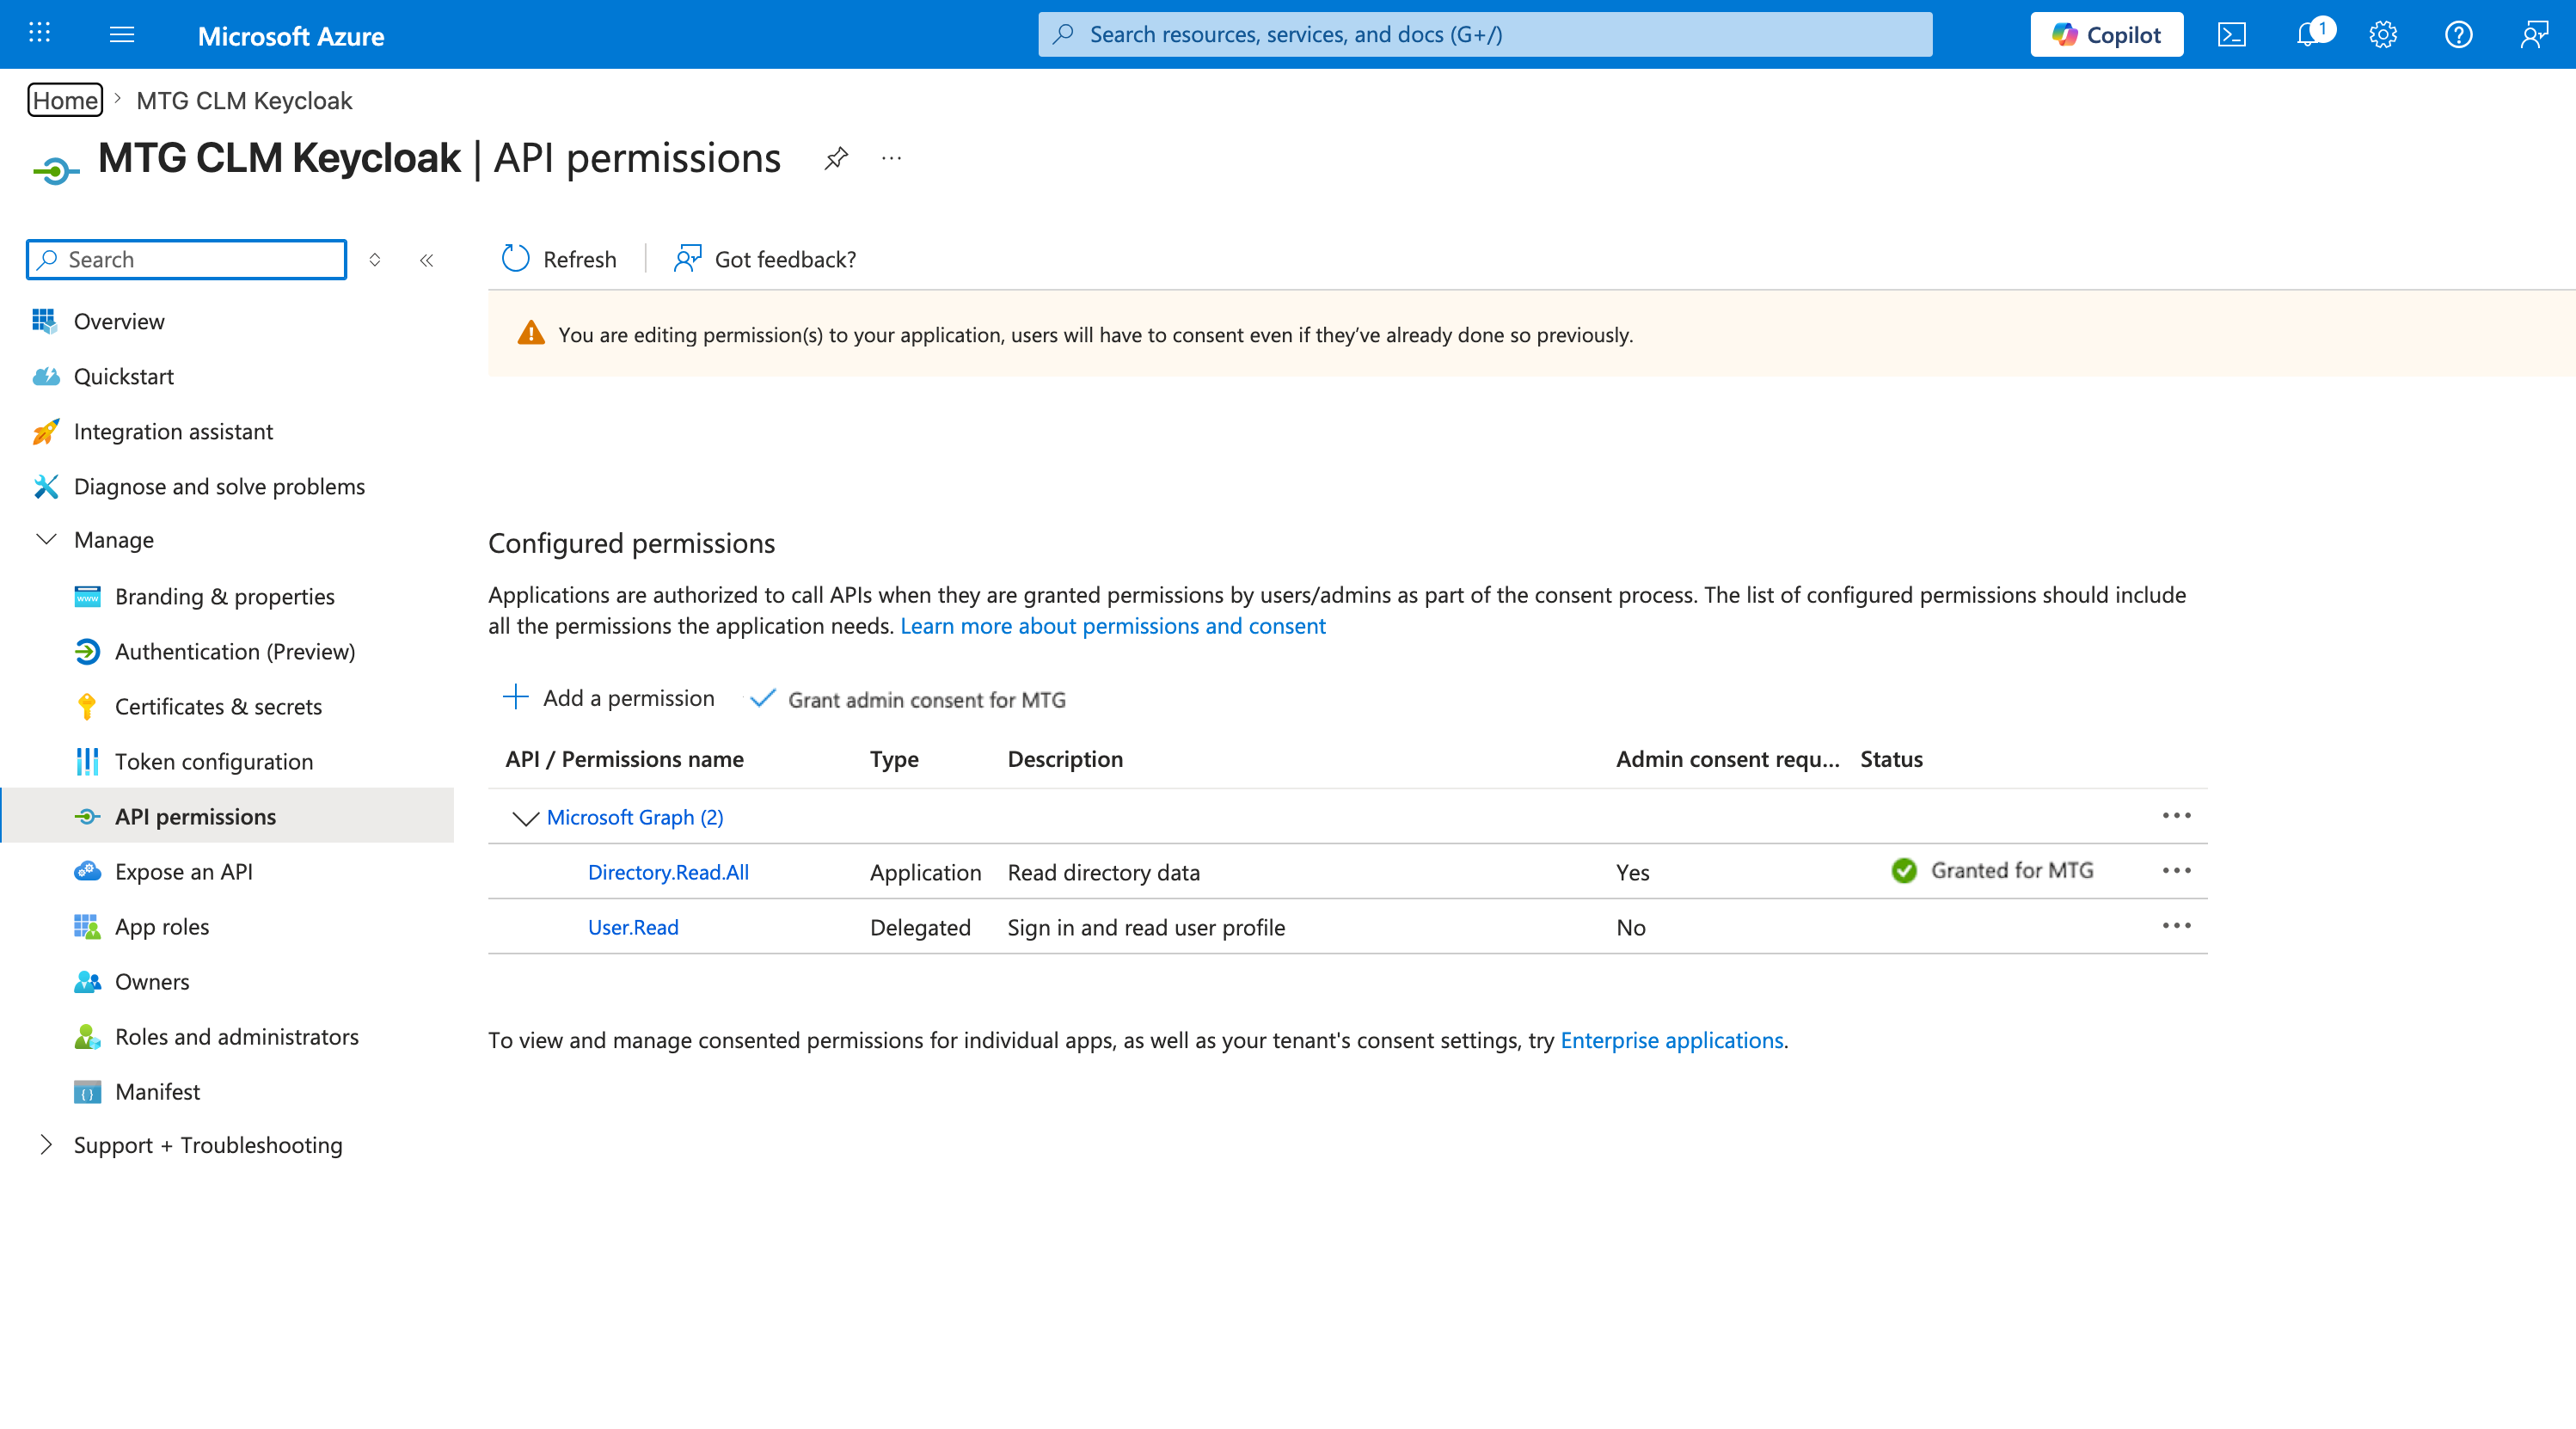
| If the Grant admin consent button is greyed out, your current account does not have the Global Administrator or Privileged Role Administrator rights required to authorize these permissions. |
Generating the Client Secret
Keycloak requires a client secret to authenticate against your Entra ID tenant securely.
-
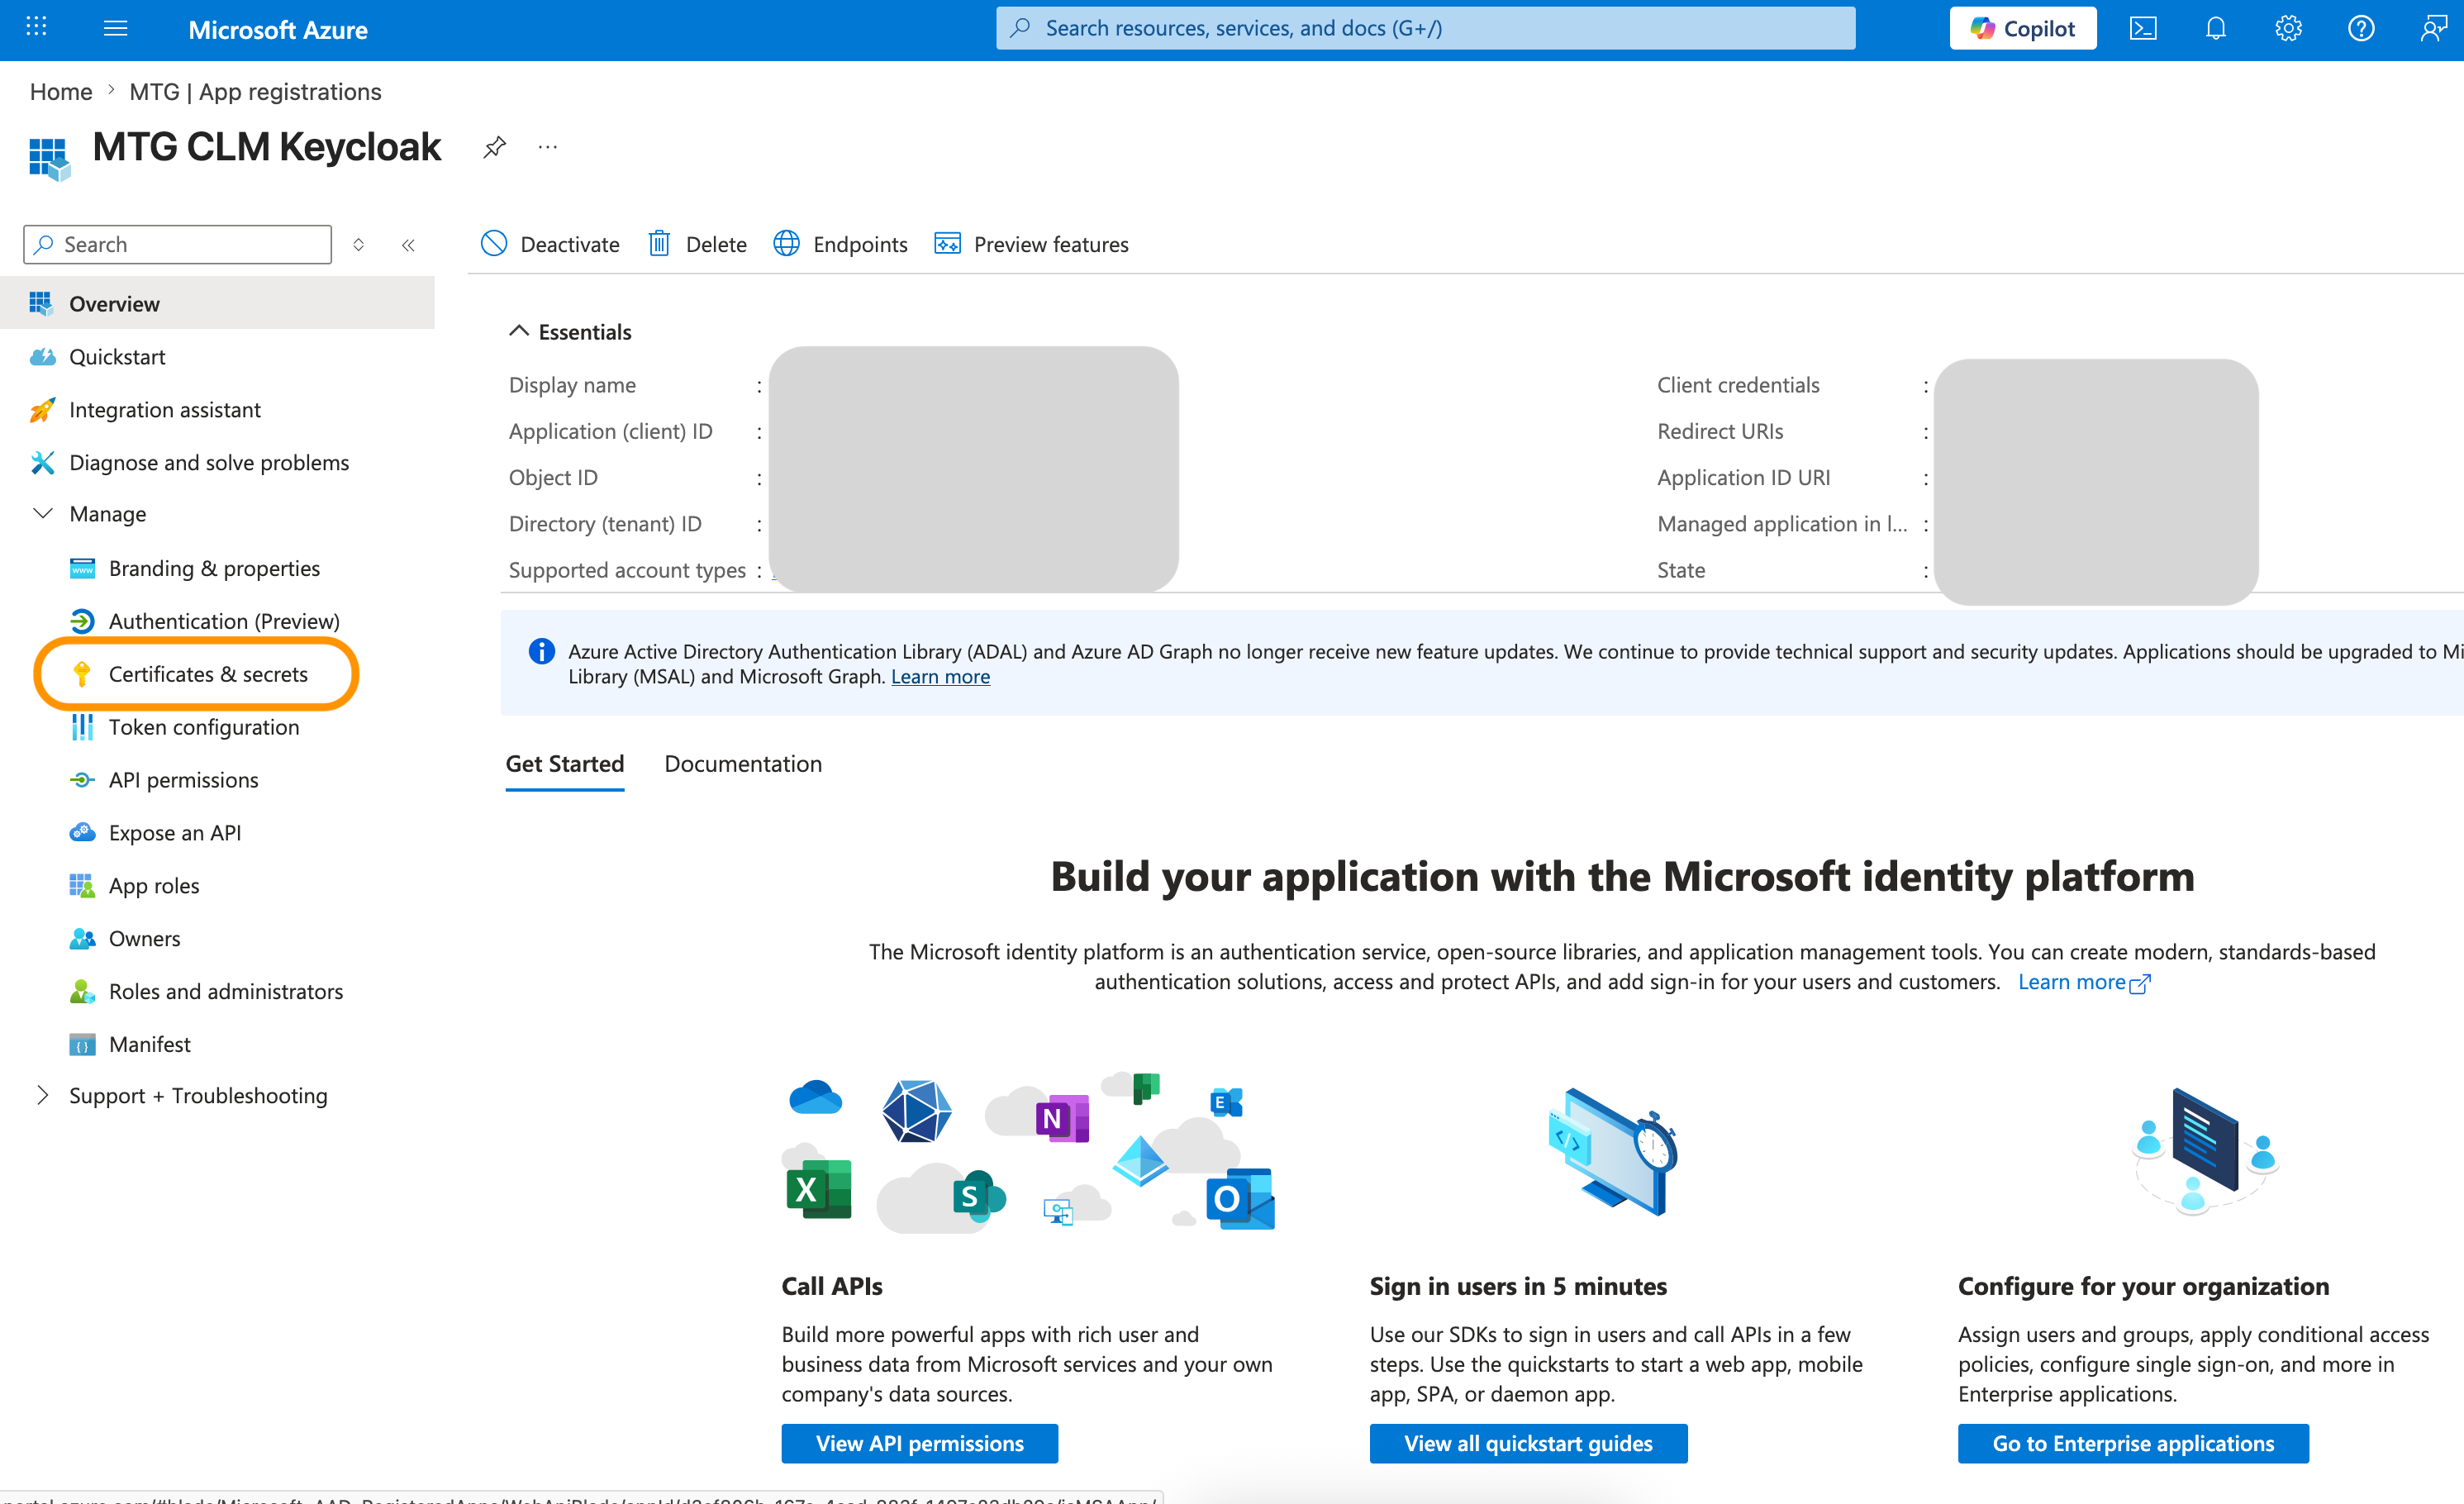
In your App Registration menu, select Certificates & secrets from the left sidebar.
-
Click + New client secret.
-
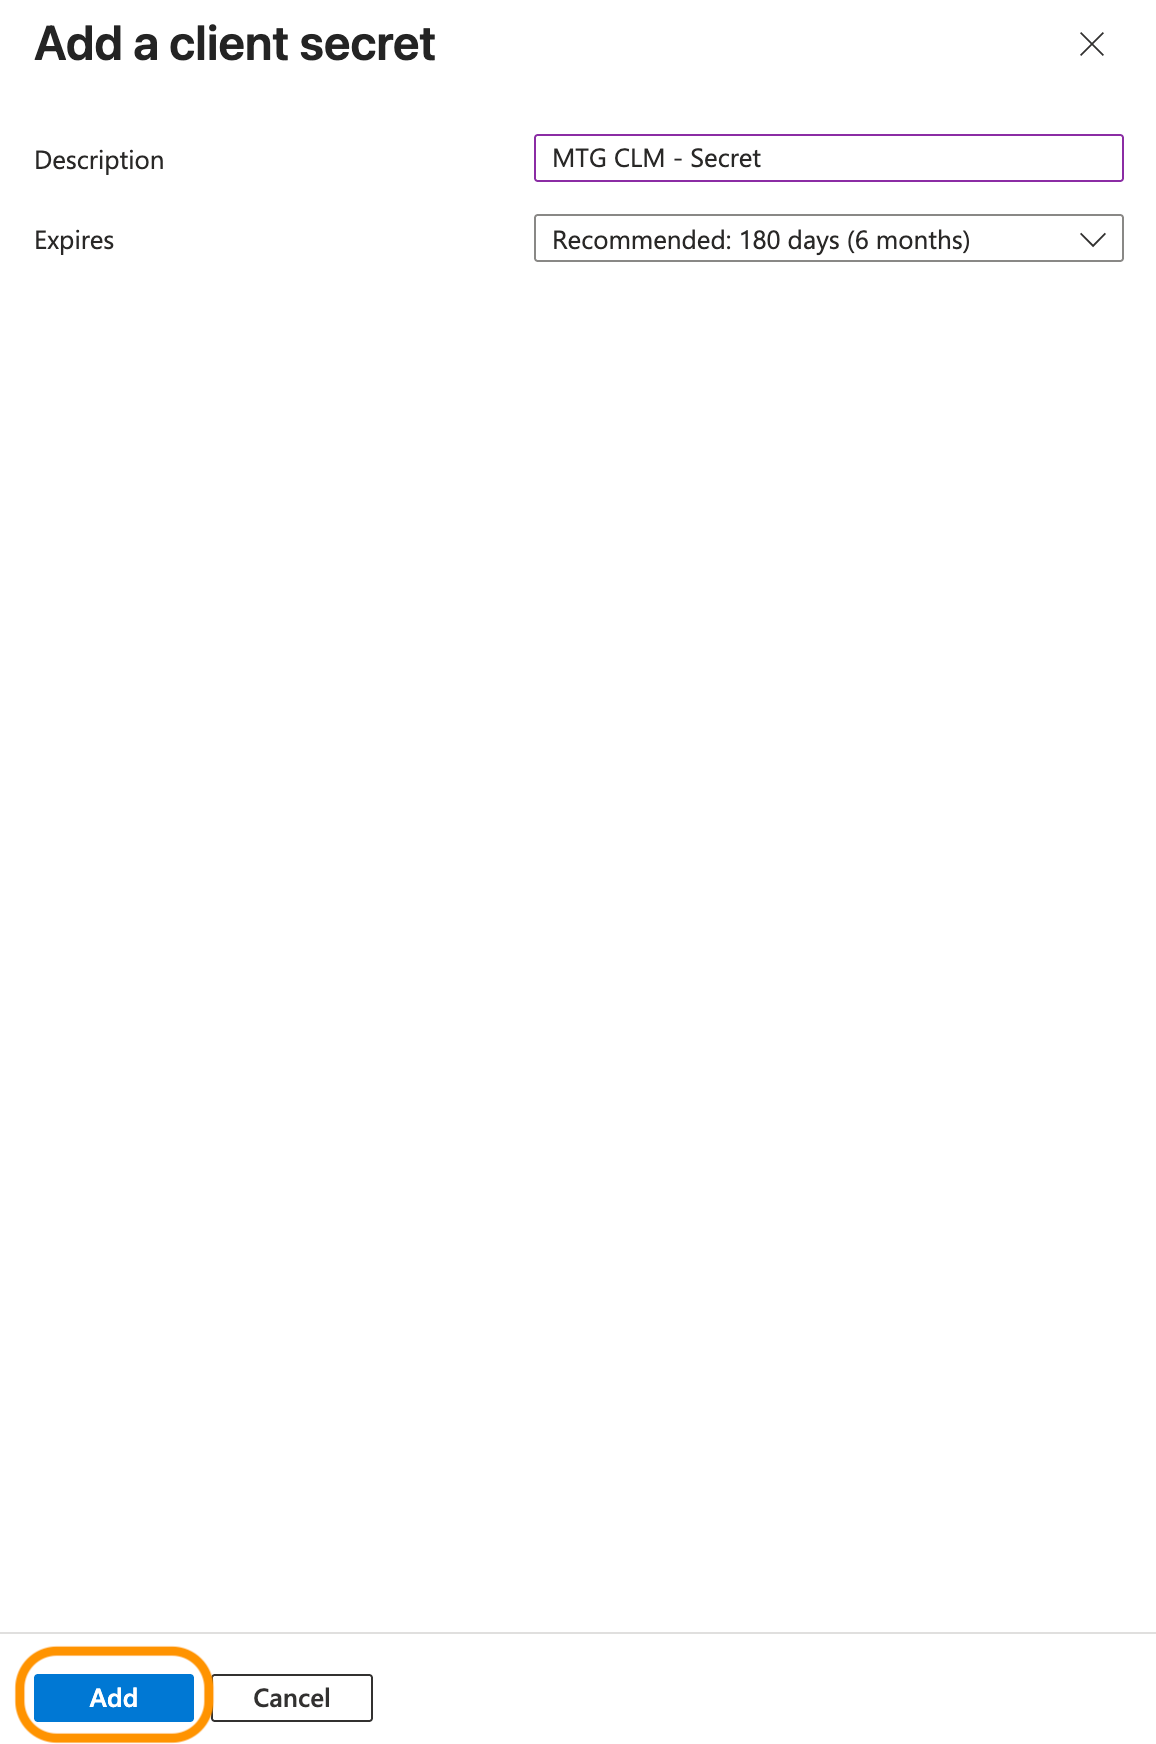
Enter a descriptive Description (e.g., MTG CLM-Secret) and select an Expires duration according to your security policy.
-
Click Add.
| Copy the Value string immediately and store it in a secure location. This value will be permanently hidden once you leave this page, and you cannot retrieve it later. You will paste this value into Keycloak in the next section. |
Configuring Keycloak Identity Provider
Accessing Identity Provider Configuration
-
Sign in to your Keycloak administration console.
-
Navigate to your target realm for MTG CLM integration.
-
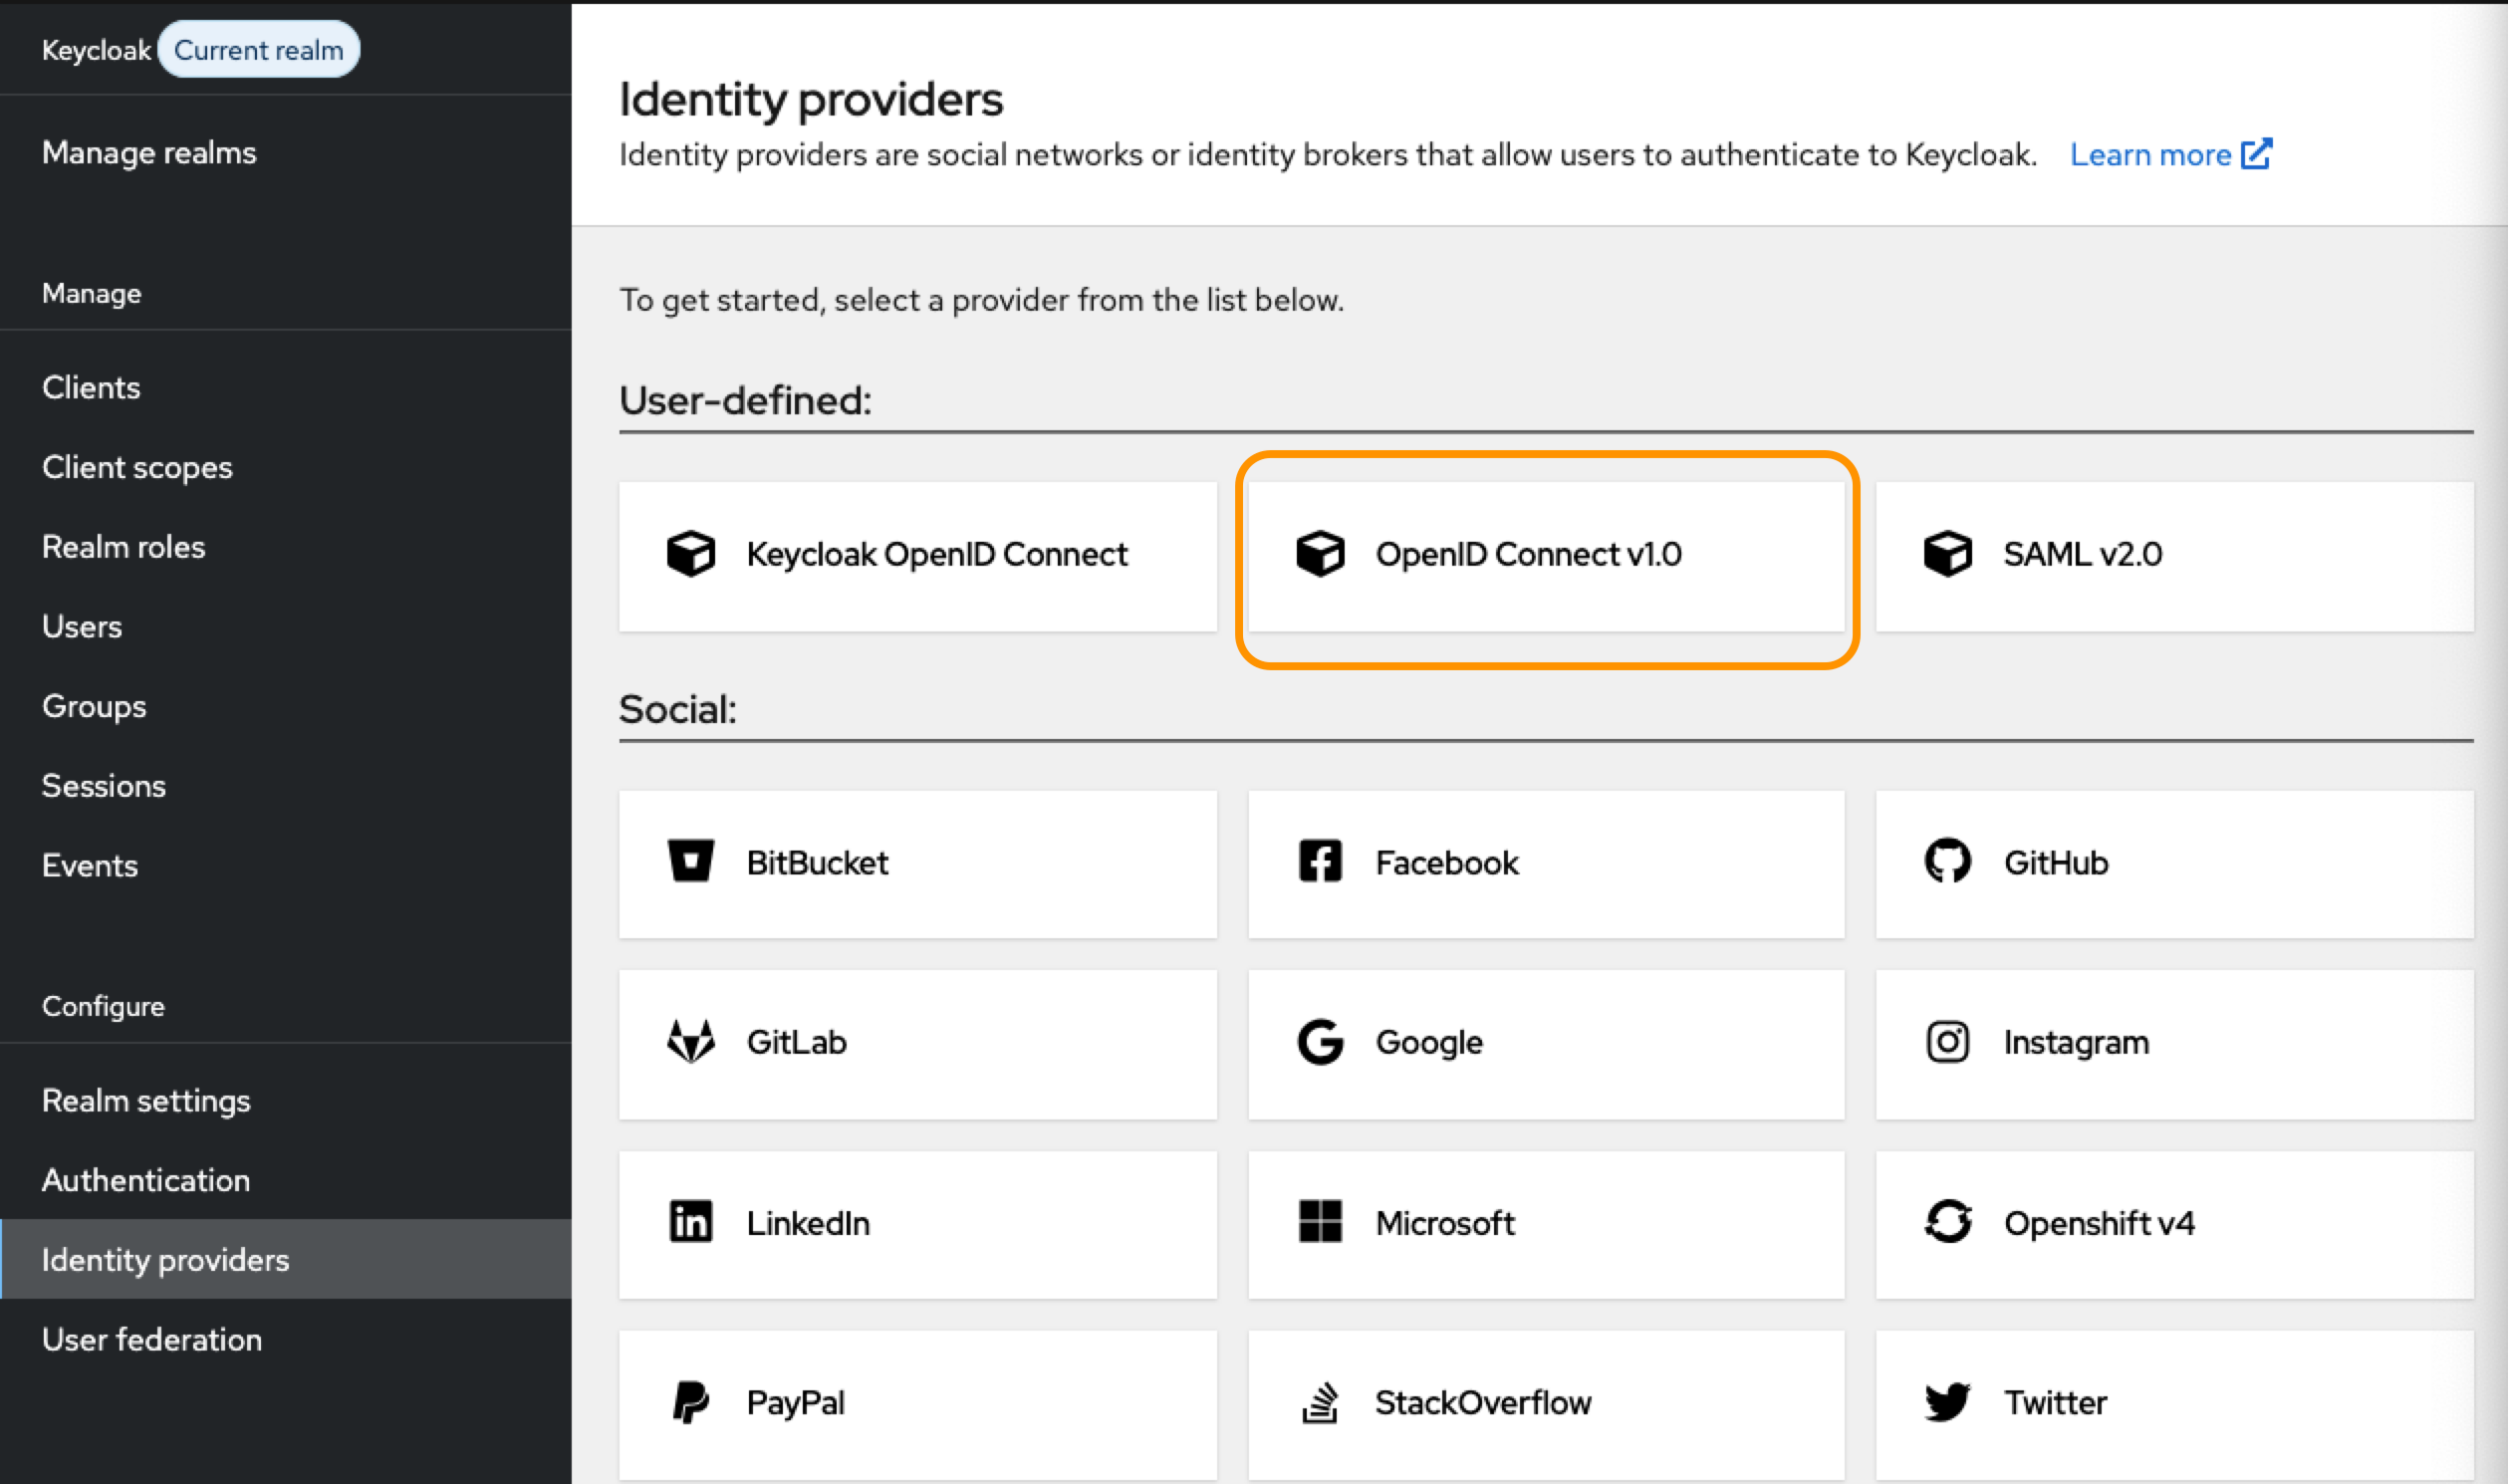
Select Identity Providers from the left navigation menu.
-
Click OpenID Connect v1.0.
Configuring Provider Settings
1. Basic Configuration
-
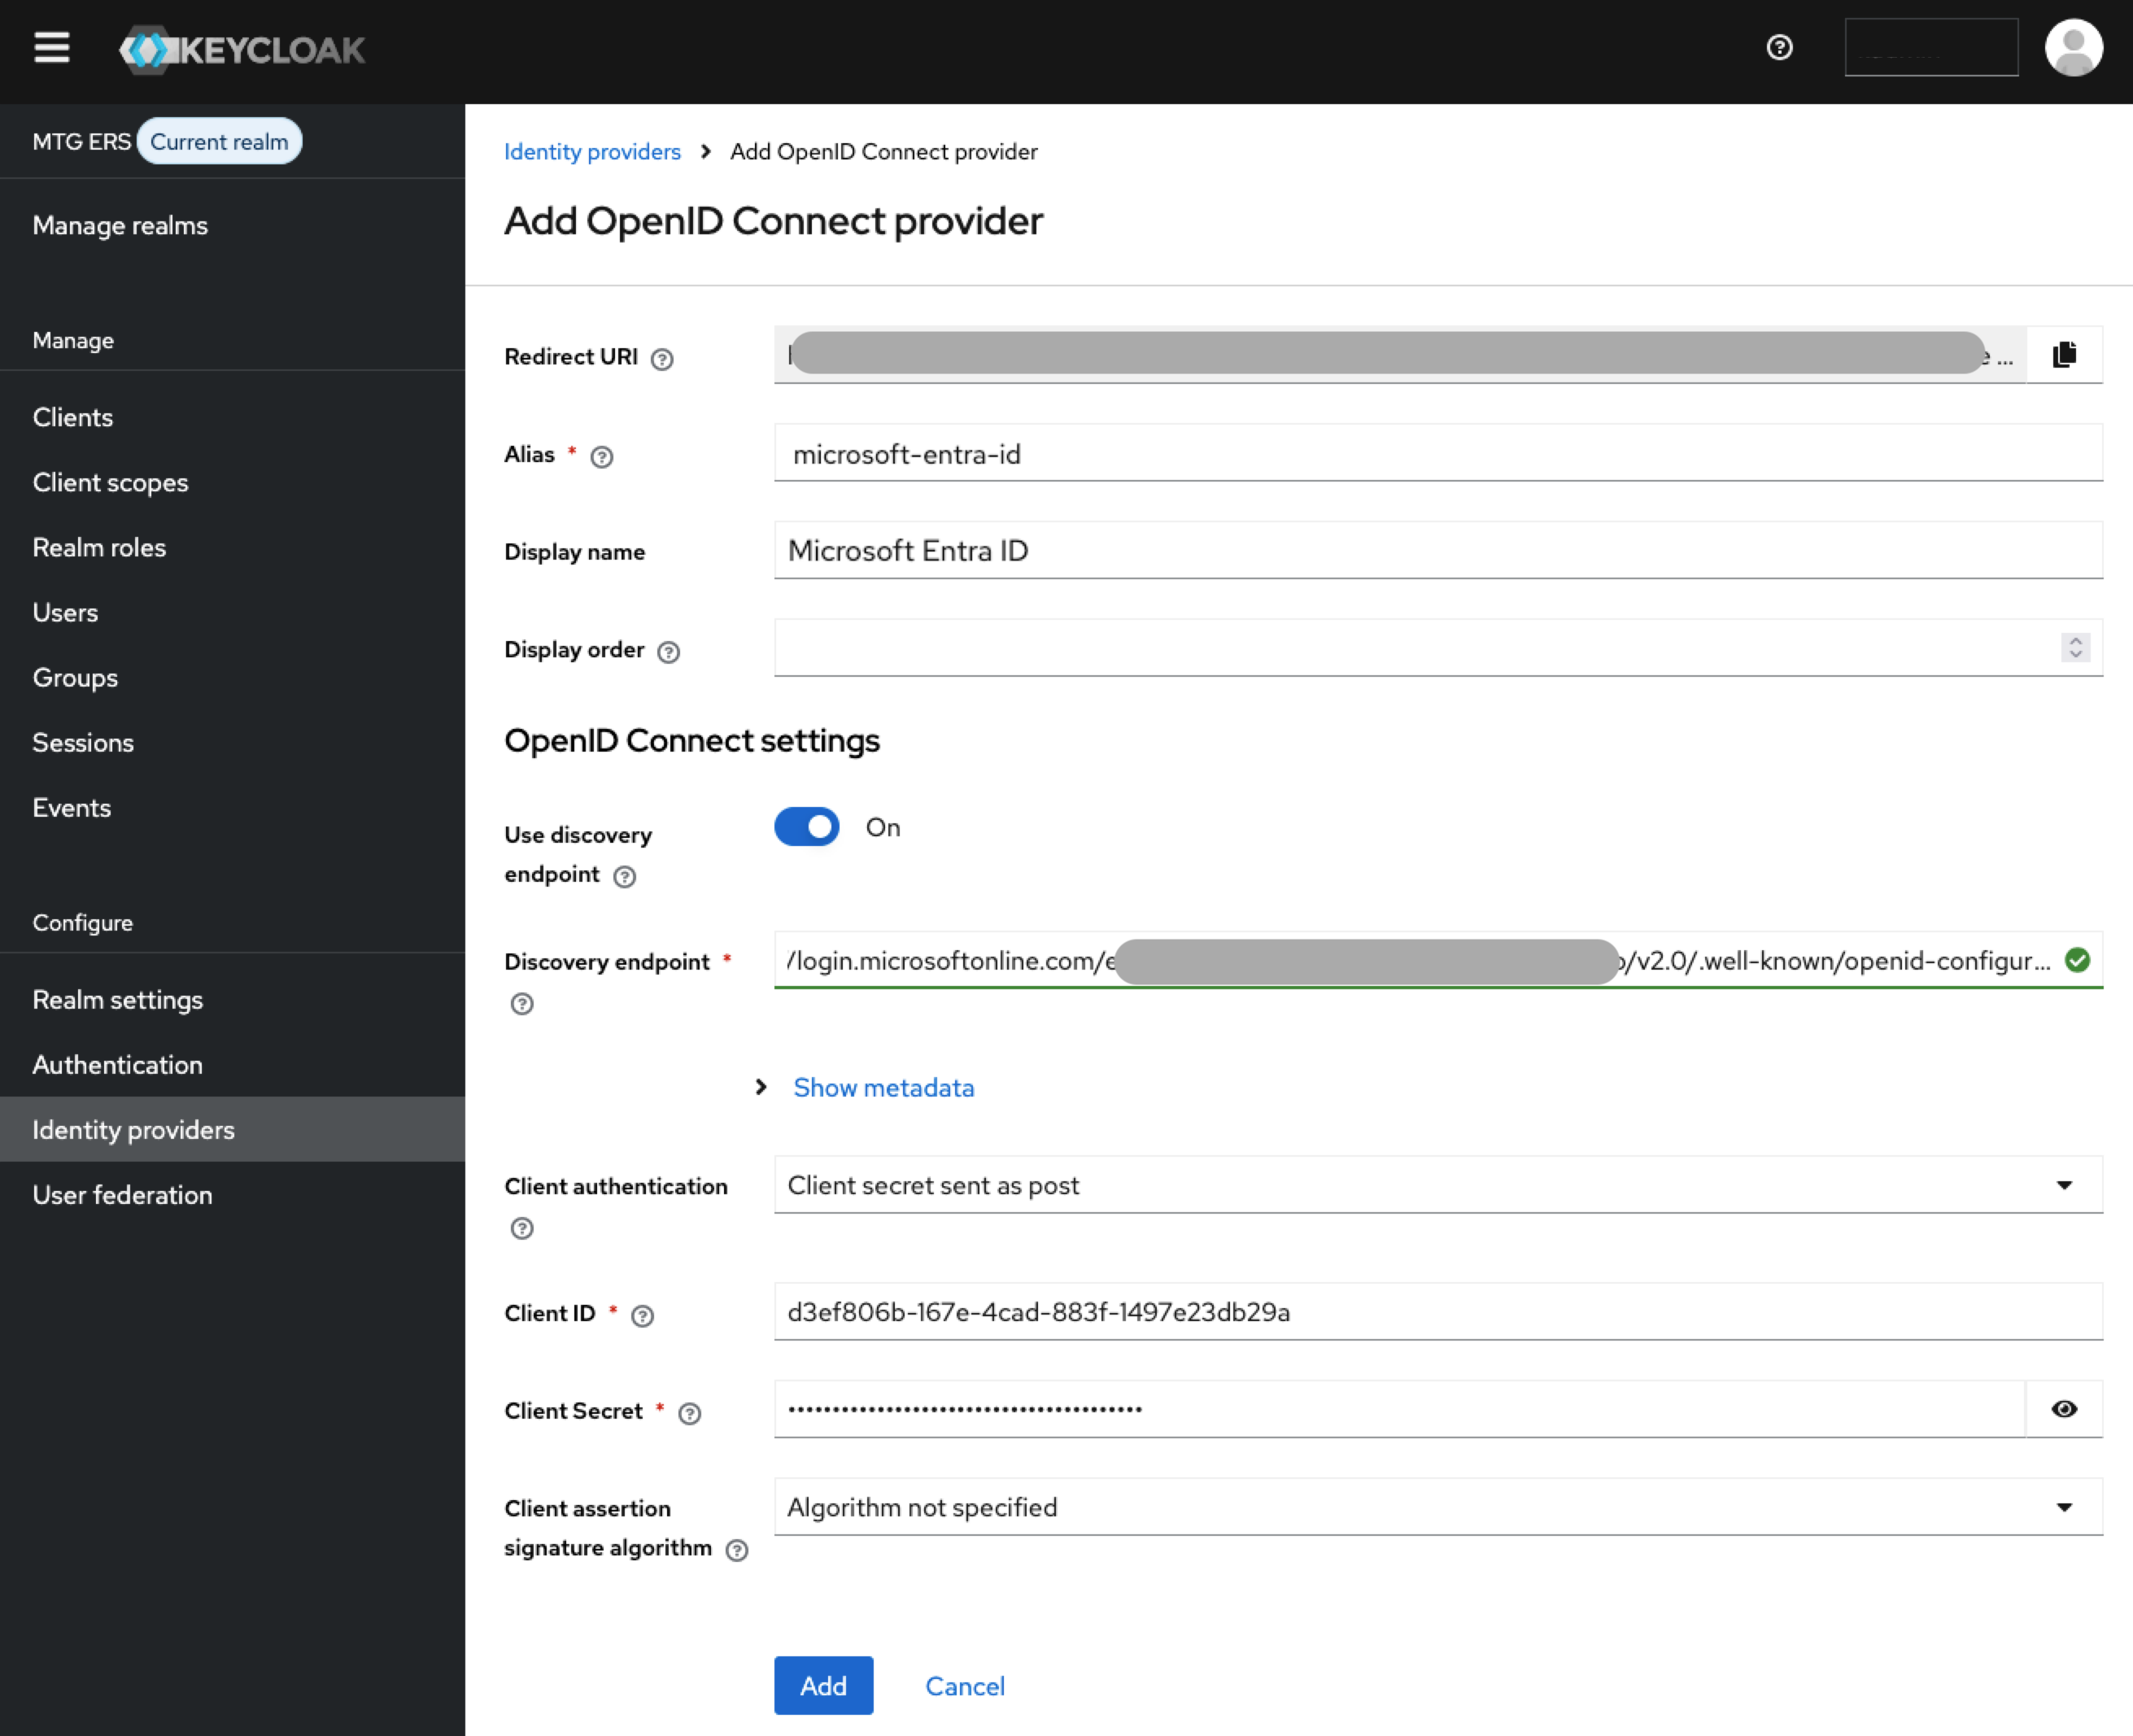
Alias: Enter "microsoft-entra-id" (or organizational standard).
-
Display Name: Enter "Microsoft Entra ID".
Make sure you store your Redirect URI now. You are going to need it later. 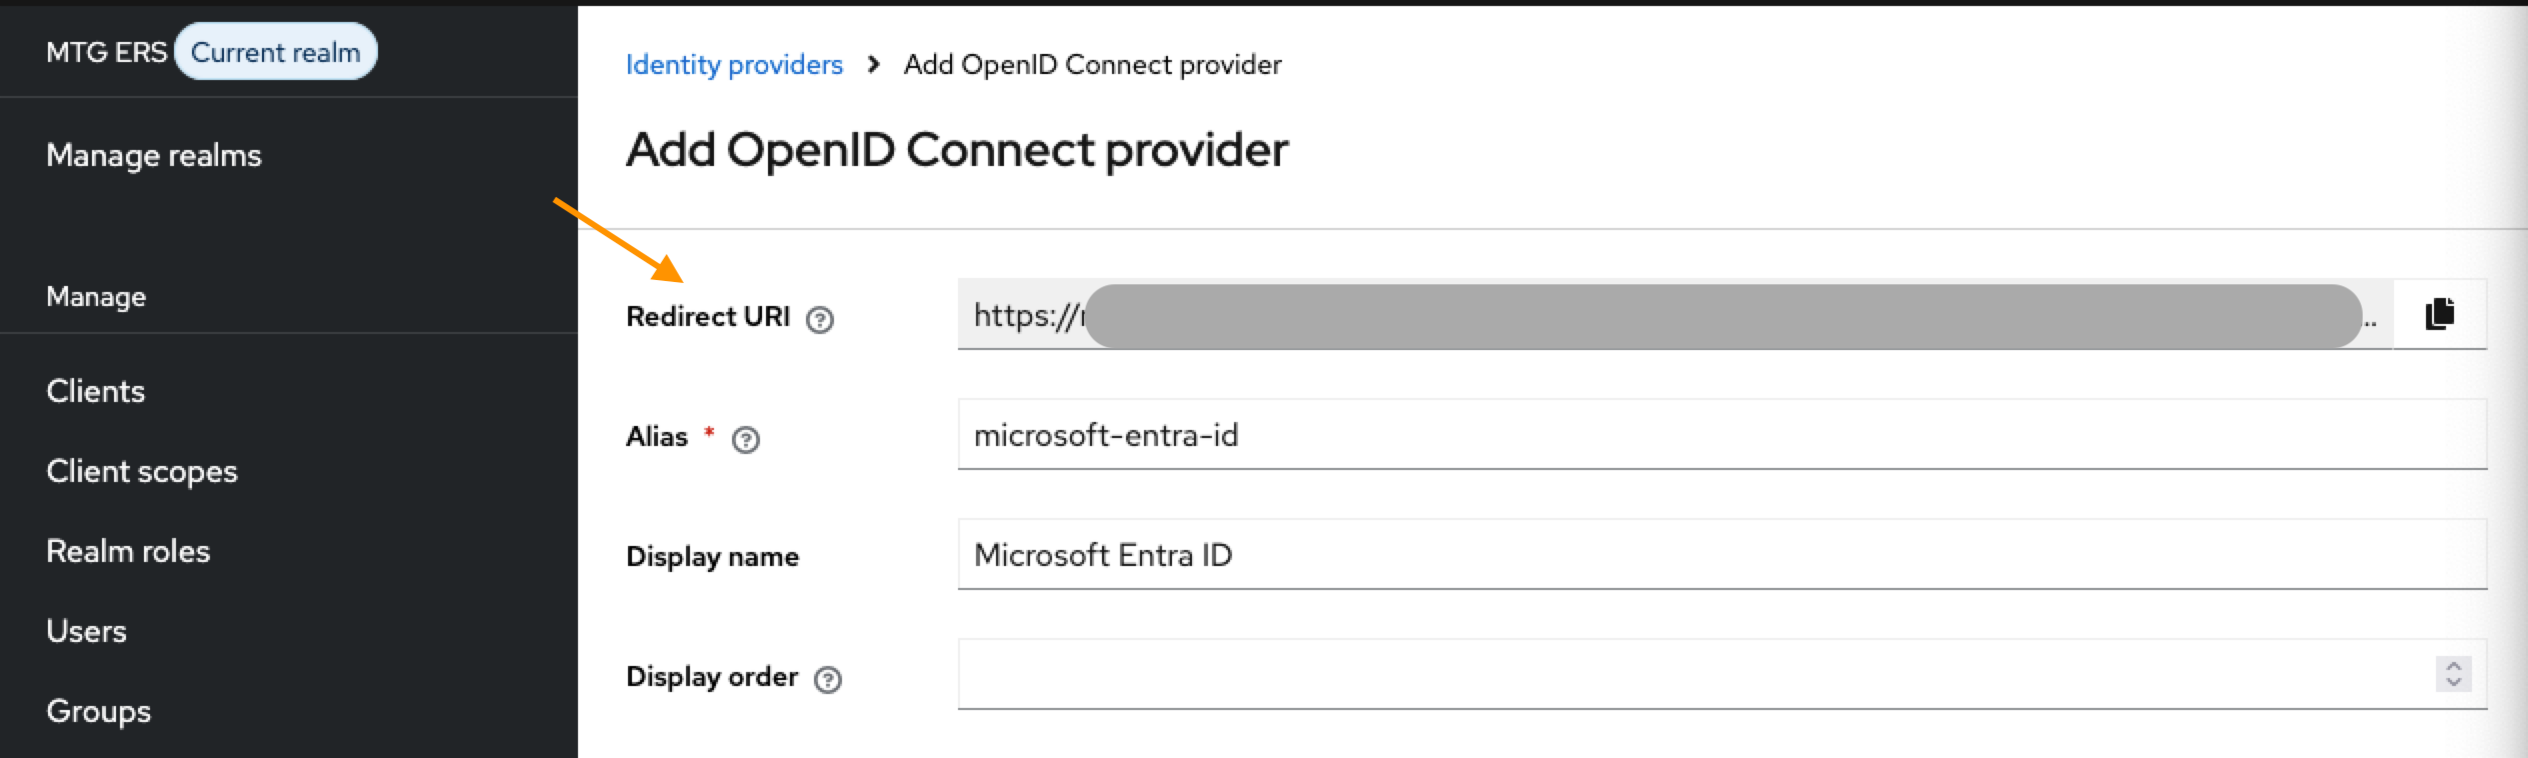
2. OpenID Connect Settings
-
Keep Use discovery endpoint on and retrieve it from portal.azure.com.
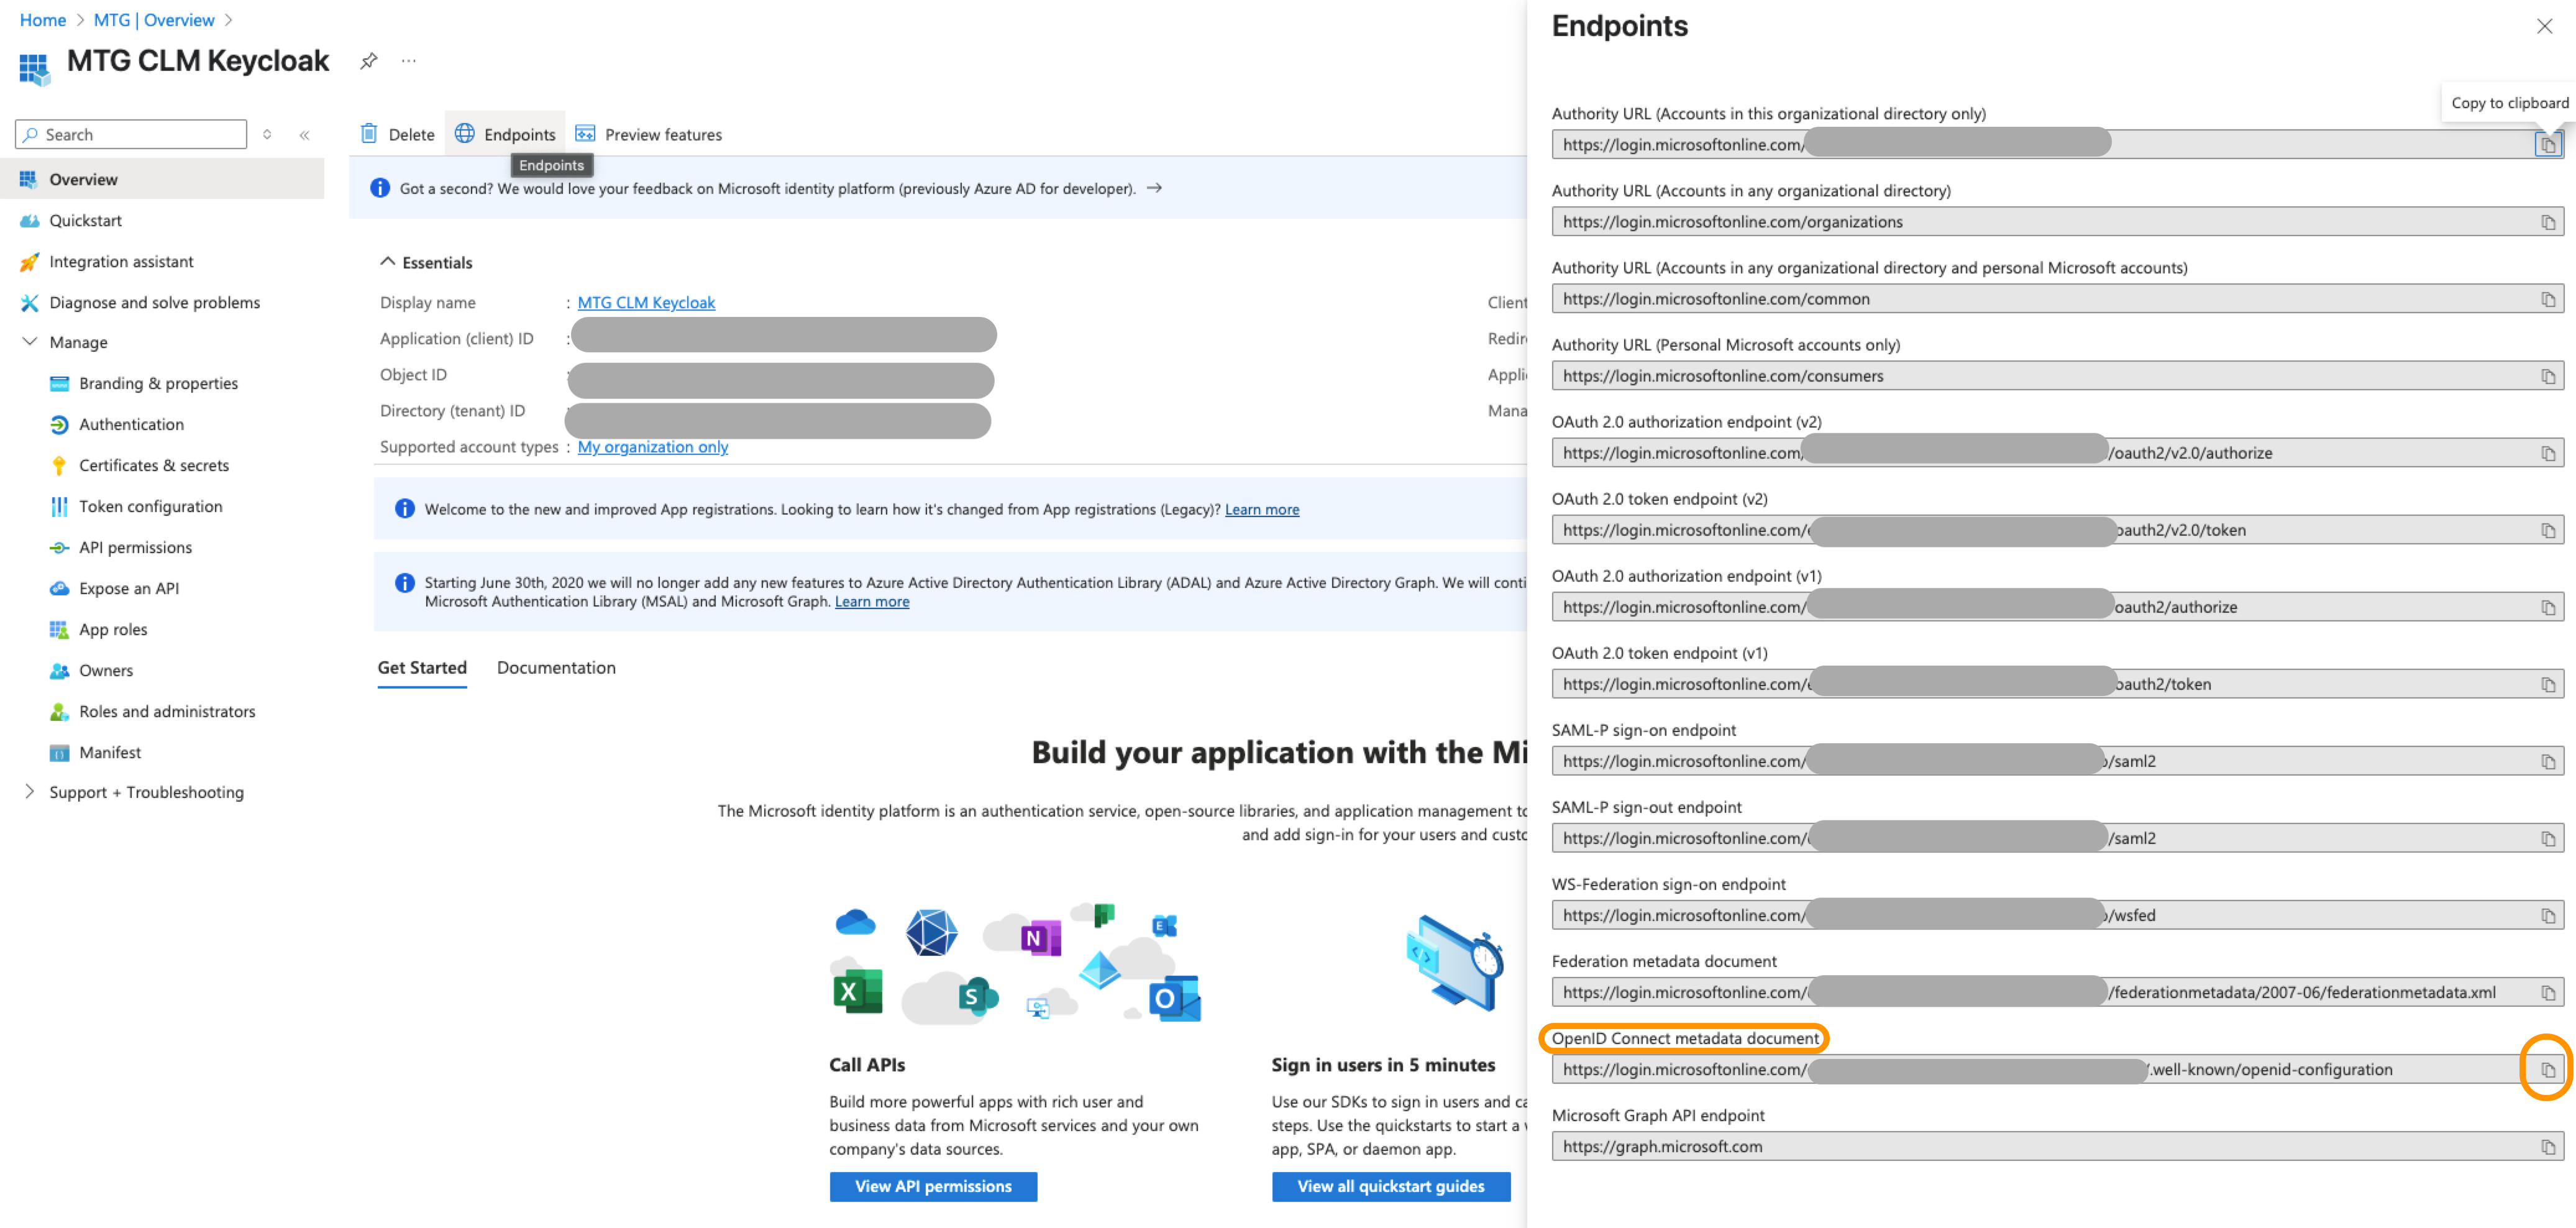
| The metadata fields related to endpoints will be automatically populated upon pasting. |
-
Client Authentication: Select "Client secret sent in the request body" from the dropdown list.
-
Client ID: Retrieve from portal.azure.com → Overview.
-
Client Secret: Retrieve from Generating the Client Secret.
| Make sure to timely renew the client secret before your selected expiration date. |
Paste the Client Secret Value to the appropriate field in Keycloak and keep Client assertion signature algorithm to "Algorithm not specified".
-
The completed page should now look like this:
-
Click "Add" to proceed.
-
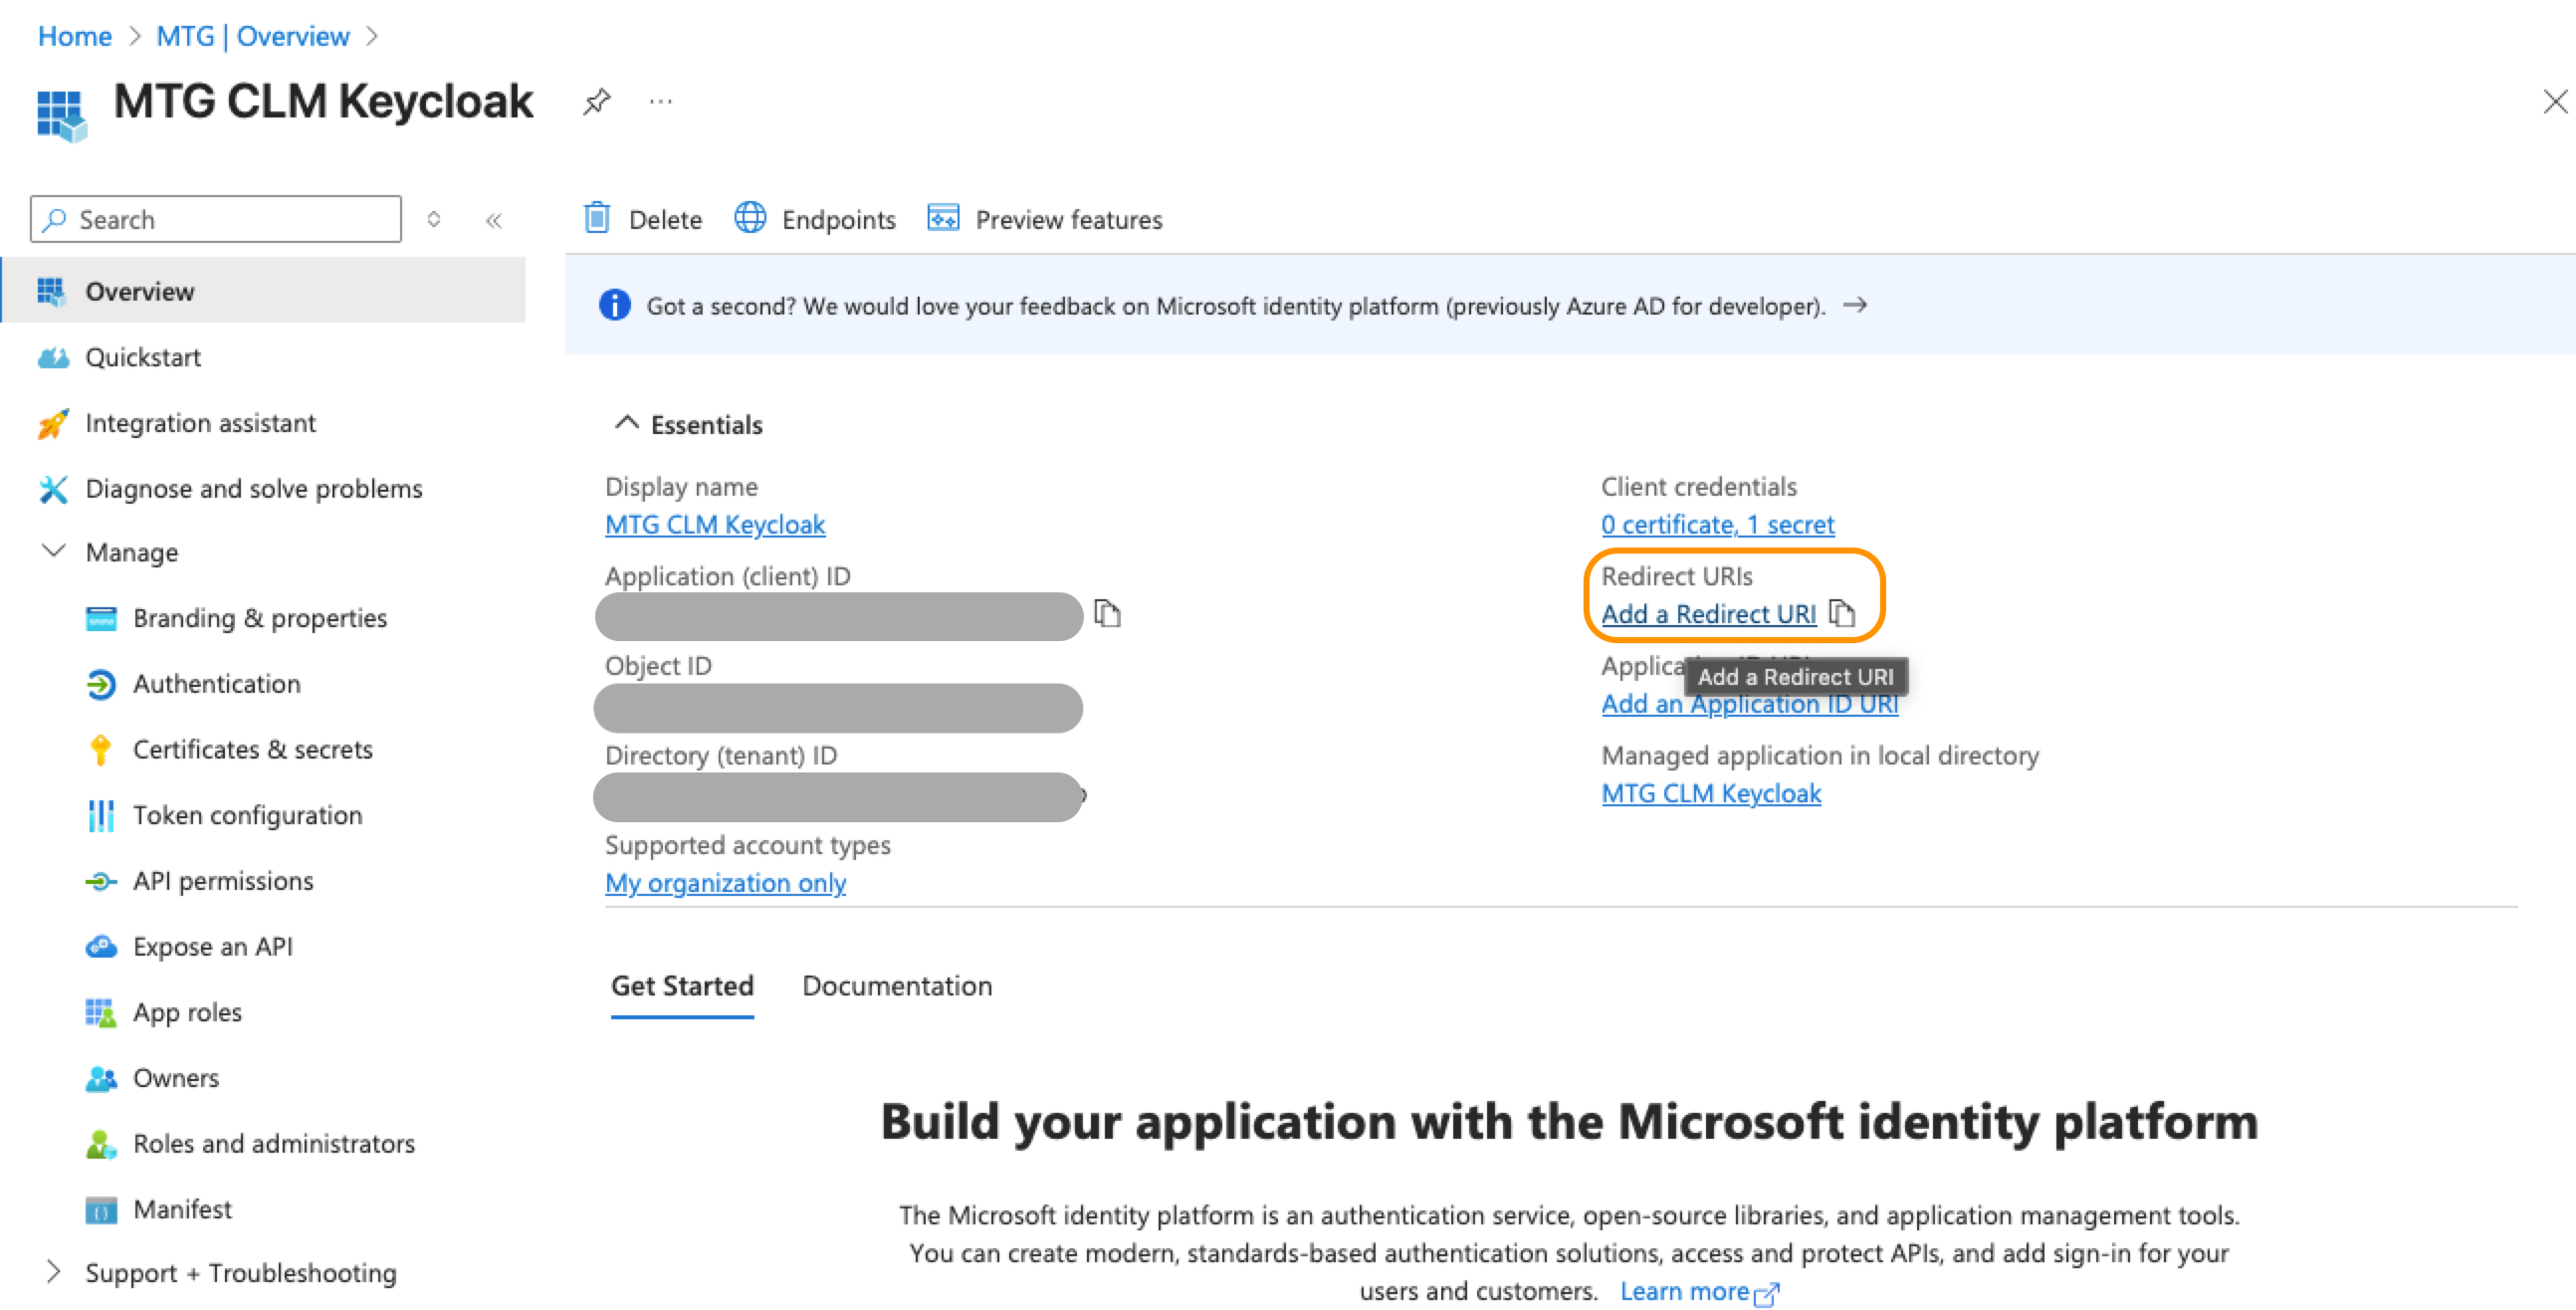
Now copy your redirect URI you saved above and paste it in portal.azure.com
-
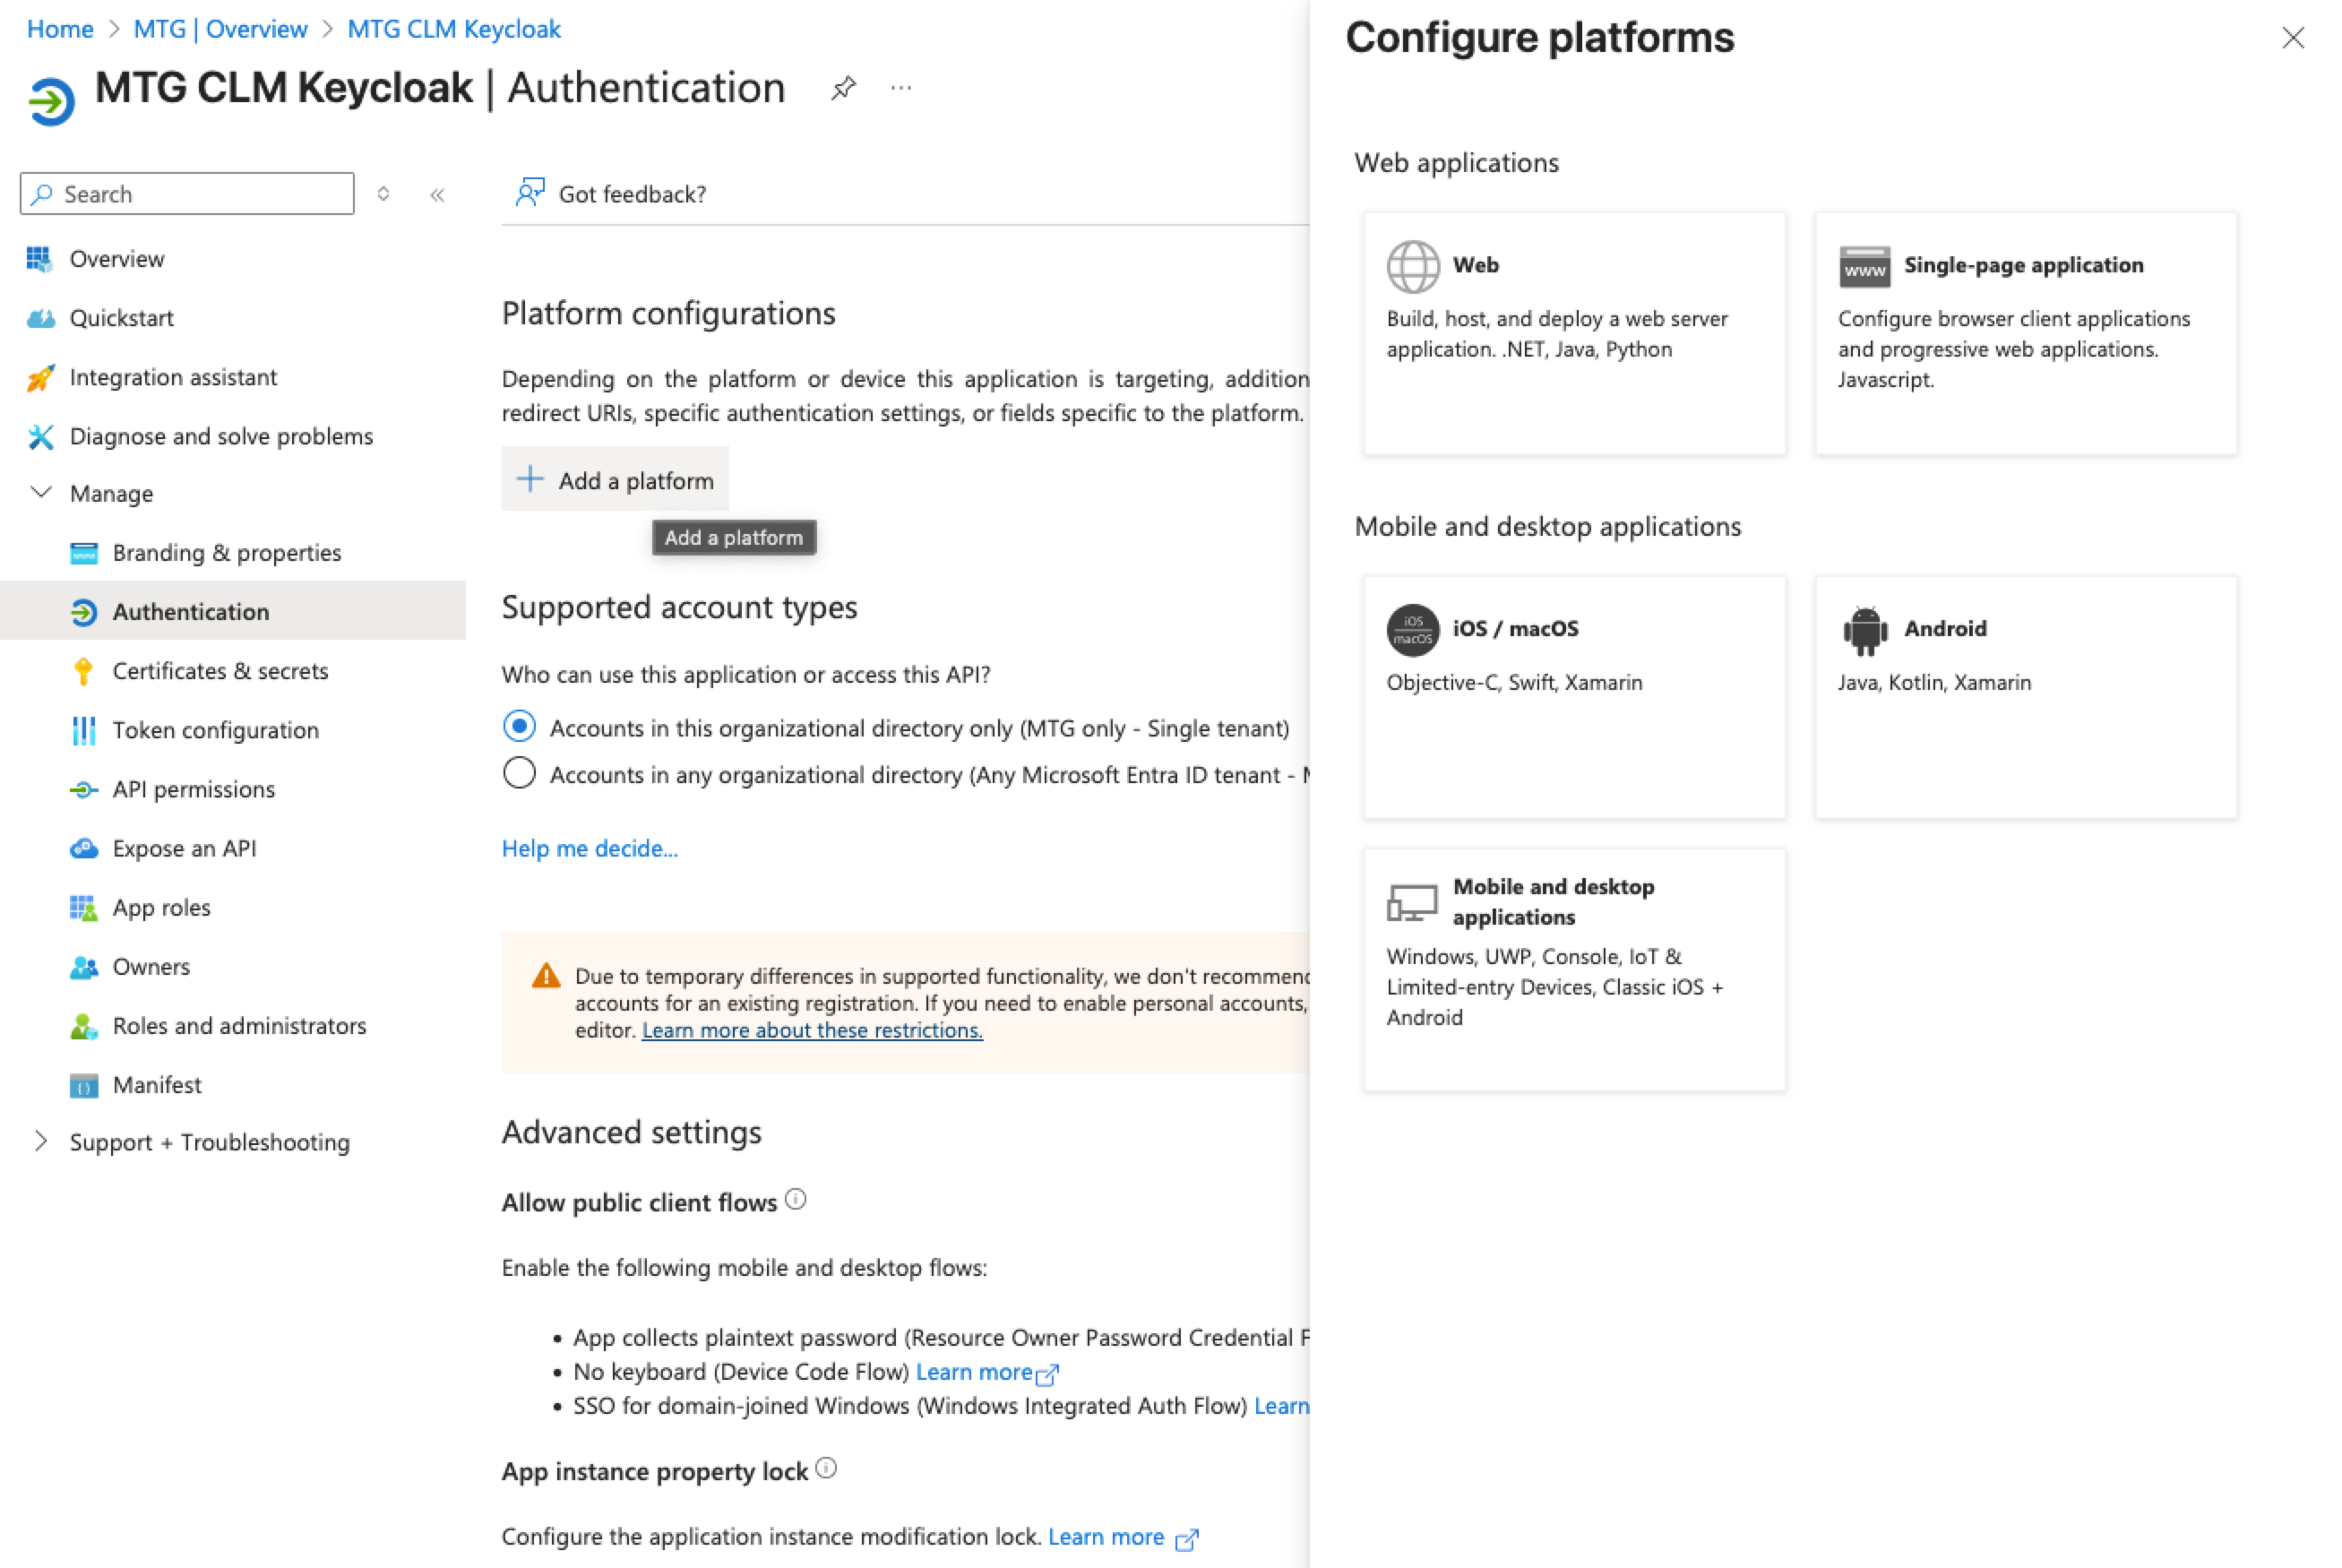
Click "Add a platform" and then select "Web".
-
Paste the Redirect URI in the appropriate field and then select "Configure" to finish.
-
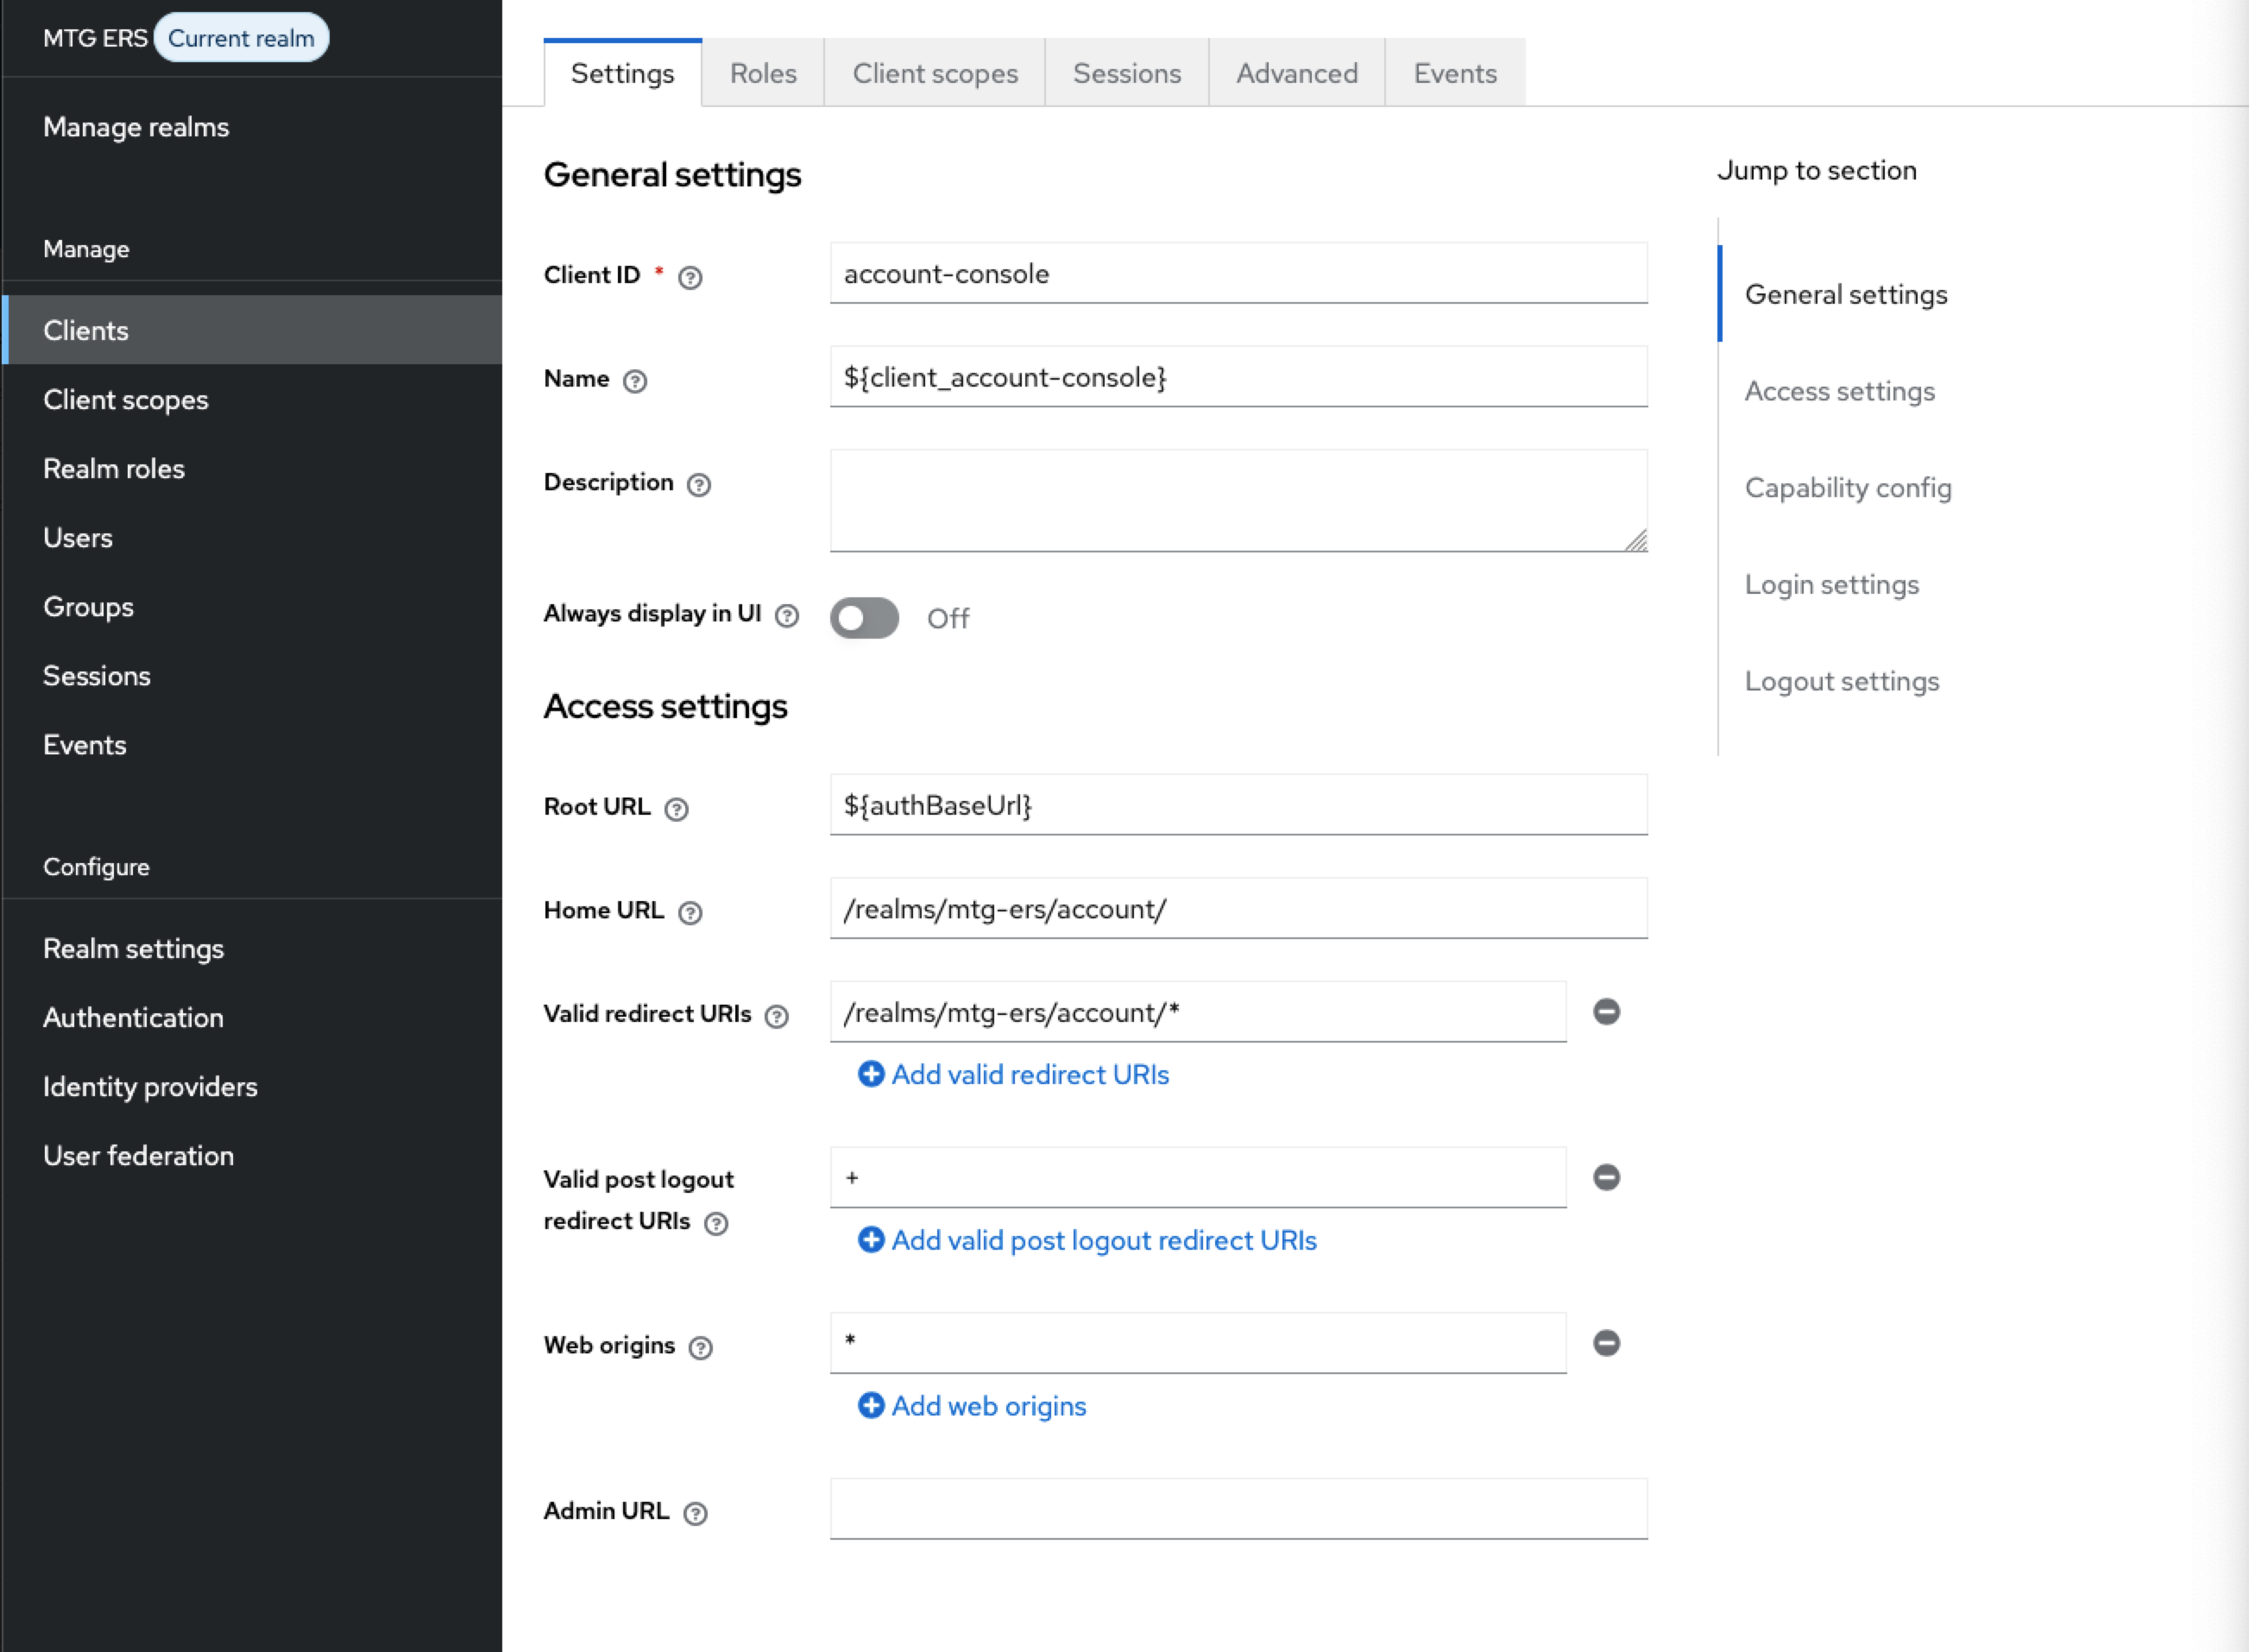
In Keycloak go to Clients (within MTG ERS realm) and choose the account-console client.
-
In Access Settings make sure Web origins is set to "*".
Configuring Keycloak Roles for Entra ID Federation
This section extends the Entra ID authentication configured earlier by mapping Entra ID app roles to Keycloak realm roles.
Use the same Entra ID app registration and Keycloak identity provider configured in the previous sections.
| The identity provider and its redirect URI are already configured. You do not need to create another identity provider or register the same redirect URI again. |
Prerequisites
-
Complete the authentication setup in the previous sections and verify that you can sign in using Entra ID.
-
Ensure you have access to the Azure Portal with permissions to manage app roles and assignments.
-
Ensure you have administrative access to the same Keycloak realm used for authentication.
-
Have an Entra ID test user available.
Defining App Roles in Entra ID
Create the app roles that you want to map to Keycloak realm roles. Use the Entra ID app registration configured in the first part of this guide.
-
Navigate to Microsoft Entra ID → App registrations and select your app.
-
Go to App roles → Create app role.
-
Fill in the following fields:
Field Example Value Notes Display name
CLM AdminHuman-readable label
Value
clm_adminValue that Keycloak will match in the
rolesclaimDescription
Full administrative access to CLMDescription of the intended role
Allowed member types
Users/GroupsAllows assignment to users and groups
-
Click Apply.
-
Repeat to create additional roles as needed, such as
clm_viewer.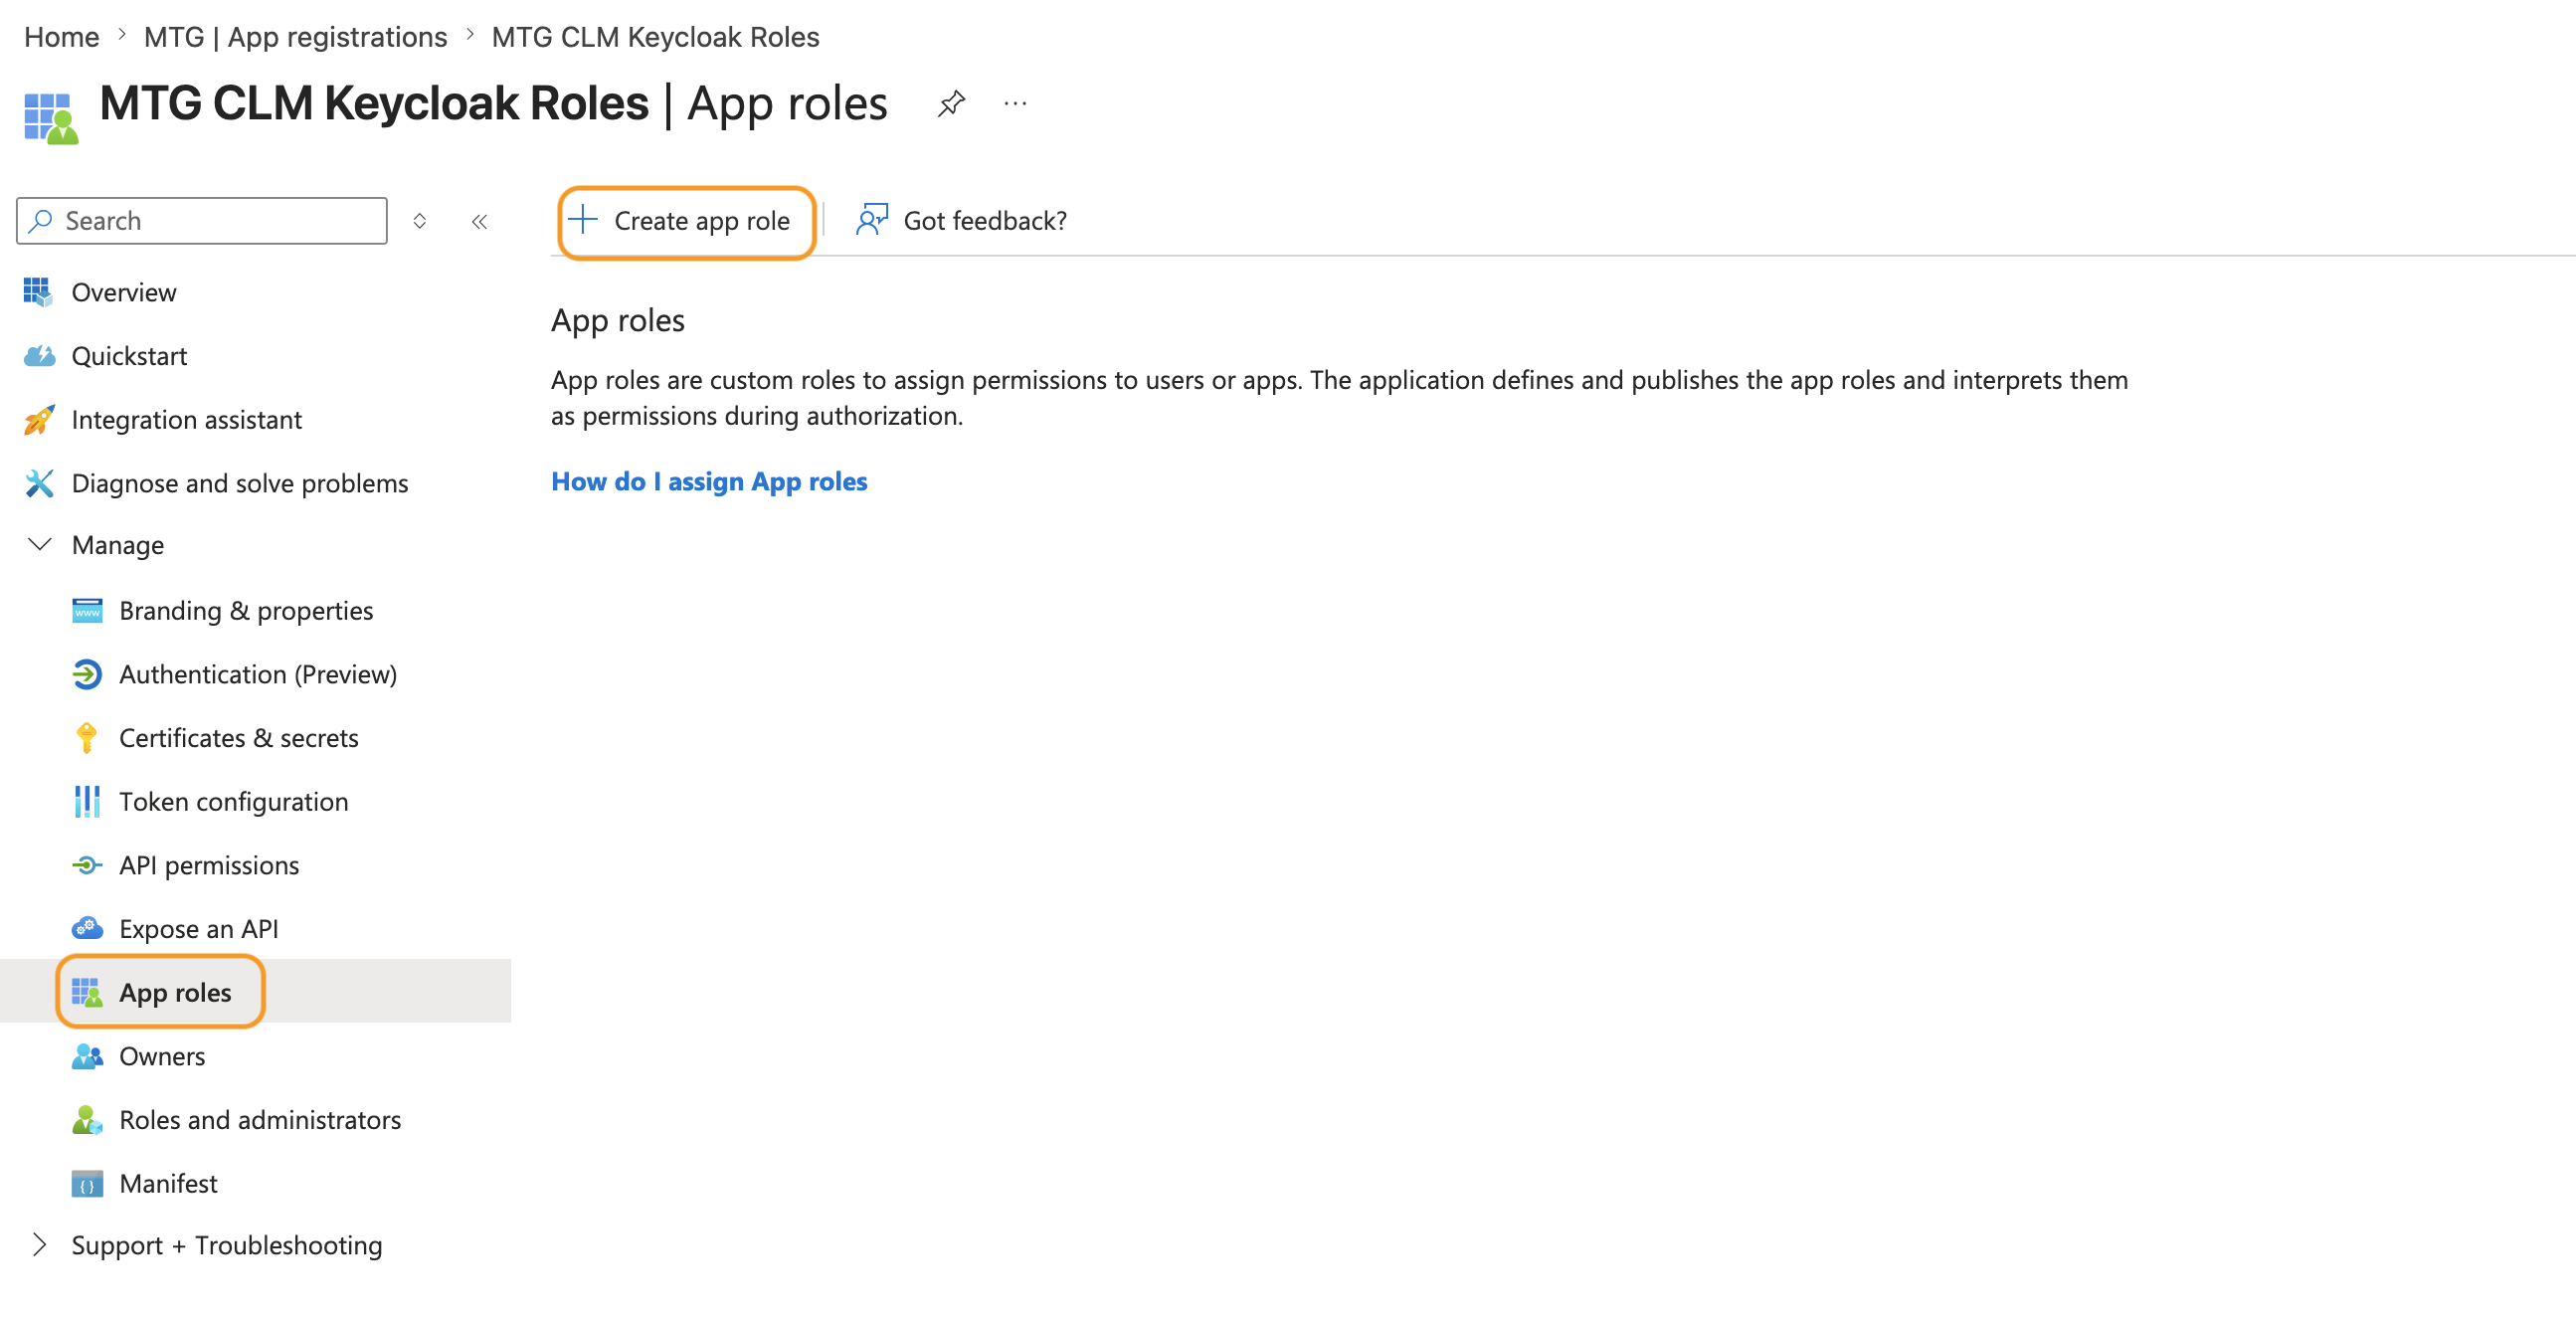
The Value field must exactly match the Claim value configured in the Keycloak mapper. This guide uses lowercase values with underscores as a naming convention. Use clm_admin consistently when following this example.
|
| Creating an Entra ID app role does not itself grant permissions in MTG CLM. The mapped Keycloak role must provide the intended access in your application configuration. |
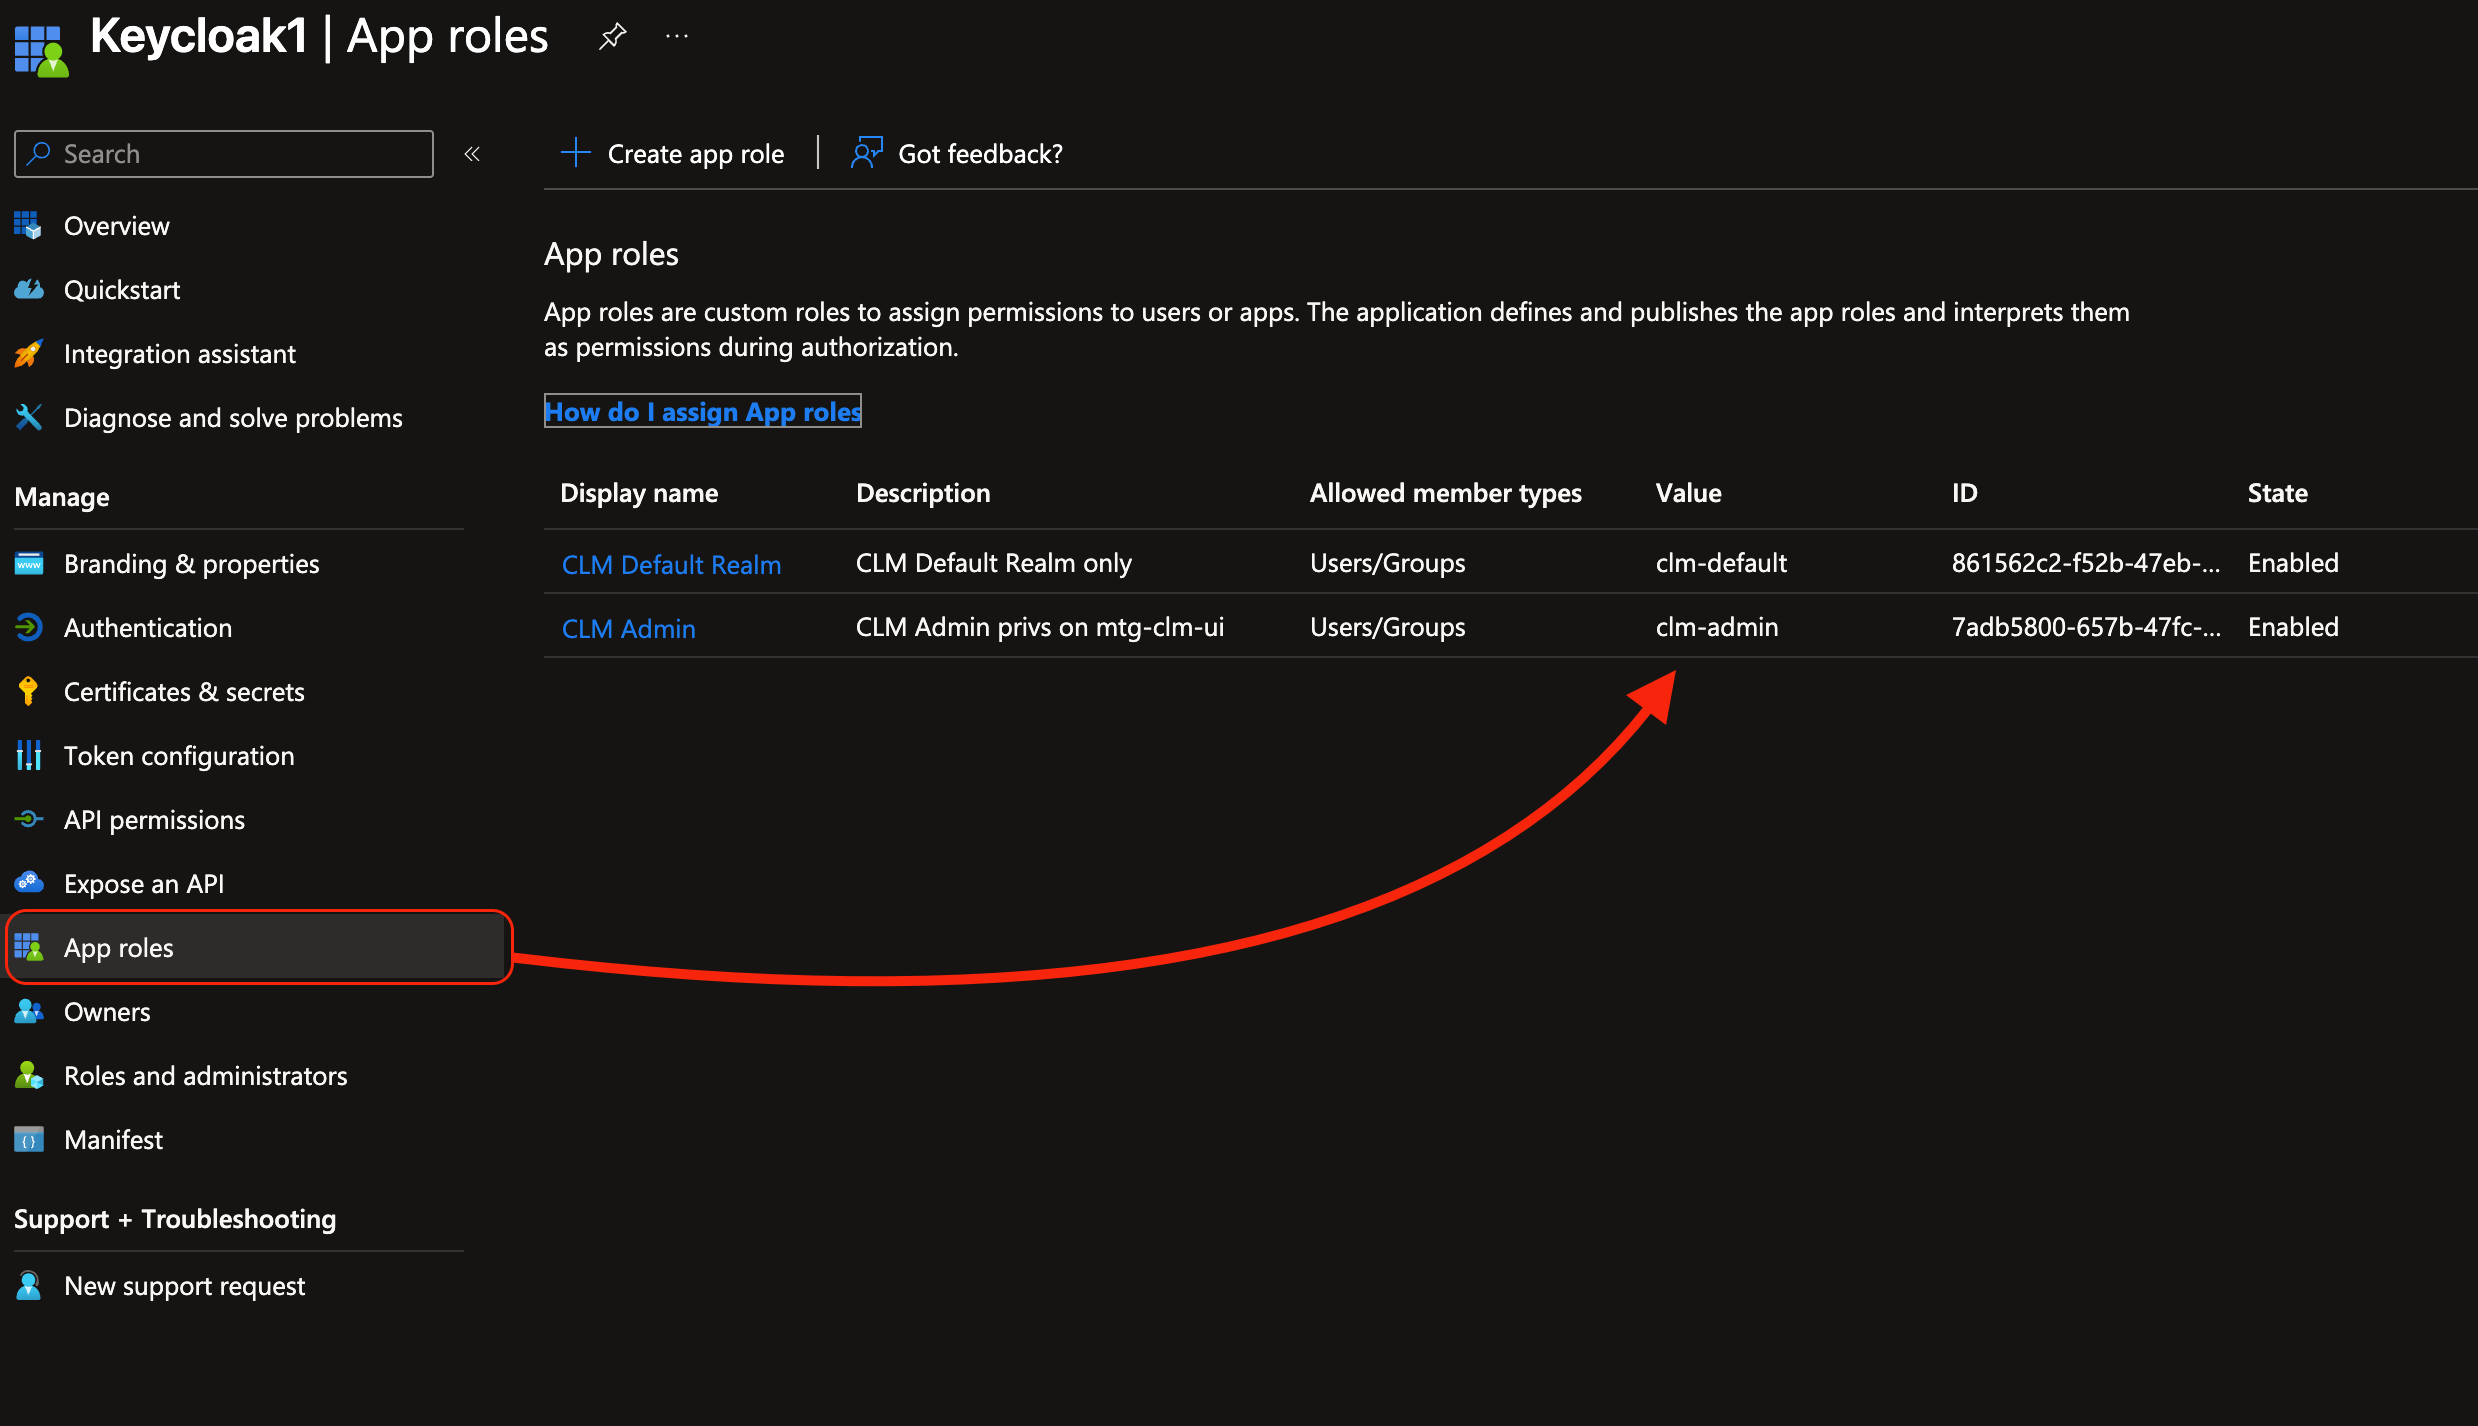
The following screenshot provides an additional example of app roles.
When following this guide, use clm_admin consistently (disregard the clm-admin value shown in the screenshot below).
Assigning the App Role to Your Test User
-
Go to Enterprise applications and select the application associated with the app registration used above.
-
Select Users and groups → Add user/group.
-
Under Users, search for and select your test user.
-
Under Select a role, choose the role you created, such as
CLM Admin. -
Click Assign.
| Verify that your test user appears in the Users and groups list with the assigned role. |
Accessing the Configured Entra ID Identity Provider
Use the existing OpenID Connect identity provider to configure role mapping.
-
Sign in to the Keycloak administration console.
-
Select the same realm used in the authentication setup.
-
Go to Identity Providers.
-
Open the provider with the alias
microsoft-entra-id, or the alias you chose during setup. -
Confirm that its Client ID matches the Application (client) ID of the Entra ID app registration where you defined and assigned the app roles.
| Keep the existing provider settings and redirect URI. The role mappers configured below will use this connection. |
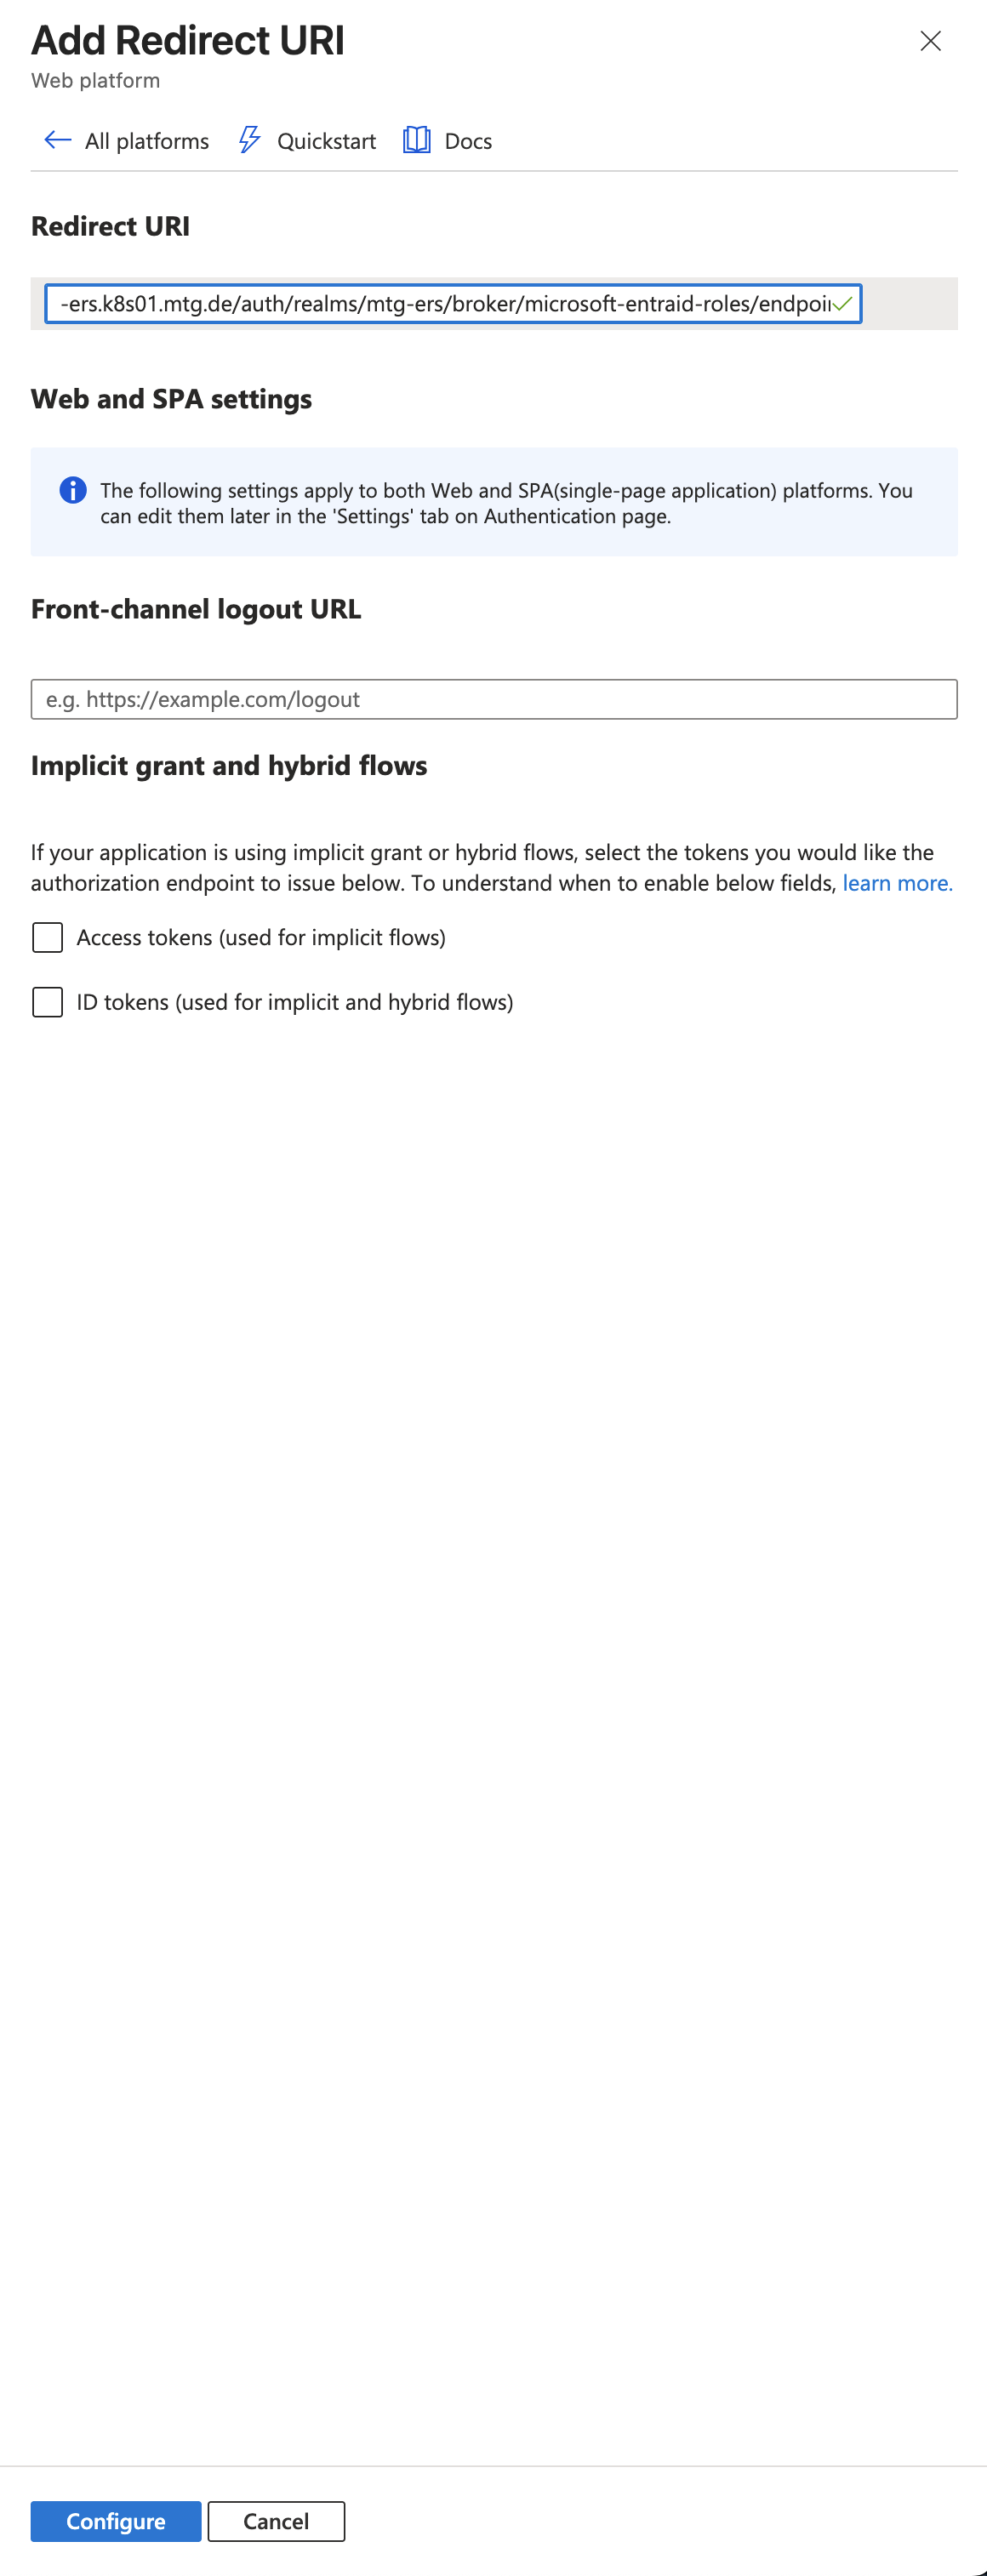
The following screenshot shows where the redirect URI was registered in Entra ID during the initial setup. It is included for reference; you do not need to repeat the registration.
Preparing the Keycloak Realm Role
The target Keycloak realm role must exist before you configure the mapper.
-
In the same Keycloak realm, go to Realm roles.
-
Locate the role that provides the intended access in MTG CLM.
-
If your application configuration requires a new role, create it before proceeding.
The mapper example below uses the Keycloak realm role clm_admin.
If your environment uses a different role name, select that role instead.
The Entra ID app role value and the Keycloak realm role name do not have to be identical. The mapper explicitly connects them. In this example, both are clm_admin.
|
Adding Mappers in Keycloak
-
Go to Identity Providers and open the Entra ID provider configured earlier.
-
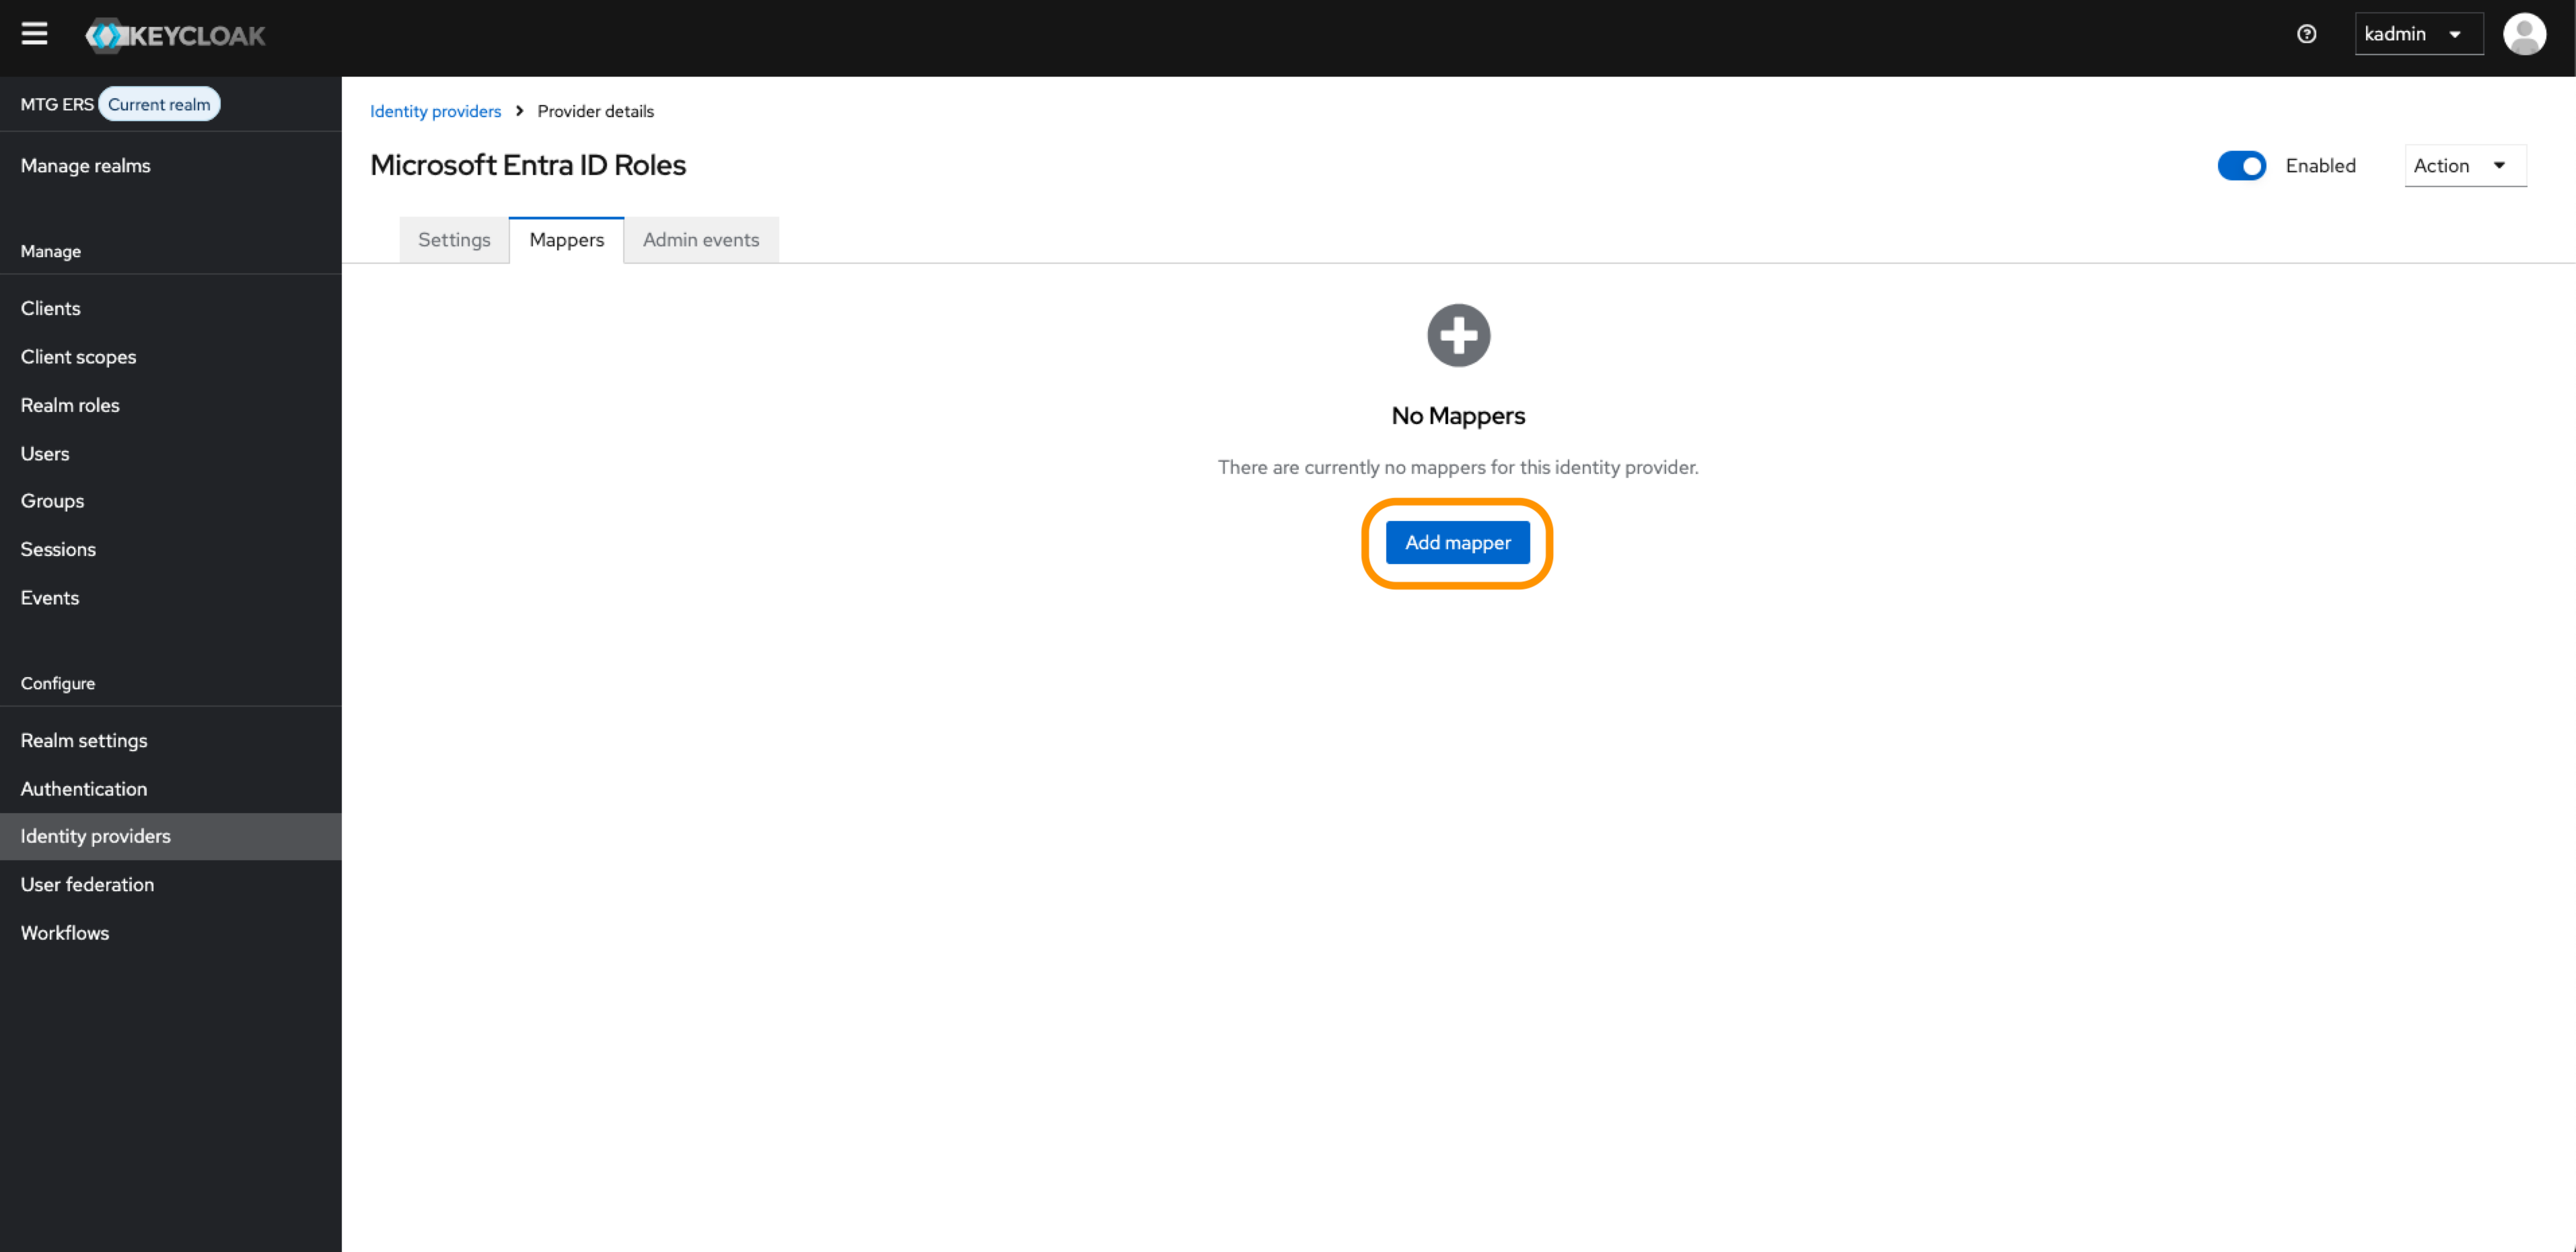
Open the Mappers tab.
-
Click Add mapper.
-
Configure the mapper:
Field Value Name
AdminsMapper type
Claim to RoleClaim
rolesClaim value
clm_adminRole
Select the Keycloak realm role
clm_admin, or the appropriate existing role for your environmentSync mode override
Force -
Save the mapper.

-
Repeat for any additional app roles that you want to map.
This mapper assigns the selected Keycloak realm role when the Entra ID token contains clm_admin in its roles claim.
|
| Match the Claim value to the Entra ID app role Value exactly. If a screenshot shows a different example value, use the values defined in your own configuration. |
The mapper does not create or assign app roles in Entra ID. Define those roles and assign them to the appropriate users or groups in Entra ID before testing.
Verifying Federation and Role Assignment
Test the existing connection and the new mapper together by completing a fresh federated sign-in.
-
Log out of the test user’s Keycloak session.
-
Open a new private or incognito browser session.
-
Navigate to the account console for the realm used throughout this guide:
https://<keycloak-host>/realms/<realm-name>/account
-
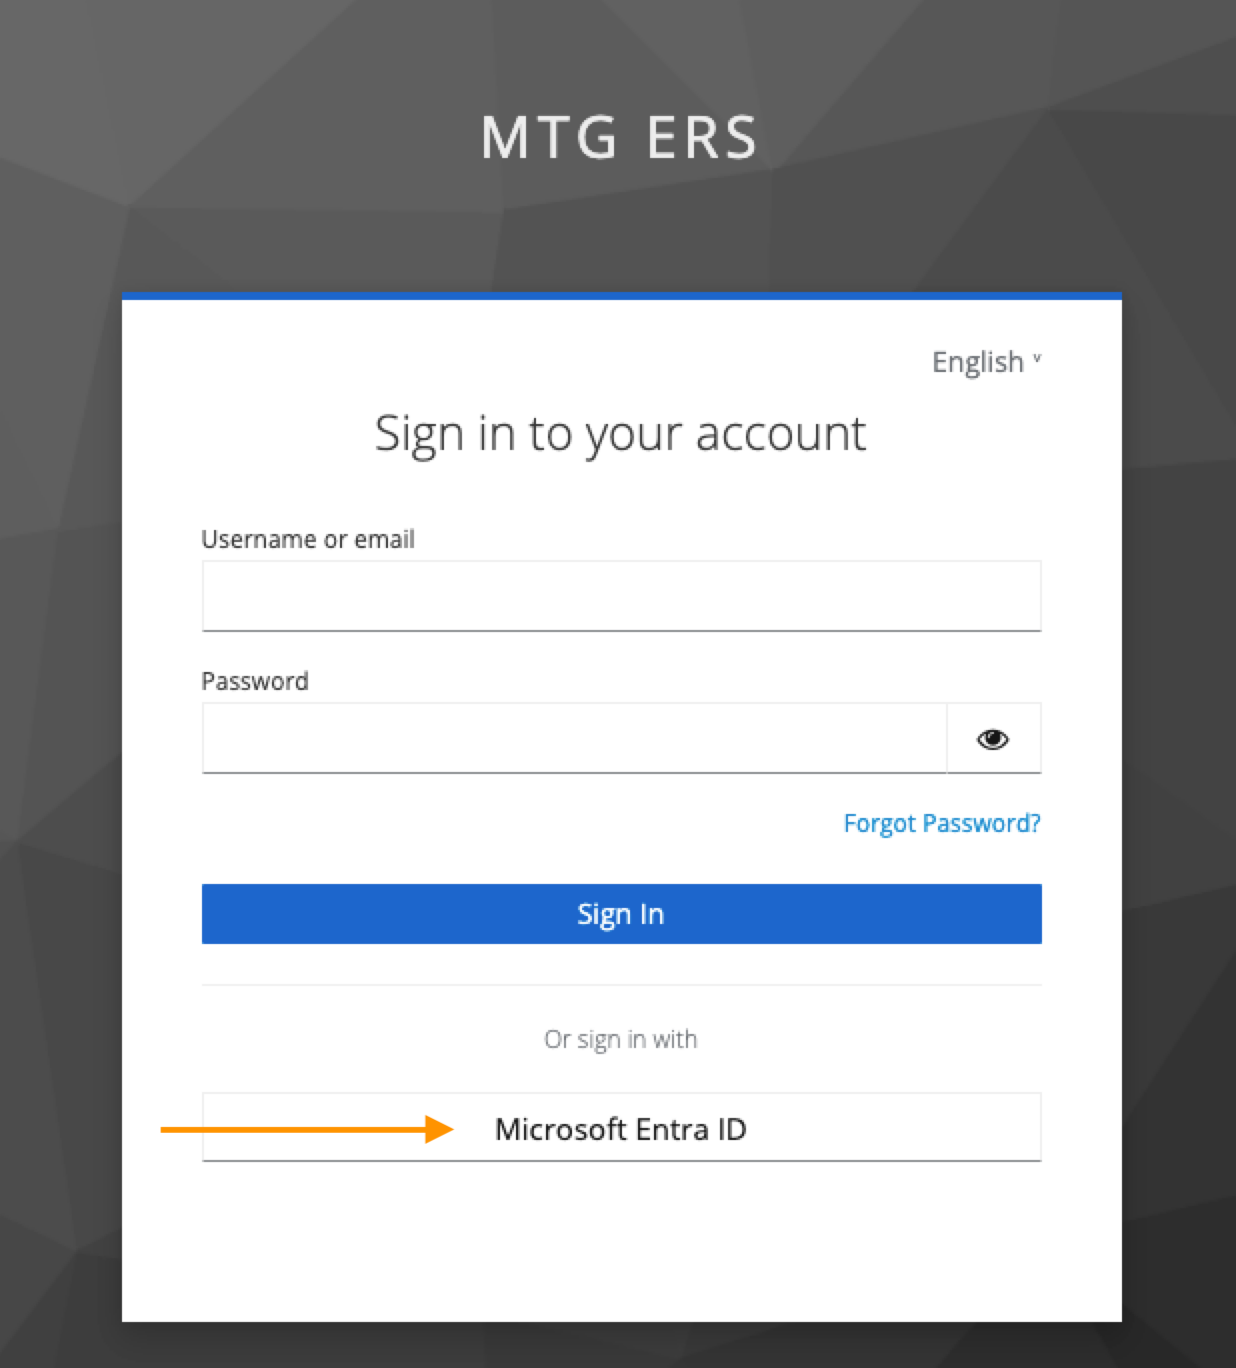
Select the sign-in option for your Entra ID provider. Its display name was configured as
Microsoft Entra ID, unless you chose another name. -
Sign in with the Entra ID test user to whom you assigned the app role.
-
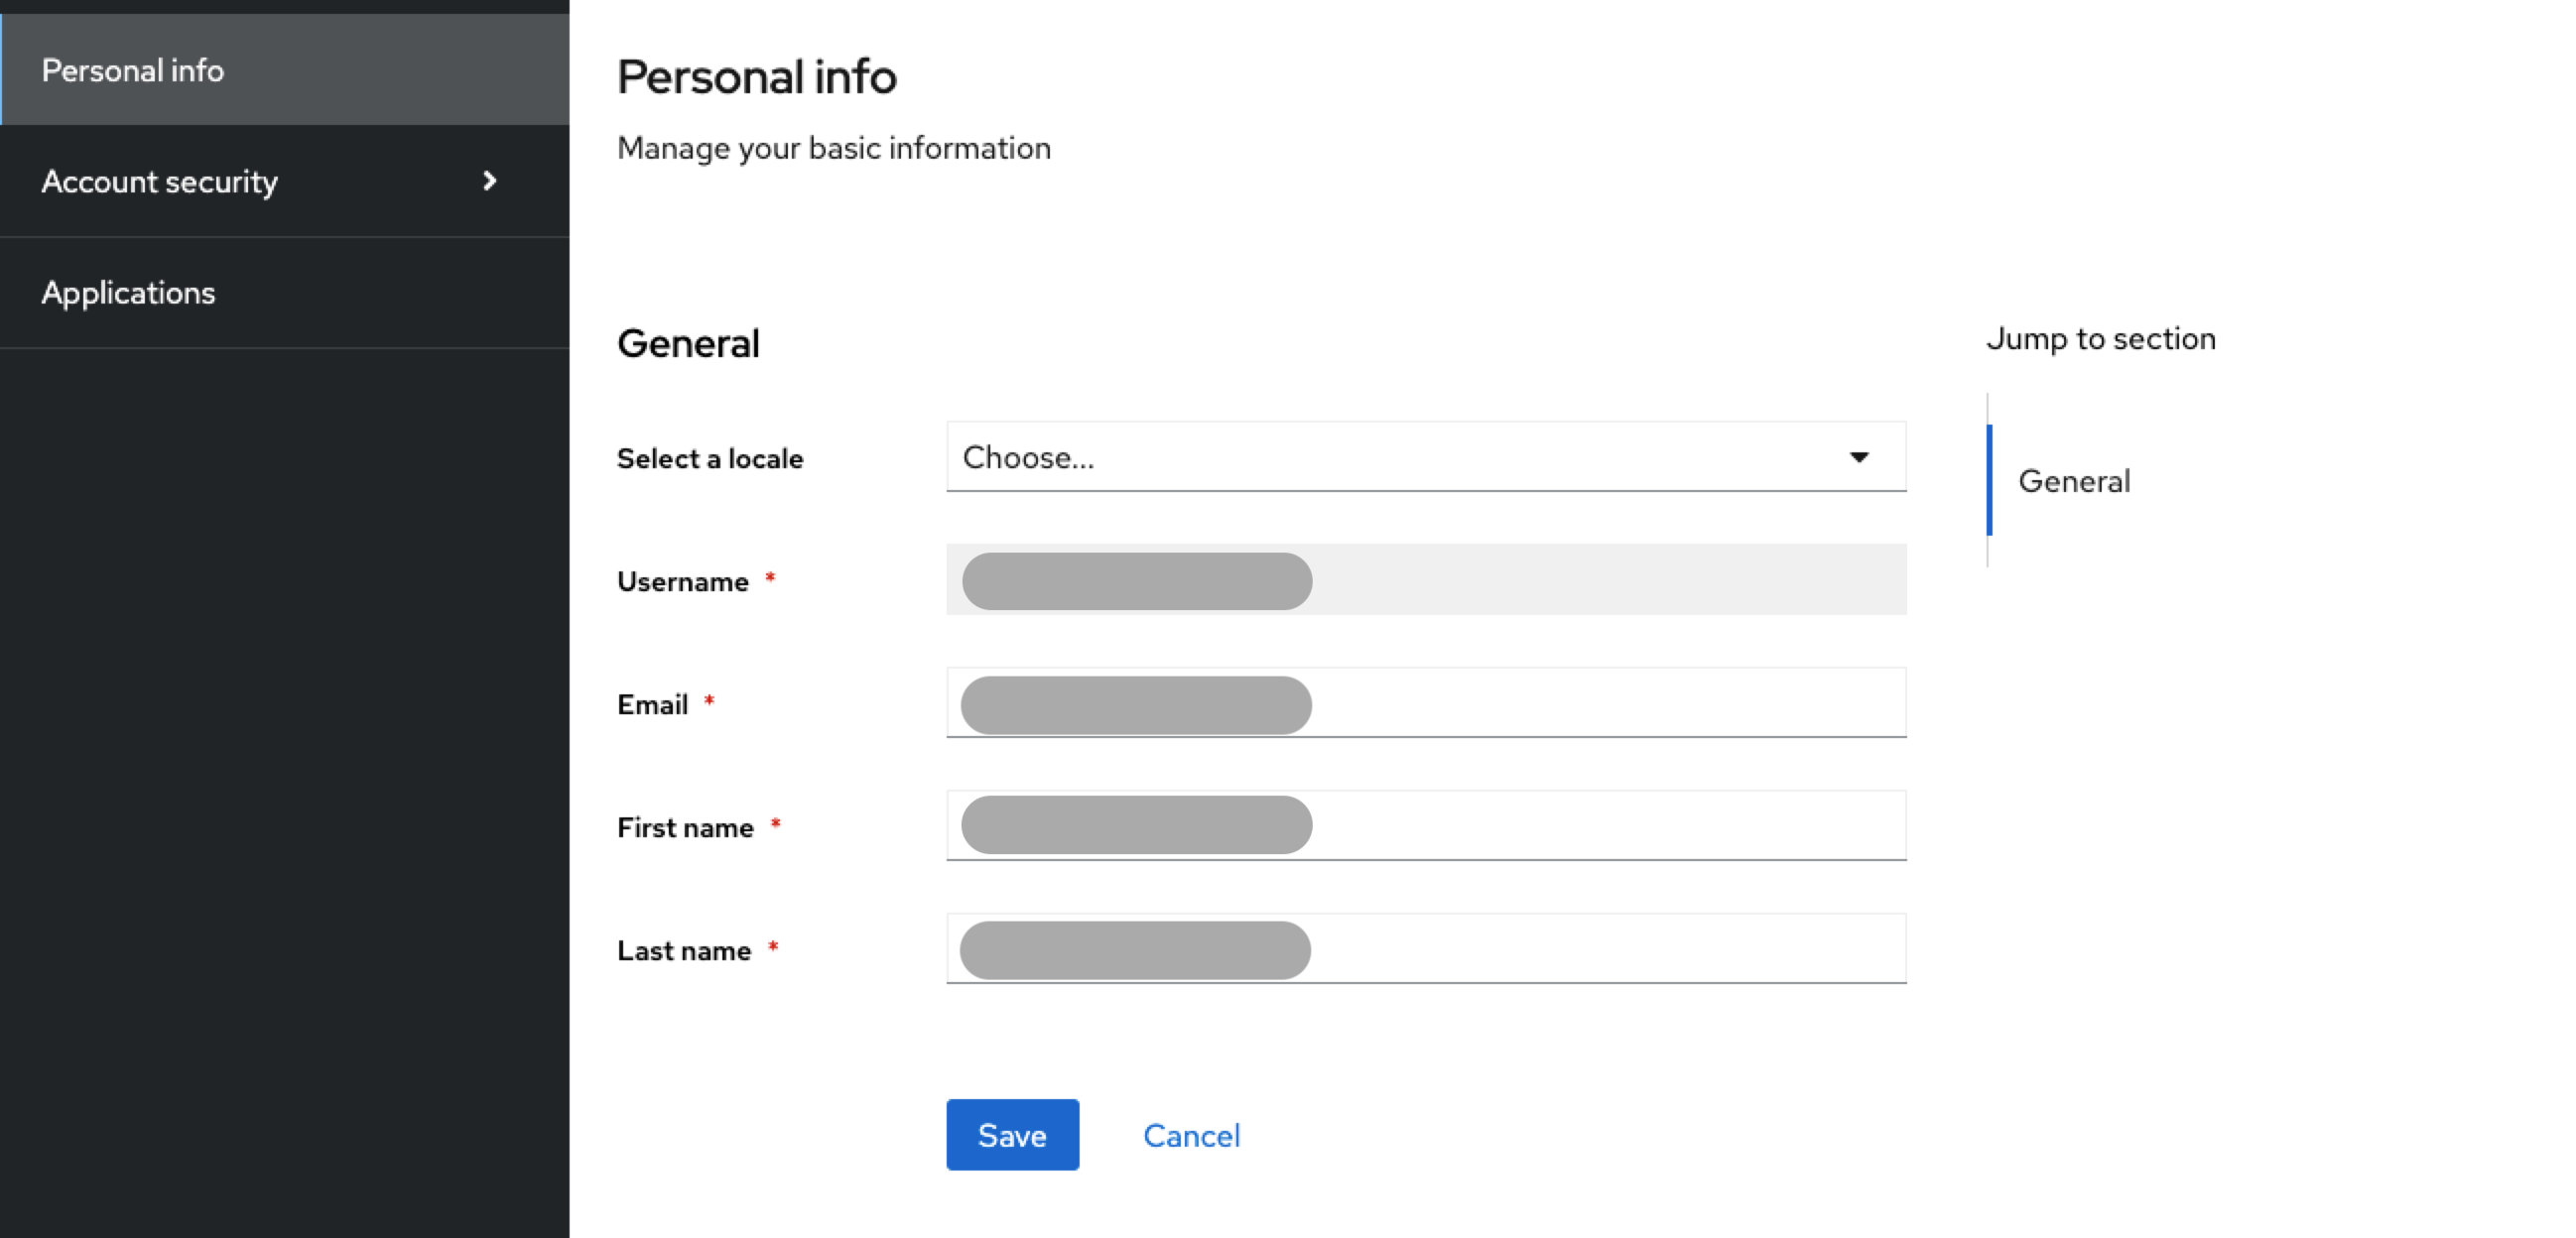
Confirm that you reach the Keycloak account console.
-
In your regular browser window, open the Keycloak administration console.
-
Go to Users and select the test user.
-
Open Role mapping and confirm that the role selected in the mapper, such as
clm_admin, is assigned. -
Sign in to MTG CLM as the test user and verify that the user has the intended application access.
| Confirming a role assignment in Keycloak verifies the mapper’s result. Checking access in MTG CLM also verifies that the application uses the assigned role as intended. |
Troubleshooting Redirect Connectivity
If the browser times out after Microsoft sign-in, check whether it can reach the Keycloak callback address.
-
Open
<keycloak-host>;in the same browser. -
If Keycloak is available only on an internal network, connect to the required network or VPN.
-
Confirm that the redirect URI registered in Entra ID exactly matches the URI displayed by the existing Keycloak identity provider.
Keycloak does not have to be publicly accessible if the user’s browser can reach it through the required network.
A localhost redirect can work when the browser and Keycloak run on the same machine and the redirect URI is registered correctly.
If the browser runs on another machine, localhost refers to that machine instead of the Keycloak server.
If live federation cannot be tested, the manual check below can verify direct role assignment separately.
Manual Role Assignment Check (If Live Federation Is Unavailable)
Use this check only to test direct Keycloak role assignment and, where local sign-in is available, the application’s handling of that role.
This check does not verify Entra ID authentication, the roles claim or the identity provider mapper. Complete the federated sign-in test when the connection becomes available.
|
-
In the Keycloak administration console, select the same realm used throughout this guide.
-
Go to Users and select a dedicated local test user, or create one using Add user.
-
Open the user’s Role mapping tab.
-
Assign the target realm role, such as
clm_admin. -
Confirm that the role appears in the user’s role assignments.
-
If local authentication is enabled and the test user has the required credentials, sign in to MTG CLM with that user and check the resulting access.
Use a separate local test user so that a manually assigned role cannot be mistaken for a role assigned by the Entra ID mapper.
Troubleshooting
| Issue | Checks |
|---|---|
No Entra ID sign-in option on the Keycloak login page |
|
Redirect URI mismatch |
|
Browser times out after Microsoft sign-in |
|
Sign-in succeeds but the expected Keycloak role is missing |
|
Role information appears under user attributes but no realm role is assigned |
|
A mapper for another role does not assign that role |
|
An existing Keycloak account conflicts with the first federated sign-in |
|
A changed Entra ID role assignment is not reflected in Keycloak |
|
Multiple Entra ID identity providers exist in the realm |
|
The role is assigned in Keycloak but application access is incorrect |
|